INDEPENDENT ENDPOINT EVIDENCE AND TELEMETRY
Your EDR Detects Threats.
vTTAC Helps Reveal the Evidence Behind Them.
Extend endpoint visibility. Enrich security telemetry. Strengthen investigations.
Your endpoint detection and response platform is an essential security control. But security investigations should not depend entirely on whether one detection engine generates an alert.
HAWK vTTAC adds an independent endpoint telemetry and evidence layer designed to help security teams observe activity, enrich investigative context, and identify suspicious behavior that warrants further investigation.
Keep your existing EDR. Strengthen the evidence behind your security decisions.
Why Independent Endpoint Evidence Matters
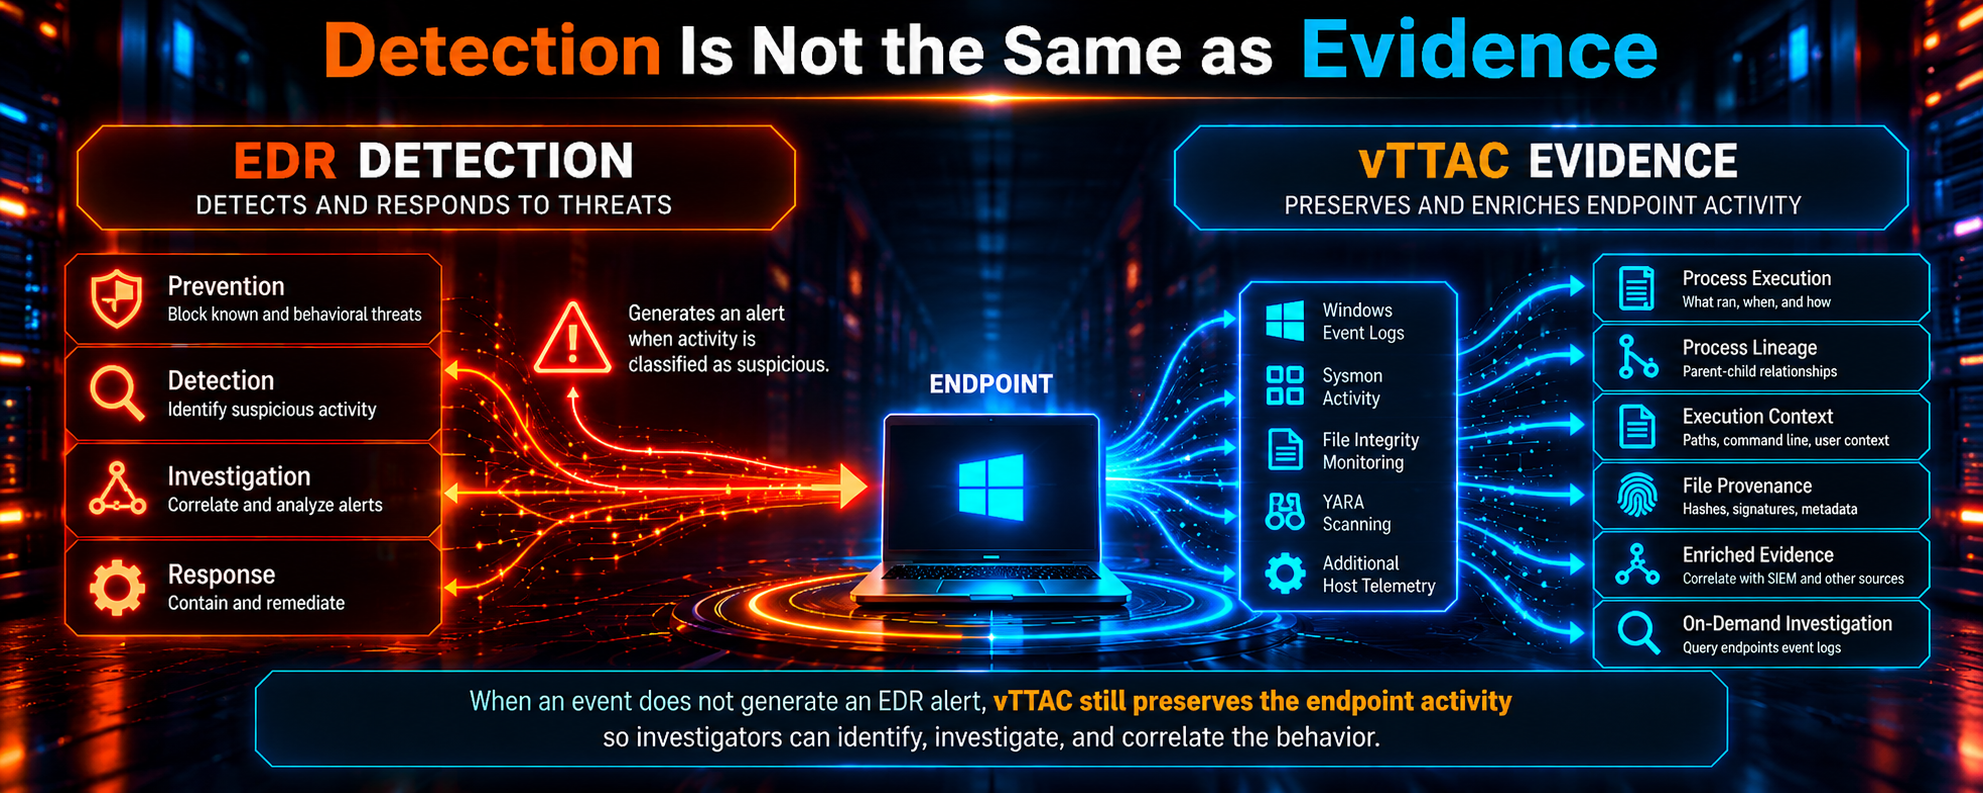
Detection Is Not the Same as Evidence
Modern EDR platforms provide powerful prevention, detection, investigation, and response capabilities.
But an event does not have to generate an EDR alert to become important to an investigation.
Suspicious activity may involve legitimate operating-system tools, unexpected process relationships, unusual execution paths, or sequences of events that become meaningful only when correlated with additional context.
vTTAC provides a complementary telemetry collection path to help preserve and enrich endpoint activity independently of an EDR alert.
That gives investigators another opportunity to understand what happened, examine related behavior, and support their conclusions with evidence.
The objective is not to replace your EDR. It is to reduce dependence on a single detection and analysis path.
How HAWK vTTAC Works
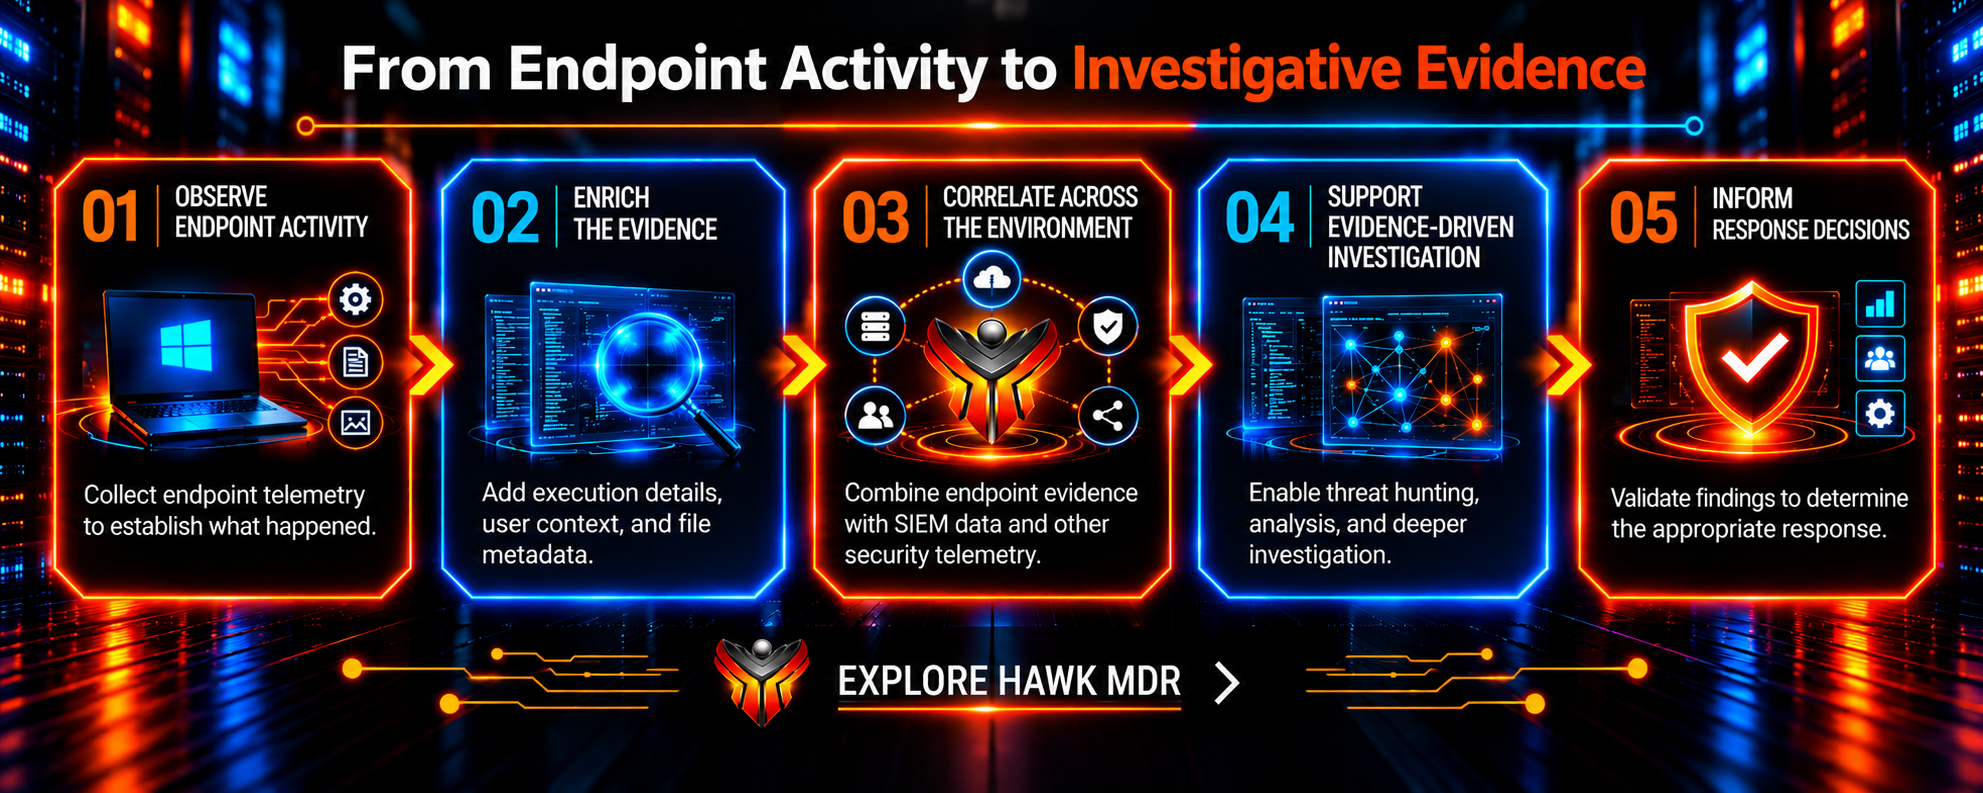
From Endpoint Activity to Investigative Evidence
01 | Observe Endpoint Activity
vTTAC collects Windows endpoint telemetry, including relevant process, event-log, and Sysmon activity, to help establish what occurred on the host.
02 | Enrich the Evidence
Process relationships, execution details, user context, and available file metadata help investigators understand the circumstances surrounding suspicious activity.
03 | Correlate Across the Environment
Endpoint evidence can be combined with SIEM data and other available security telemetry to provide broader investigative context.
04 | Support Evidence-Driven Investigation
The resulting evidence supports security analytics, threat hunting, and further investigation through HAWK's security operations environment.
05 | Inform Response Decisions
Validated investigative findings help security teams determine whether containment or another response is appropriate, subject to the customer's defined authority and available integrations.
Built for Security Teams That Need More Than Alerts
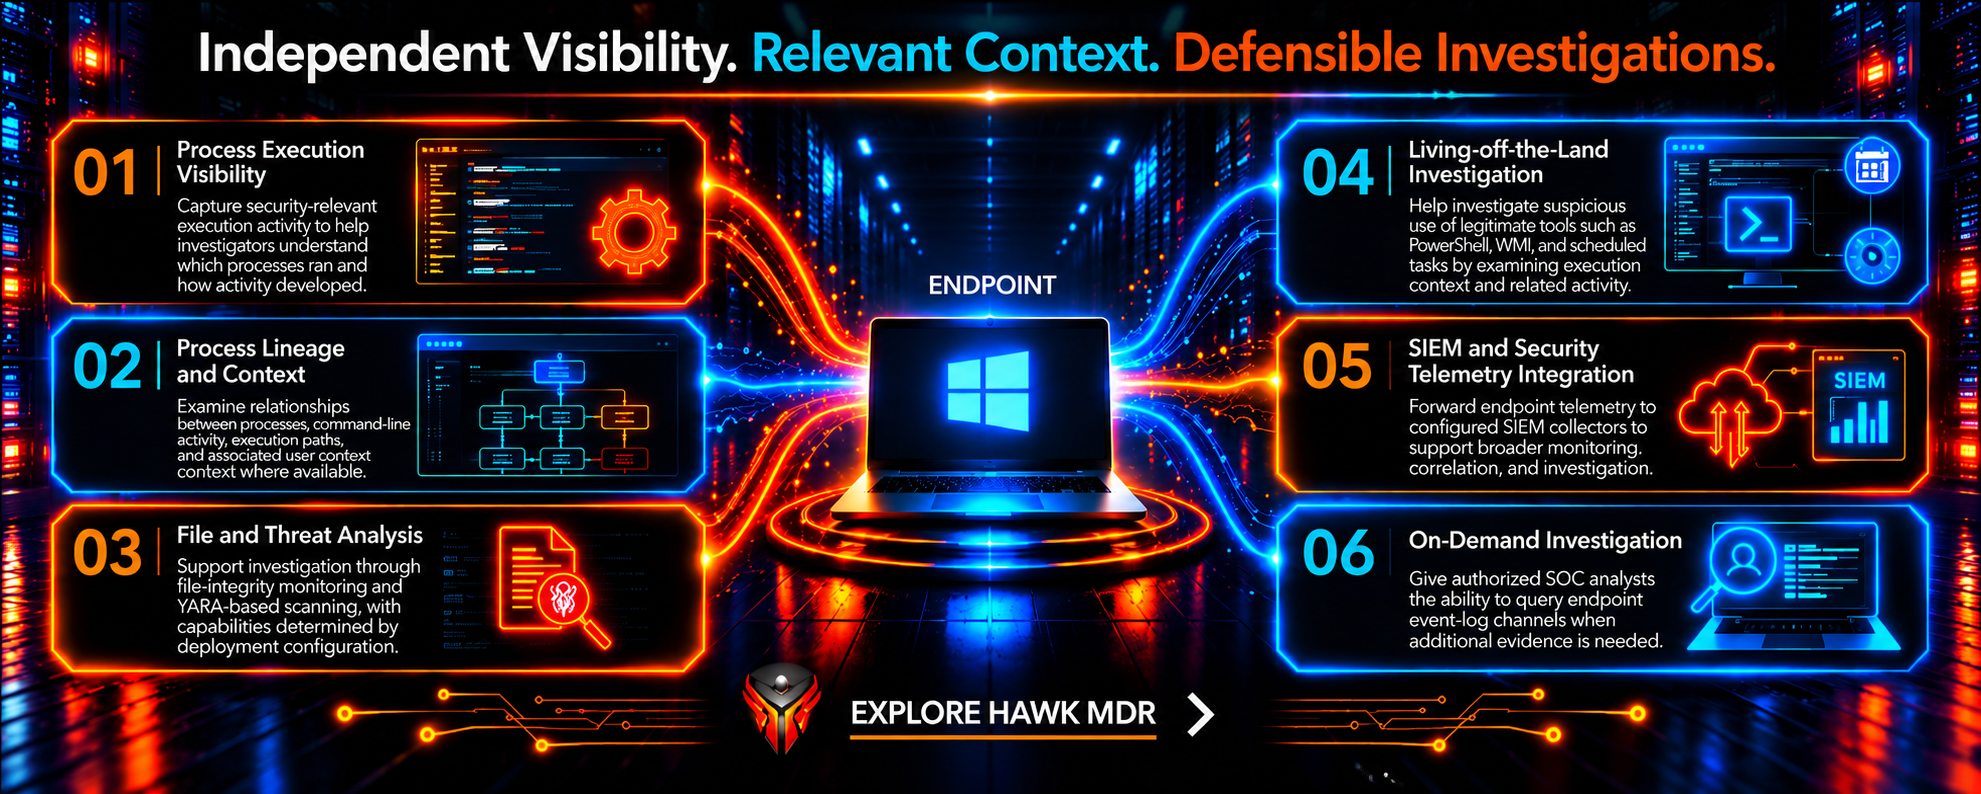
Independent Visibility. Relevant Context. Defensible Investigations.
Process Execution Visibility
Capture security-relevant execution activity to help investigators understand which processes ran and how activity developed.
Process Lineage and Context
Examine parent-child relationships, command-line activity, execution paths, and associated user context where available.
File and Threat Analysis
Support investigation through file-integrity monitoring and YARA-based scanning, with capabilities determined by the agent's deployment configuration.
Living-off-the-Land Investigation
Help investigate suspicious uses of legitimate tools such as PowerShell, WMI, and scheduled tasks by examining their execution context and related activity.
SIEM and Security Telemetry Integration
Forward endpoint telemetry to a configured SIEM collector, allowing it to contribute to broader security monitoring and correlation.
On-Demand Investigation
Give authorized SOC analysts the ability to query endpoint event-log channels when additional evidence is needed.
Complement Your Existing EDR
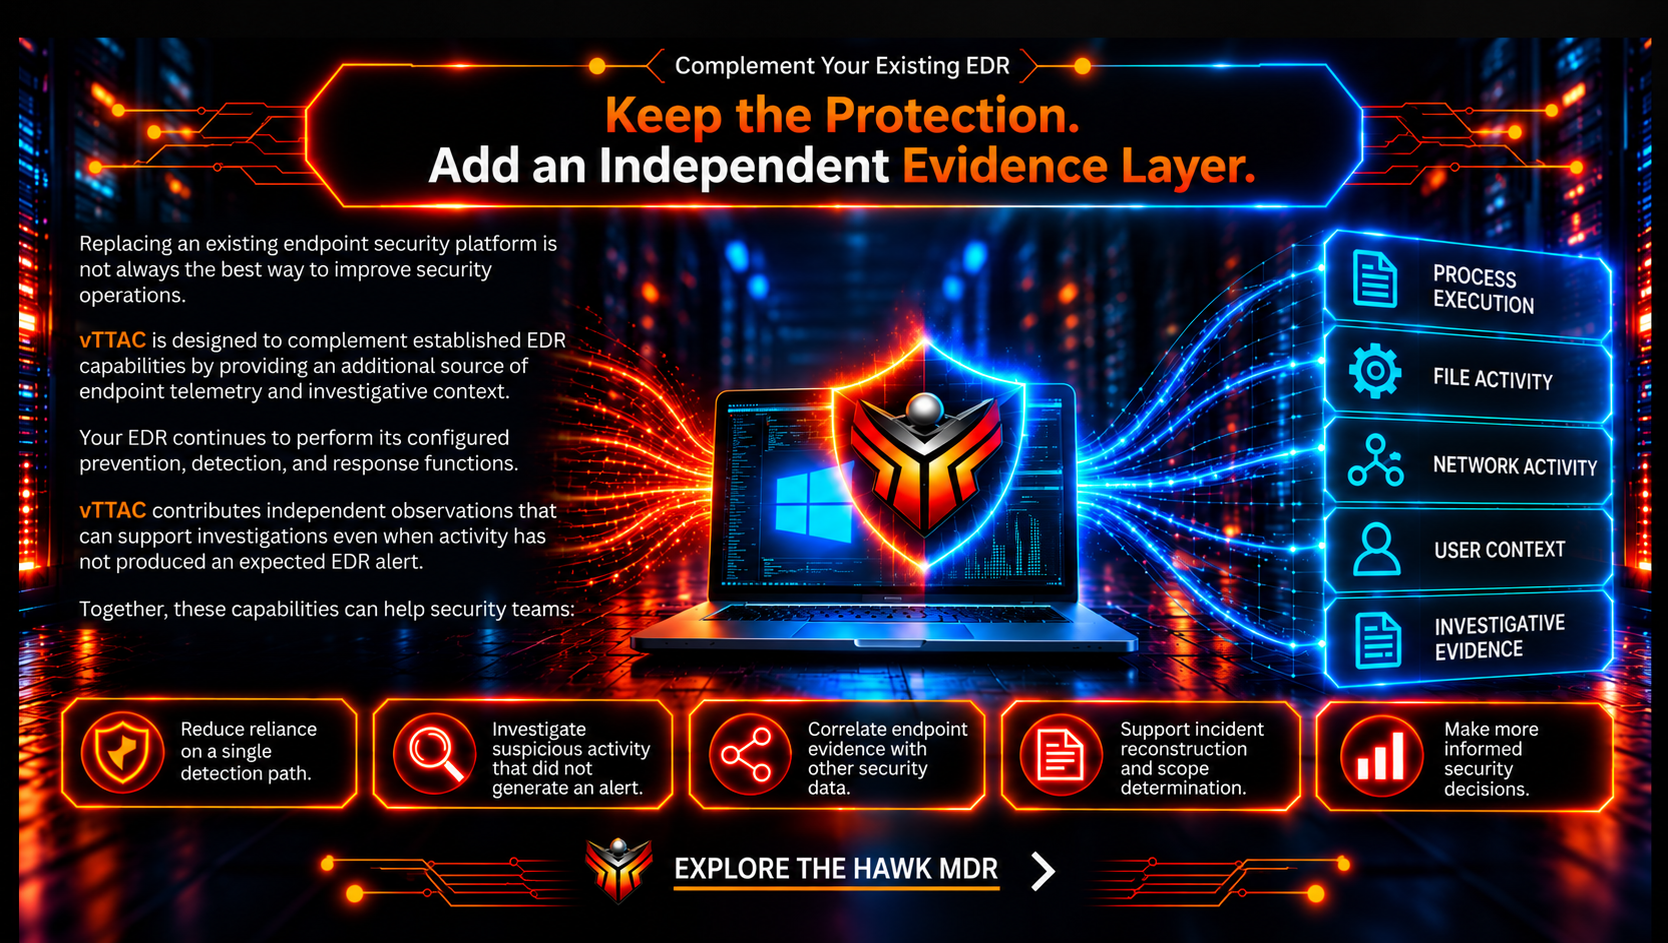
Keep the Protection. Add an Independent Evidence Layer.
Replacing an existing endpoint security platform is not always the best way to improve security operations.
vTTAC is designed to complement established EDR capabilities by providing an additional source of endpoint telemetry and investigative context.
Your EDR continues to perform its configured prevention, detection, and response functions.
vTTAC contributes independent observations that can support investigations even when activity has not produced an expected EDR alert.
Together, these capabilities can help security teams:
Reduce reliance on a single detection path.
Investigate suspicious activity that did not generate an alert.
Correlate endpoint evidence with other security data.
Support incident reconstruction and scope determination.
Make more informed security decisions.
Stronger security does not always require another replacement project.
Sometimes it requires better evidence from the environment you already have.
Deployment Designed Around Operational Needs
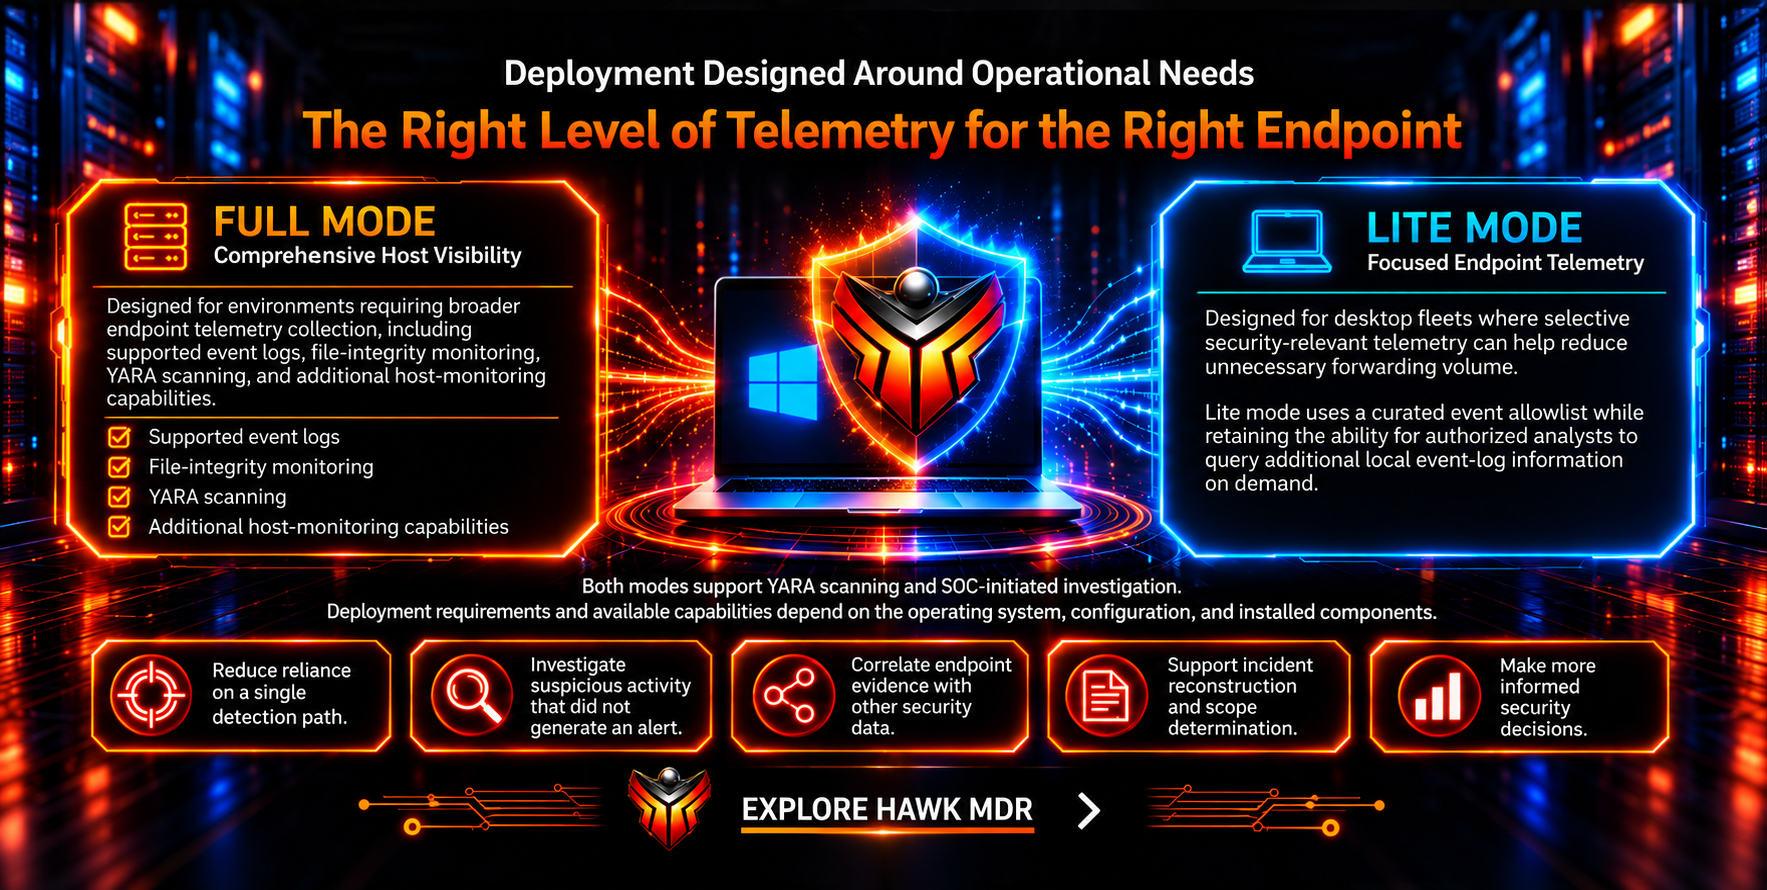
The Right Level of Telemetry for the Right Endpoint
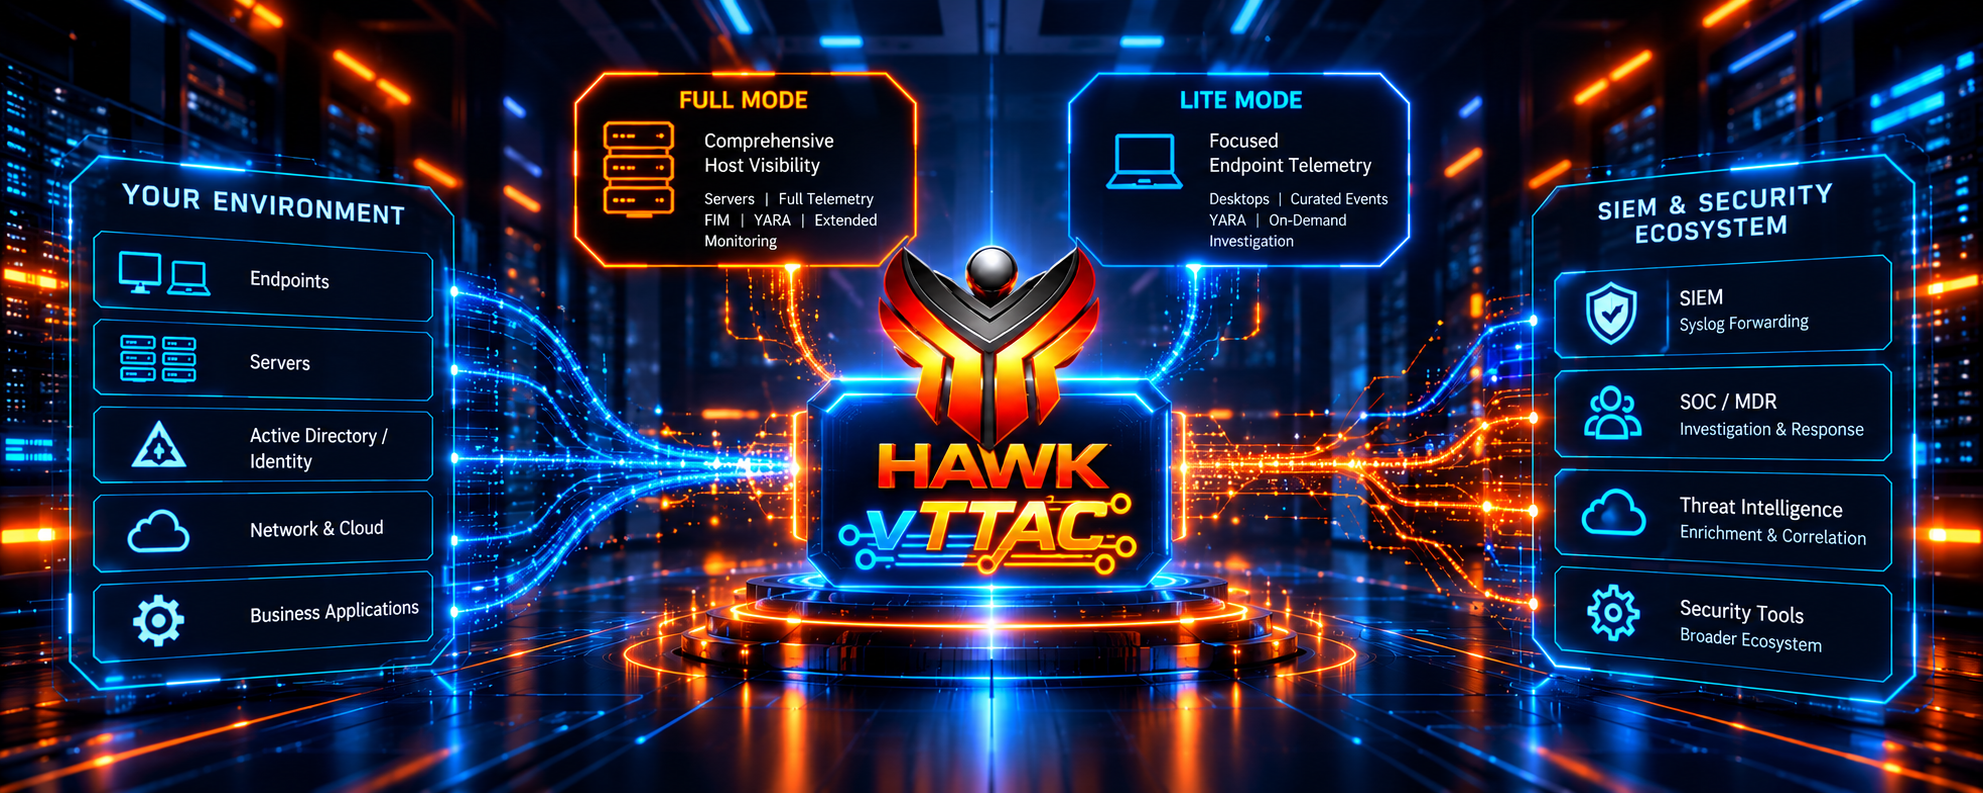
vTTAC supports two Windows deployment modes.
Full Mode — Comprehensive Host Visibility
Designed for environments requiring broader endpoint telemetry collection, including supported event logs, file-integrity monitoring, YARA scanning, and additional host-monitoring capabilities.
Lite Mode — Focused Endpoint Telemetry
Designed for desktop fleets where selective security-relevant telemetry can help reduce unnecessary forwarding volume.
Lite mode uses a curated event allowlist while retaining the ability for authorized analysts to query additional local event-log information on demand.
Both modes support YARA scanning and SOC-initiated investigation.
Deployment requirements and available capabilities depend on the operating system, configuration, and installed components.
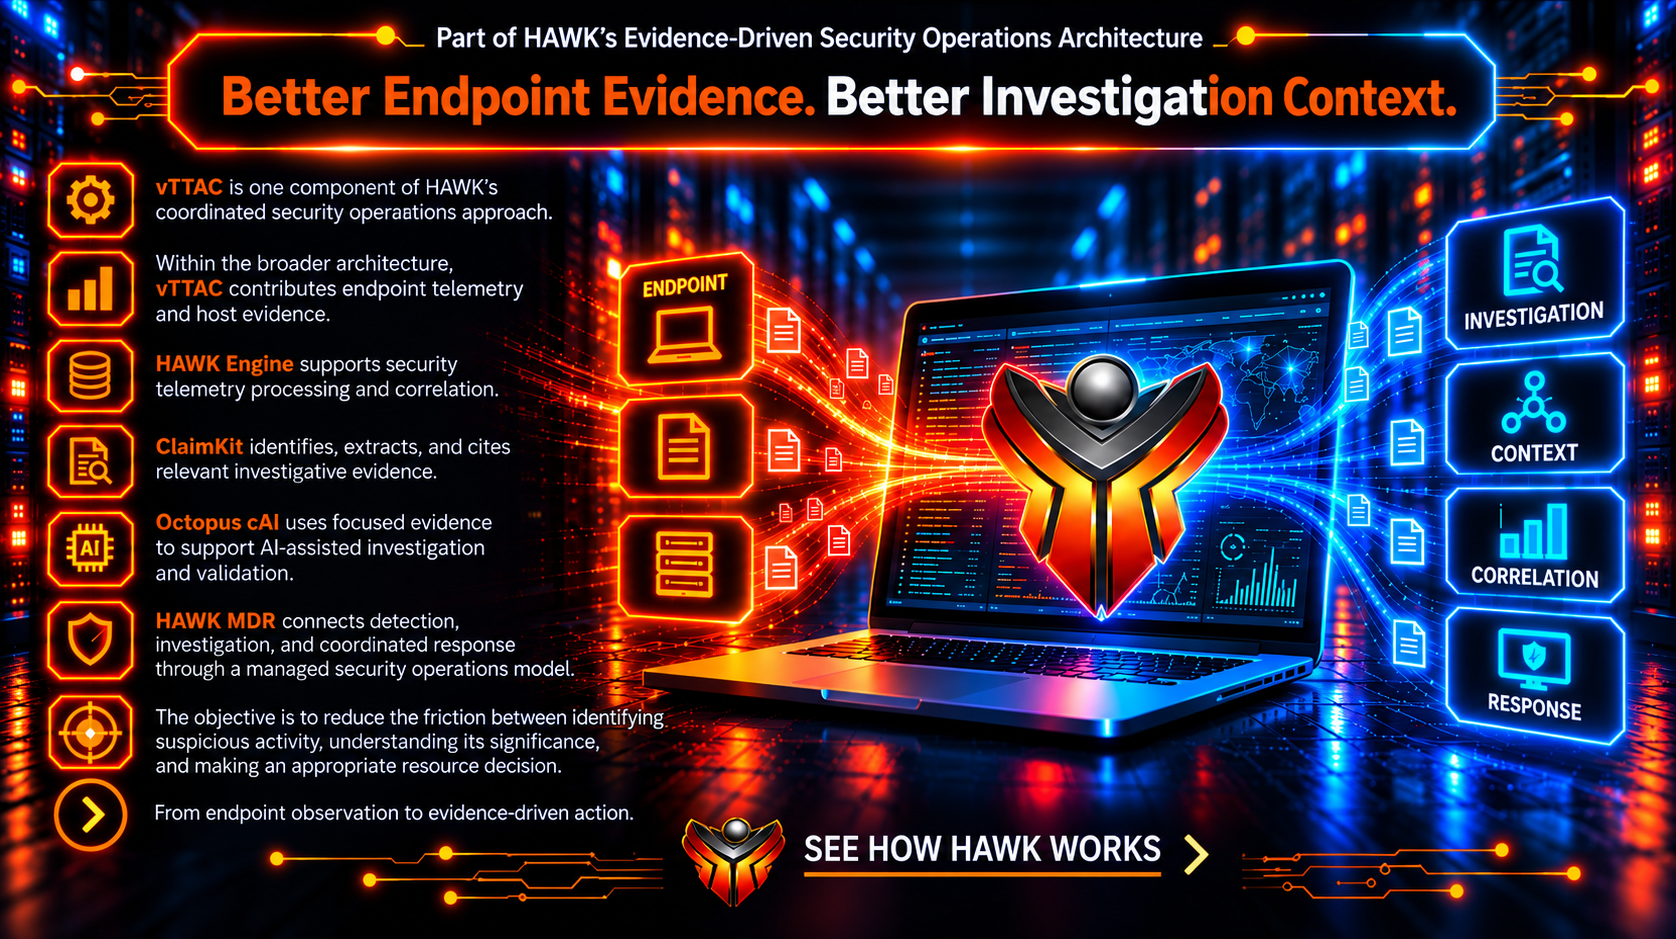
Part of HAWK's Evidence-Driven Security Operations Architecture
Better Endpoint Evidence. Better Investigation Context.
vTTAC is one component of HAWK's coordinated security operations approach.
Within the broader architecture:
vTTAC contributes endpoint telemetry and host evidence.
HAWK Engine supports security telemetry processing and correlation.
ClaimKit identifies, extracts, and cites relevant investigative evidence.
Octopus cAI uses focused evidence to support AI-assisted investigation and validation.
HAWK MDR connects detection, investigation, and coordinated response through a managed security operations model.
The objective is to reduce the friction between identifying suspicious activity, understanding its significance, and making an appropriate response decision.
From endpoint observation to evidence-driven action.
Strengthen the Security Investments You Already Have
Your EDR Is an Important Part of the Answer. It Should Not Be the Only Source of Evidence.
Security teams need more than an alert to explain what happened.
They need the surrounding activity, supporting context, and evidence necessary to investigate confidently and determine an appropriate response.
HAWK vTTAC helps strengthen that foundation by contributing independent endpoint telemetry to a broader evidence-driven security operations environment.
Build stronger investigations without automatically replacing the endpoint protection you already trust.