HAWK.io Managed Detection & Response (MDR)
Security Operations That Don’t Stop at Detection
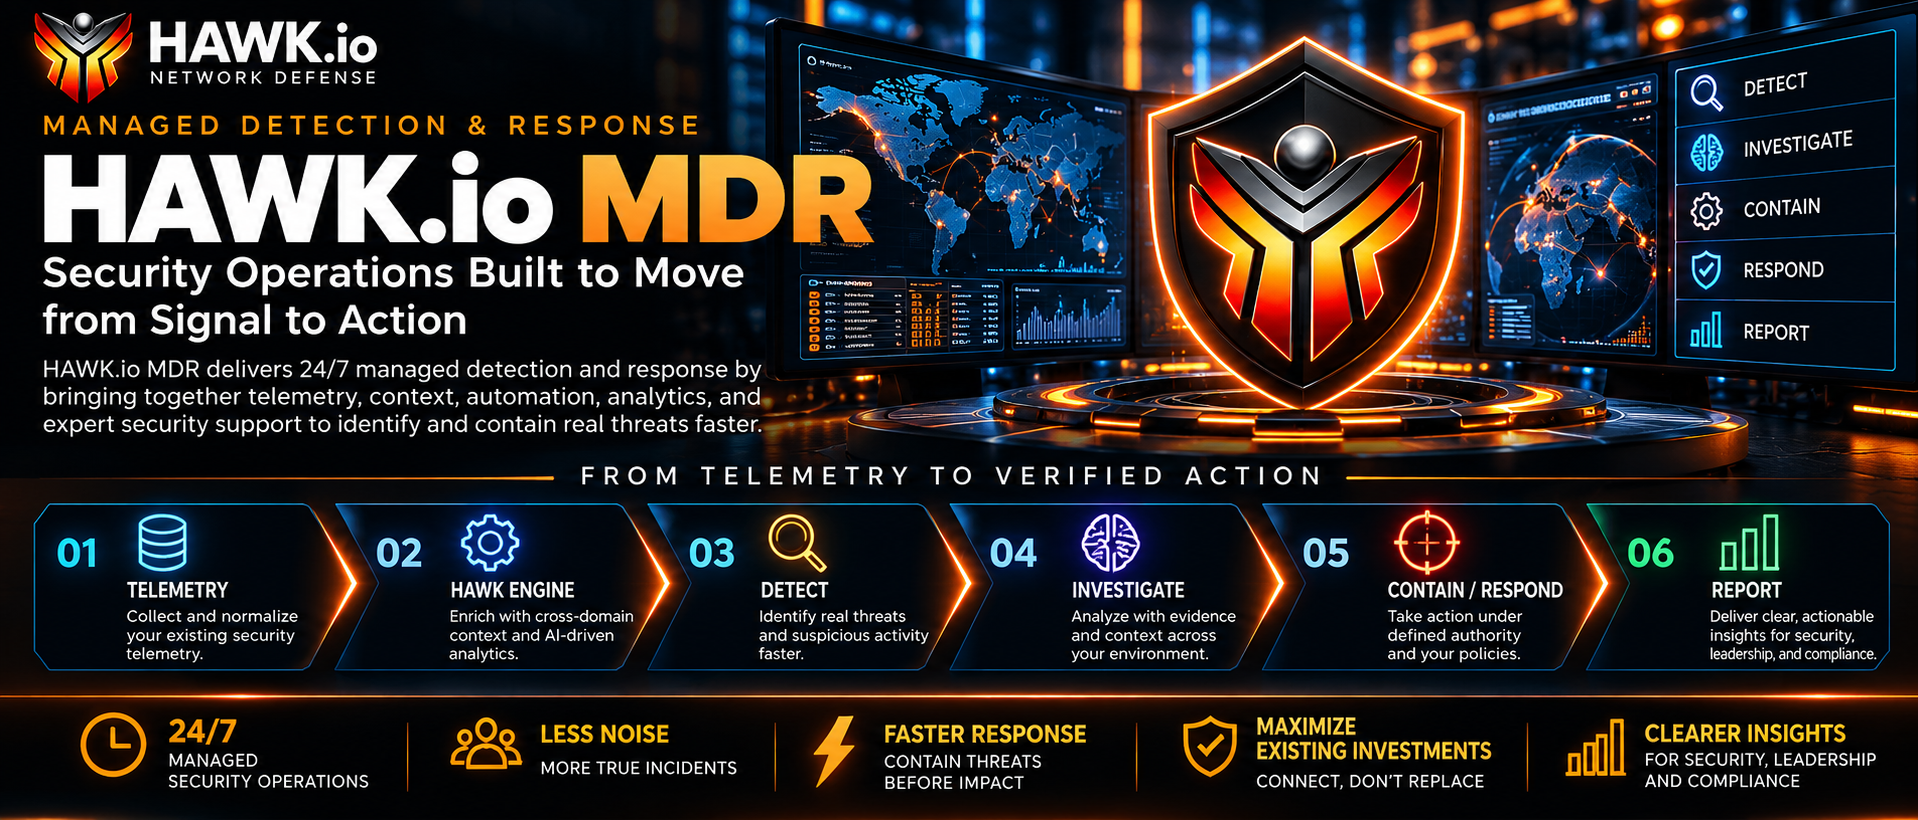
HAWK.io MDR delivers 24/7 managed detection and response by bringing together the security telemetry, context, evidence, automation, analytics, and expertise organizations need to identify, investigate, and contain real threats faster.
Rather than replacing the security investments already in place, HAWK.io connects and operationalizes the existing security ecosystem. Telemetry and context from endpoint, identity, cloud, network, email, operating systems, and other security technologies are normalized, enriched, and analyzed through the HAWK platform to create a more complete picture of suspicious activity.
The result is a coordinated security operation that moves beyond alert generation to detection, evidence-driven investigation, decision, containment, response, verification, and reporting.
What HAWK Managed Detection & Response Delivers
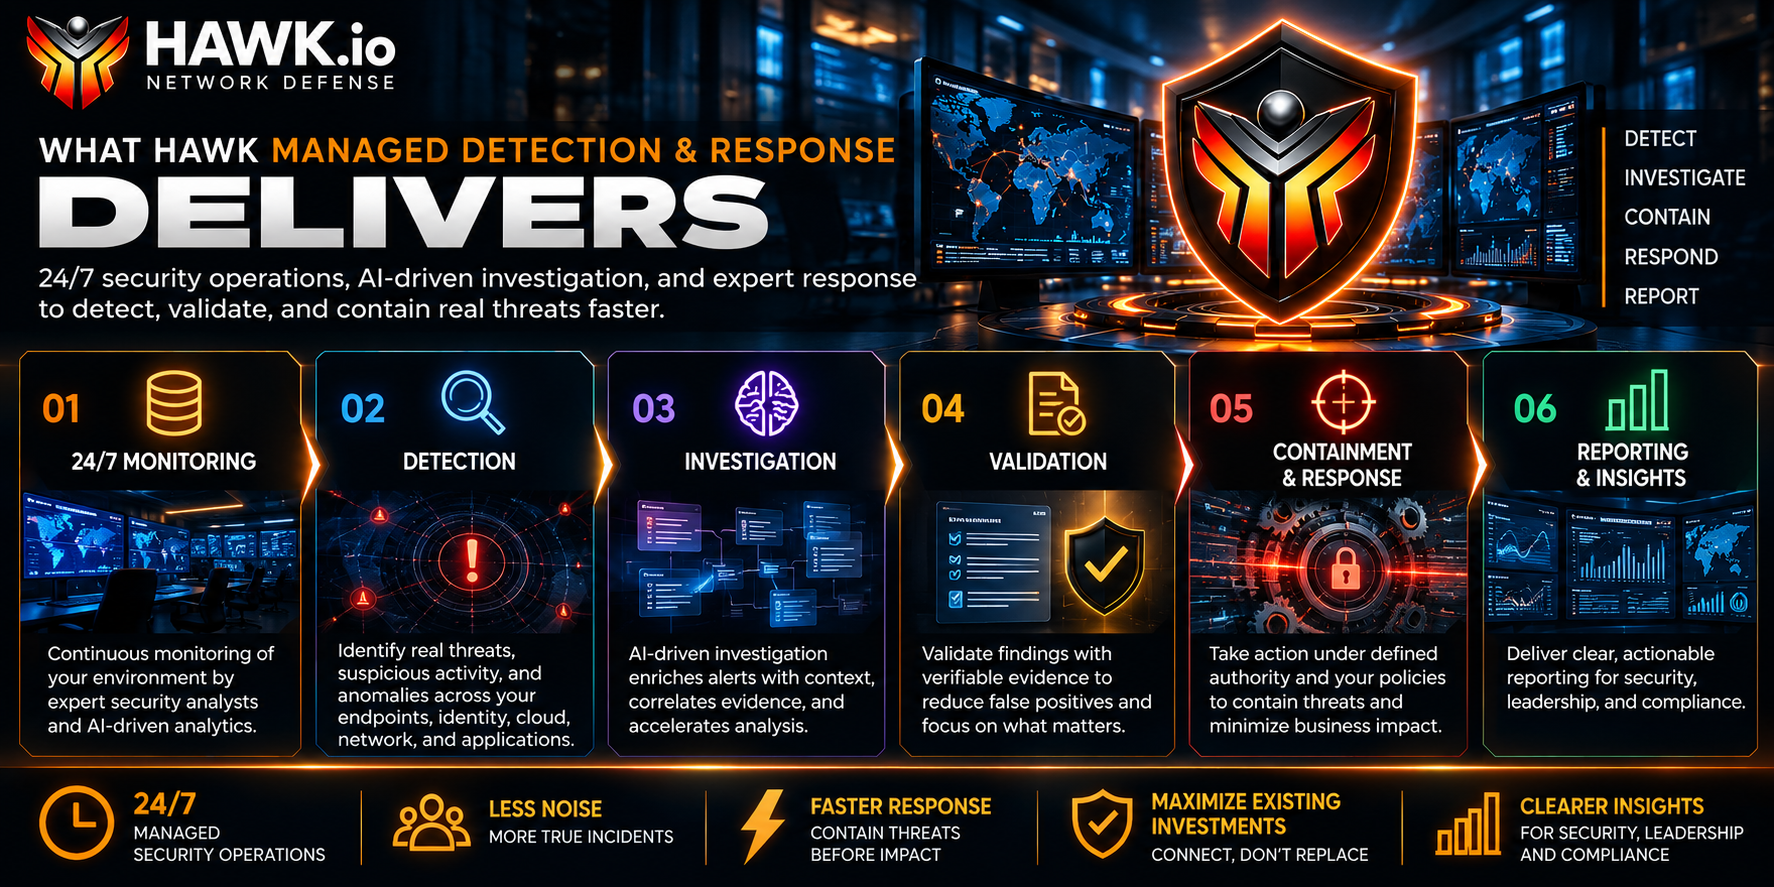
HAWK Managed Detection & Response combines continuous security monitoring, evidence-driven investigation, coordinated response, and security expertise to help organizations identify, investigate, and respond to threats across their existing security environments.
24/7 Security Monitoring
HAWK provides continuous managed detection and response, using security telemetry and contextual information from the connected customer environment to identify activity requiring investigation.
Threat Detection and Investigation
The HAWK Engine analyzes and enriches security telemetry. Octopus cAI supports autonomous investigation using relevant context and evidence to evaluate suspicious activity and support validated findings.
Evidence Intelligence and Validation
HAWK.io ClaimKit identifies, extracts, and cites relevant investigation evidence. This supports traceable findings, evidence validation, and more defensible security decisions.
Coordinated Threat Response
HAWK supports policy-governed response through connected security technologies. Automated actions and human approvals operate within the customer's authorized procedures, permissions, and escalation boundaries.
Human Security Expertise
HAWK combines automation with security professional oversight, preserving human involvement for activities and decisions requiring additional judgment or authorization.
Verification and Reporting
Investigation evidence, decisions, response actions, and outcomes support verification, operational reporting, and the review of security effectiveness.
Built to Extend Your Existing Security Investments
HAWK MDR is designed to work alongside existing SIEM, EDR, identity, cloud, network, and other security technologies rather than requiring wholesale replacement.
Specific integration capabilities, deployment requirements, and supported response actions are established for the customer's environment.
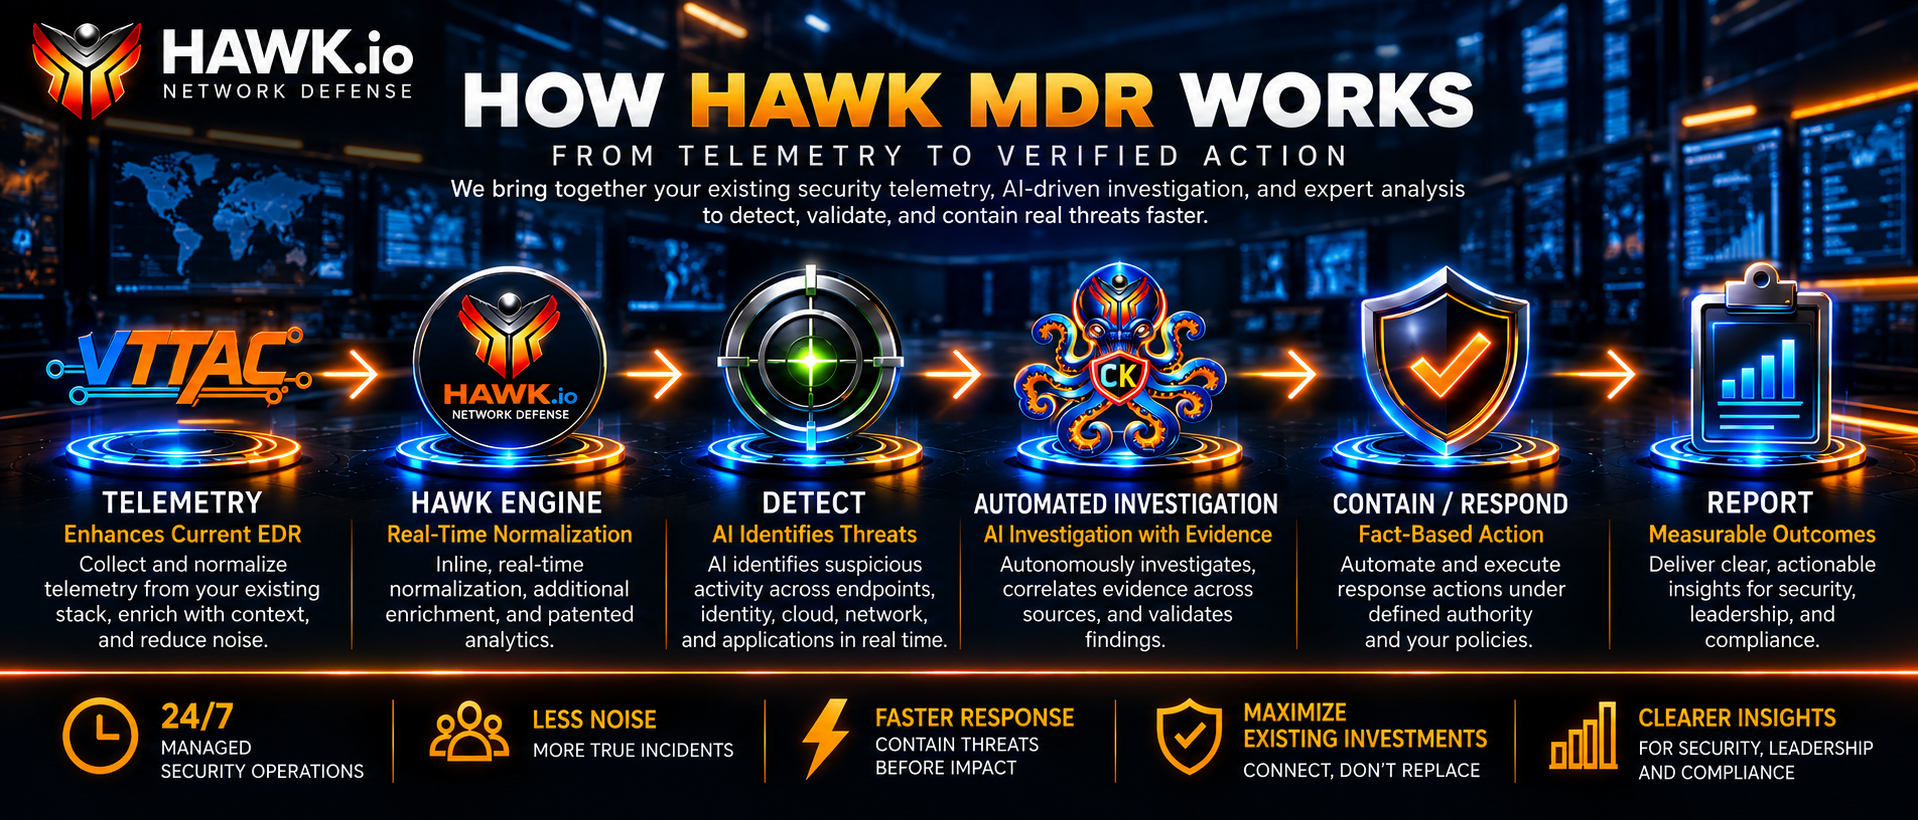
Enrich the Signal.
vTTAC™ complements existing EDR by providing lightweight, host-based contextual data enrichment and additional endpoint visibility. The underlying HAWK architecture continuously ingests and normalizes security telemetry through the HAWK Engine, enriches it with additional context and threat intelligence, and transforms incoming signals into actionable security intelligence.
Detect What Matters.
HAWK performs real-time analysis to identify suspicious activity, including techniques such as living-off-the-land activity that can be difficult to identify from isolated security signals. The objective is not simply to generate another alert, but to establish the context needed to determine what warrants investigation.
Investigate With Evidence.
Patent-pending HAWK.io ClaimKit provides focused, evidence-based context for investigation, helping reduce unnecessary information and giving Octopus cAI the relevant evidence needed to investigate, reason, and validate findings.
HAWK can also gather incident-related artifacts, analyze reputation and attack context, and map validated activity to MITRE ATT&CK tactics and techniques—building a stronger evidentiary foundation for decision-making.
Decide and Act.
Octopus cAI uses HAWK intelligence and ClaimKit evidence to investigate incidents, validate findings, determine appropriate next actions, and execute authorized actions within customer-defined policies, authority, thresholds, and escalation boundaries.
AI-Assisted vs. Autonomous MDR
AI-assisted MDR typically uses artificial intelligence to support analysts with enrichment, alert interpretation, and investigation recommendations.
Autonomous MDR extends automation into defined investigative and response activities that can execute within established policies and authorization boundaries.
The distinction is not whether humans remain involved. It is which activities can proceed automatically, what evidence supports those activities, and where human approval remains necessary.
HAWK's approach combines evidence-driven investigation with customer-defined controls over automated decisions and actions.
Contain and Respond.
Automated and coordinated response workflows execute approved actions across the security environment, reducing the time between identifying a threat and taking action while keeping security professionals at the helm.
Verify and Measure the Outcome.
HAWK maintains visibility into incidents, evidence, decisions, actions, and outcomes, supporting verification and reporting for security operations, leadership, incident response, and compliance requirements.
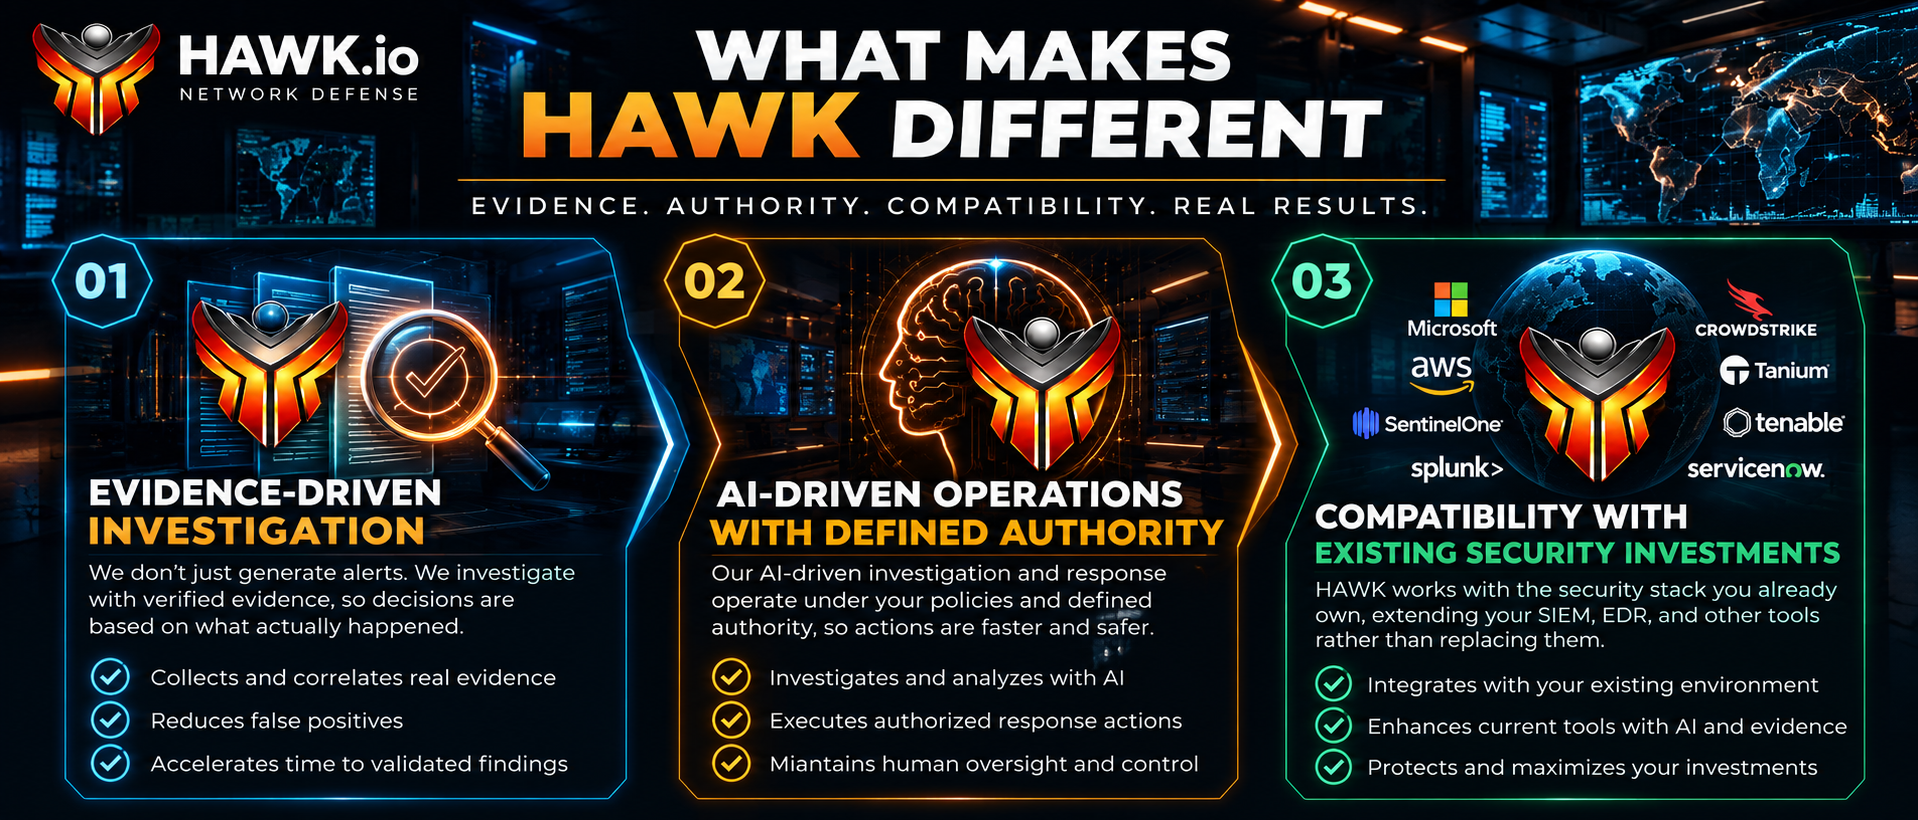
What Makes HAWK Different
Evidence-driven investigation. AI-driven operations. Security investments that work together.
HAWK.io MDR combines expert security operations, evidence intelligence, and AI-driven investigation to help organizations move from threat detection to informed response decisions.
Evidence-Driven Investigation
HAWK goes beyond individual alerts to correlate relevant security evidence and support findings that can be traced and verified. ClaimKit helps prepare investigation evidence, while Octopus cAI supports investigation and analysis.
AI-Driven Operations with Defined Authority
AI-driven investigation helps reduce repetitive manual work without removing human accountability. Authorized response actions can operate within customer-defined policies and authority boundaries, while decisions requiring additional judgment are escalated for human review.
Compatibility with Existing Security Investments
HAWK MDR is designed to extend the security tools organizations already use, including SIEM, EDR, and other available security telemetry sources. The objective is to improve investigation context and response coordination without requiring organizations to replace their existing security investments.
Learn more about HAWK Security Operations Automation.
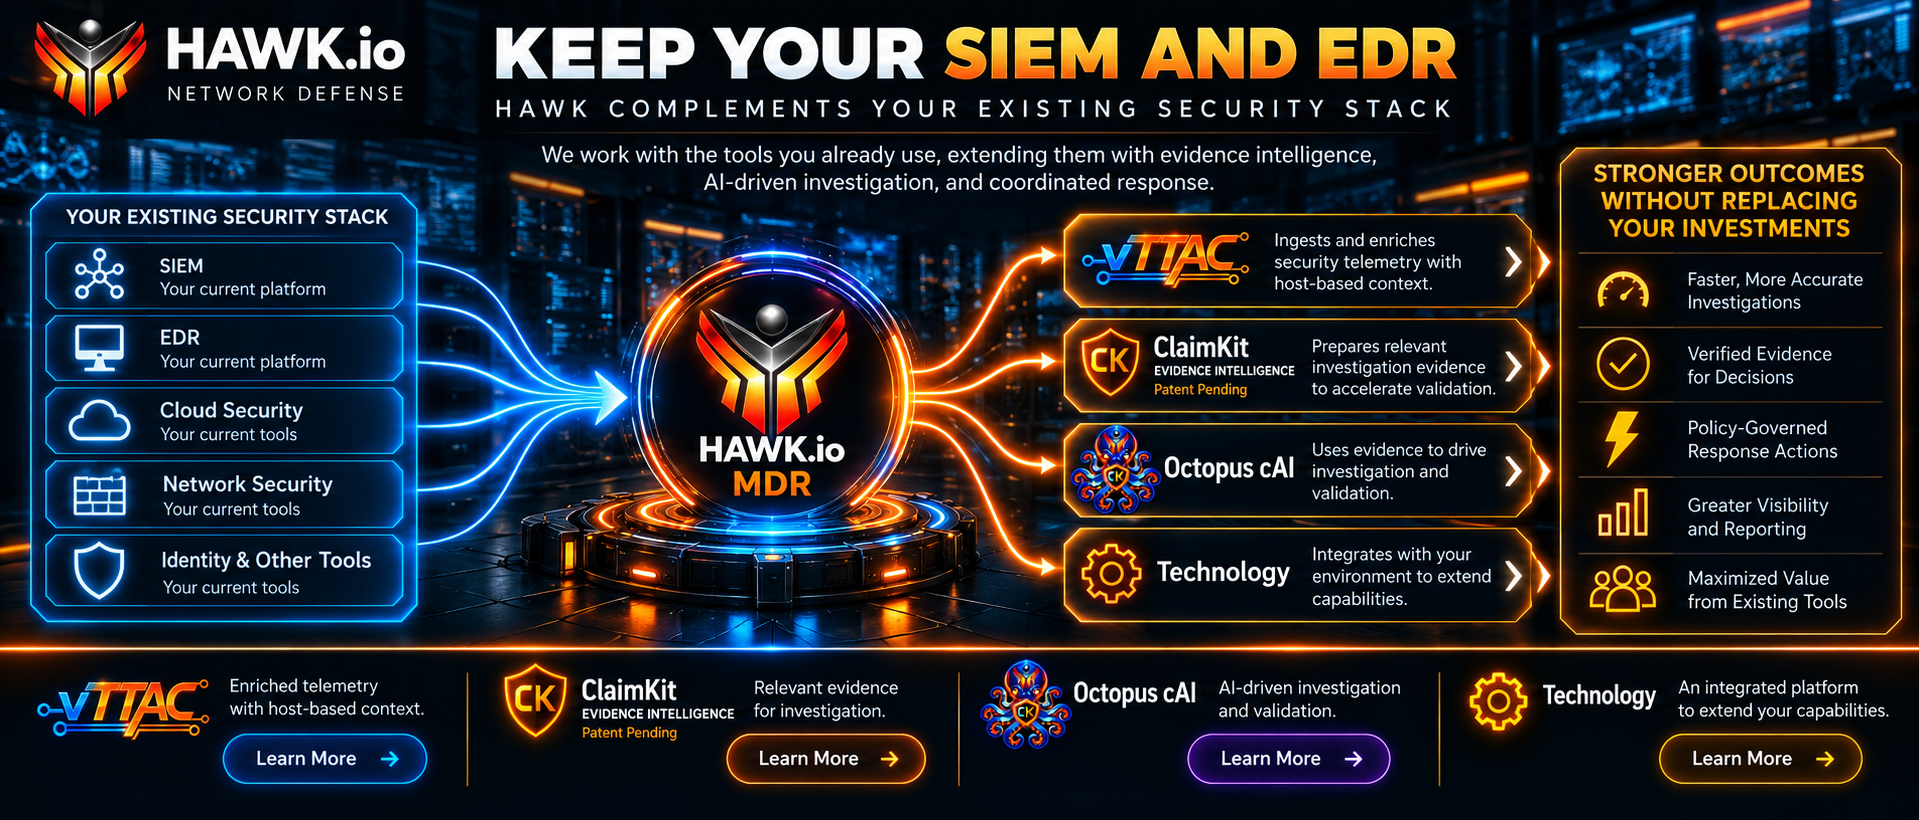
Keep Your SIEM and EDR. Strengthen What They Can Deliver.
Your existing security investments should be part of the solution—not something you have to replace.
HAWK.io MDR is designed to work alongside your existing SIEM, EDR, cloud, identity, and network security technologies.
Rather than requiring organizations to rebuild their security stack, HAWK brings together available security telemetry, evidence-driven investigation, and coordinated response to help security teams make better-informed decisions.
HAWK's technologies support this approach:
HAWK vTTAC — Independent Endpoint Evidence
HAWK vTTAC complements existing EDR capabilities by providing additional endpoint telemetry and investigative context.
HAWK ClaimKit — Evidence Intelligence
HAWK ClaimKit, patent pending, helps identify, organize, and cite relevant investigation evidence to support traceable, verifiable findings.
HAWK Octopus cAI — AI-Driven Investigation
HAWK Octopus cAI supports evidence-driven investigation, correlation, and analysis to inform security decisions and coordinated response.
HAWK Technology — Connected Security Capabilities
Explore HAWK's technology to understand how these capabilities contribute to the broader MDR approach.
The advantage: stronger investigation context, more informed response decisions,
and greater value from the security technologies you already own.
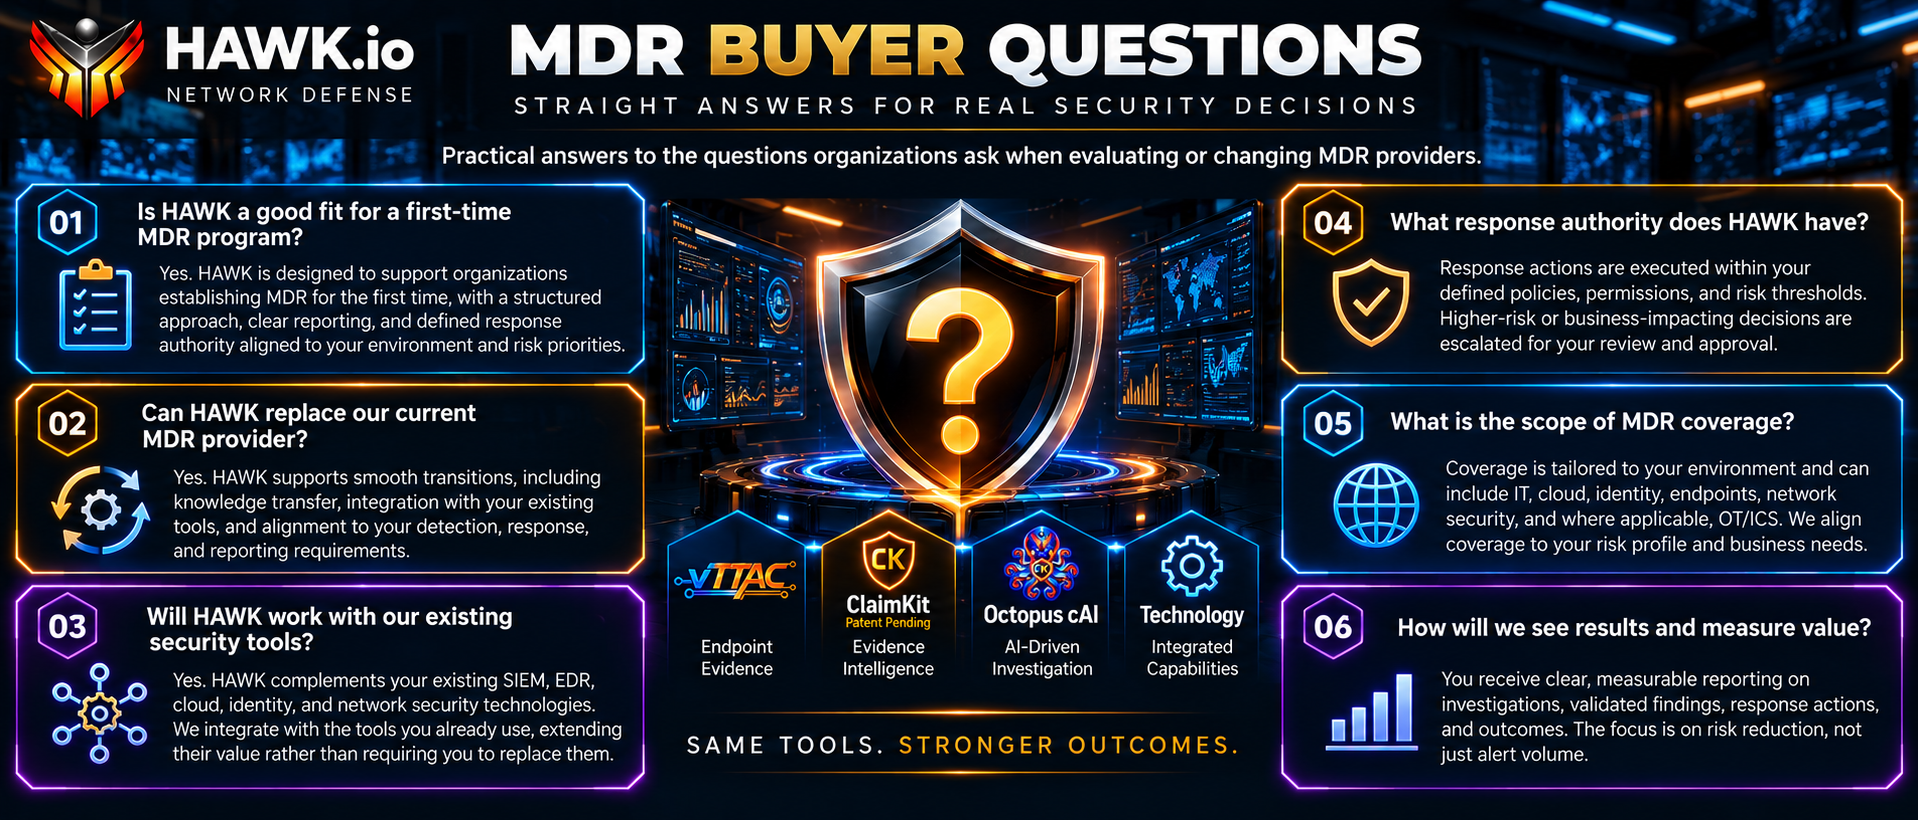
Frequently Asked Questions About HAWK Managed Detection and Response
What should we look for when choosing our first MDR provider?
Look beyond alert monitoring. Evaluate investigation quality, security coverage, integration with existing tools, response capabilities, reporting, and how the provider handles escalation and decision authority.
HAWK.io MDR emphasizes evidence-driven investigation, AI-supported security operations, and coordinated response within defined customer authority.
Can we switch to HAWK MDR without replacing our existing security tools?
HAWK.io MDR is designed to complement existing security investments rather than require wholesale replacement.
The transition approach, supported integrations, and onboarding requirements depend on your current environment and security operations needs.
Will HAWK MDR work with our existing SIEM and EDR?
HAWK MDR is designed to work with existing security technologies, including SIEM and EDR solutions.
HAWK vTTAC can provide additional endpoint evidence, while ClaimKit and Octopus cAI support evidence-driven investigation and analysis. Specific integration capabilities should be confirmed for your environment.
What security coverage does HAWK MDR provide?
HAWK MDR brings together available security telemetry, investigation capabilities, and coordinated response to support managed detection and response.
Coverage depends on the connected security sources, deployed capabilities, service scope, and agreed operational requirements.
How does HAWK MDR differ from traditional managed detection and response?
HAWK combines managed security expertise with evidence intelligence, AI-driven investigation, and policy-governed response.
The objective is to move beyond processing alerts toward validated investigative findings, informed decisions, and coordinated action.
Can HAWK automatically contain threats without human approval?
Only actions authorized under the customer's defined policies, permissions, and response procedures may be eligible for automated execution.
Higher-risk actions or decisions outside the approved authority require appropriate escalation or human approval. Autonomous investigation does not mean unrestricted response authority.
How does HAWK MDR use AI to accelerate threat investigation?
HAWK uses AI-driven investigation to analyze available security evidence, connect relevant activity, and support conclusions about potential threats.
ClaimKit helps prepare relevant investigation evidence, while Octopus cAI supports investigation and analysis. This approach is designed to reduce repetitive manual investigation work while preserving human oversight.
How can we measure the value of an MDR service?
Useful measures include investigation quality, time to validate threats, response effectiveness, security coverage, and whether actions produce the intended outcomes.
HAWK's approach emphasizes validated findings and operational accountability rather than measuring success solely by alert volume.
Better context. Stronger evidence. Faster decisions. Faster containment.
Managed detection and response should do more than identify threats. It should establish what happened, validate the evidence, and support appropriate action before an incident creates greater business impact.
Whether you're choosing your first MDR provider or considering a replacement, HAWK.io MDR is designed to strengthen your existing security operations through AI-driven investigation, evidence intelligence, and coordinated response.
Keep your security investments. Strengthen your security operations.
See How HAWK MDR Fits Your Security Environment
Talk with the HAWK team about integrating your existing security technologies, defining response authority, and aligning MDR coverage with your organization's needs.