HAWK.io helps organizations move from security signals to evidence, investigation, decisions, and coordinated response without replacing the security technologies they already own.
The HAWK platform brings together real-time telemetry, contextual enrichment, advanced analytics, evidence intelligence, autonomous investigation, and policy-governed response to reduce the time between detecting suspicious activity and taking appropriate action.
HAWK.io security solutions include Managed Detection and Response (MDR), Security Operations Automation, Cloud and Hybrid Security Operations, and Incident Response and Containment.
Security Operations Solutions
Extend Your Existing SIEM With Machine-Speed Security Operations
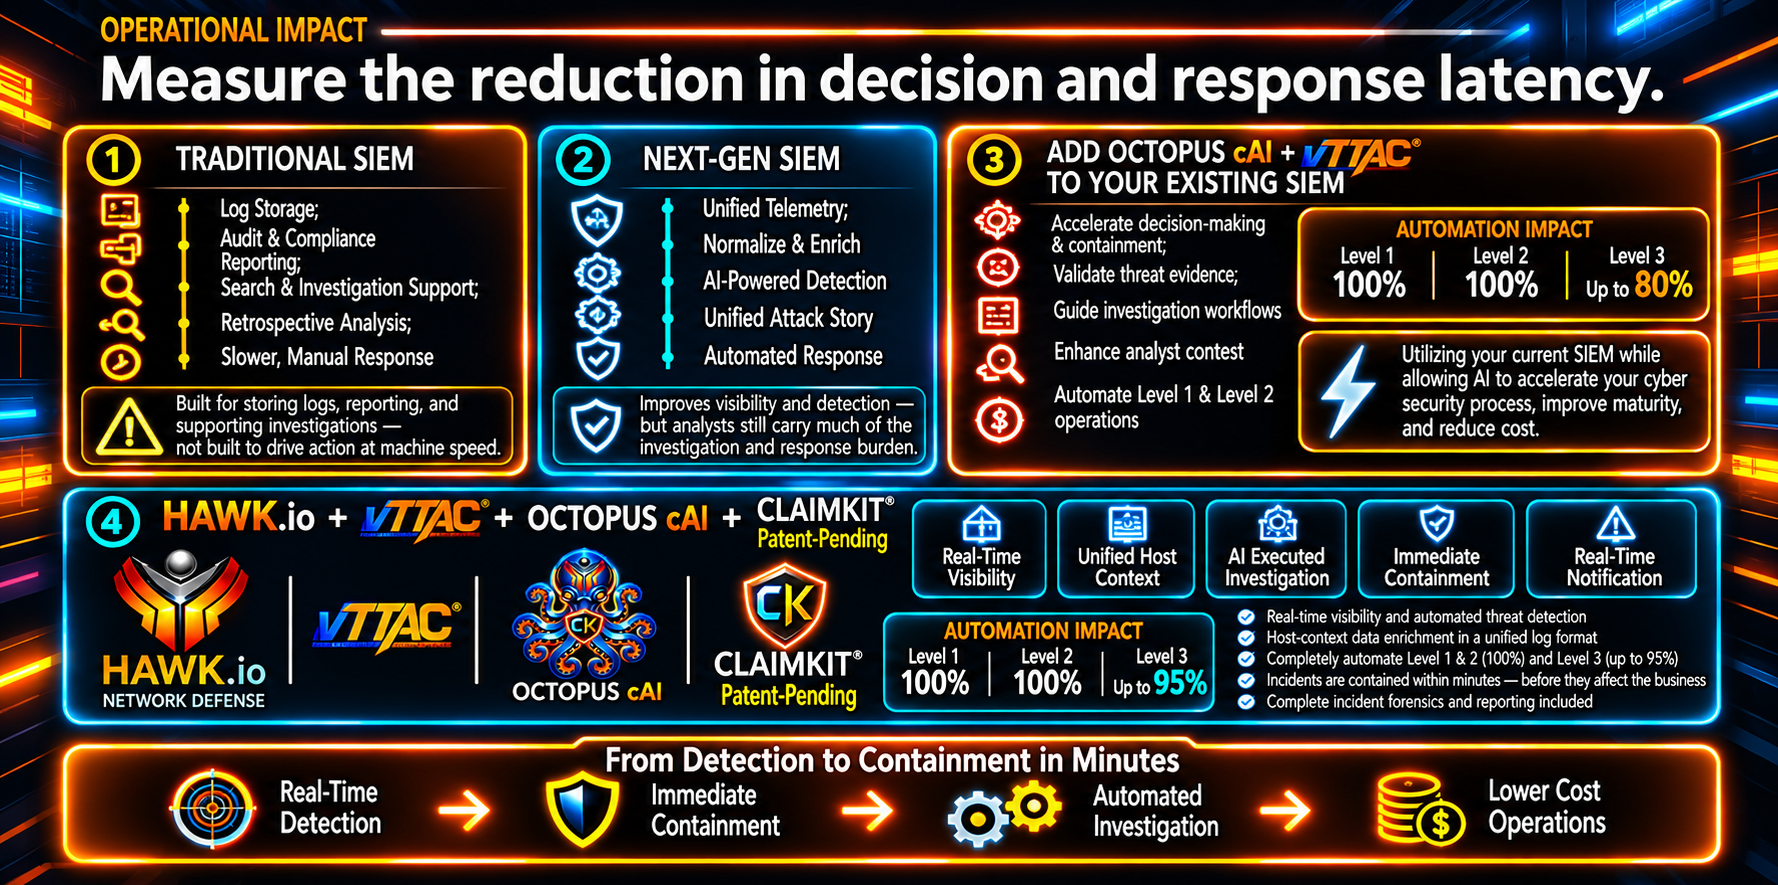
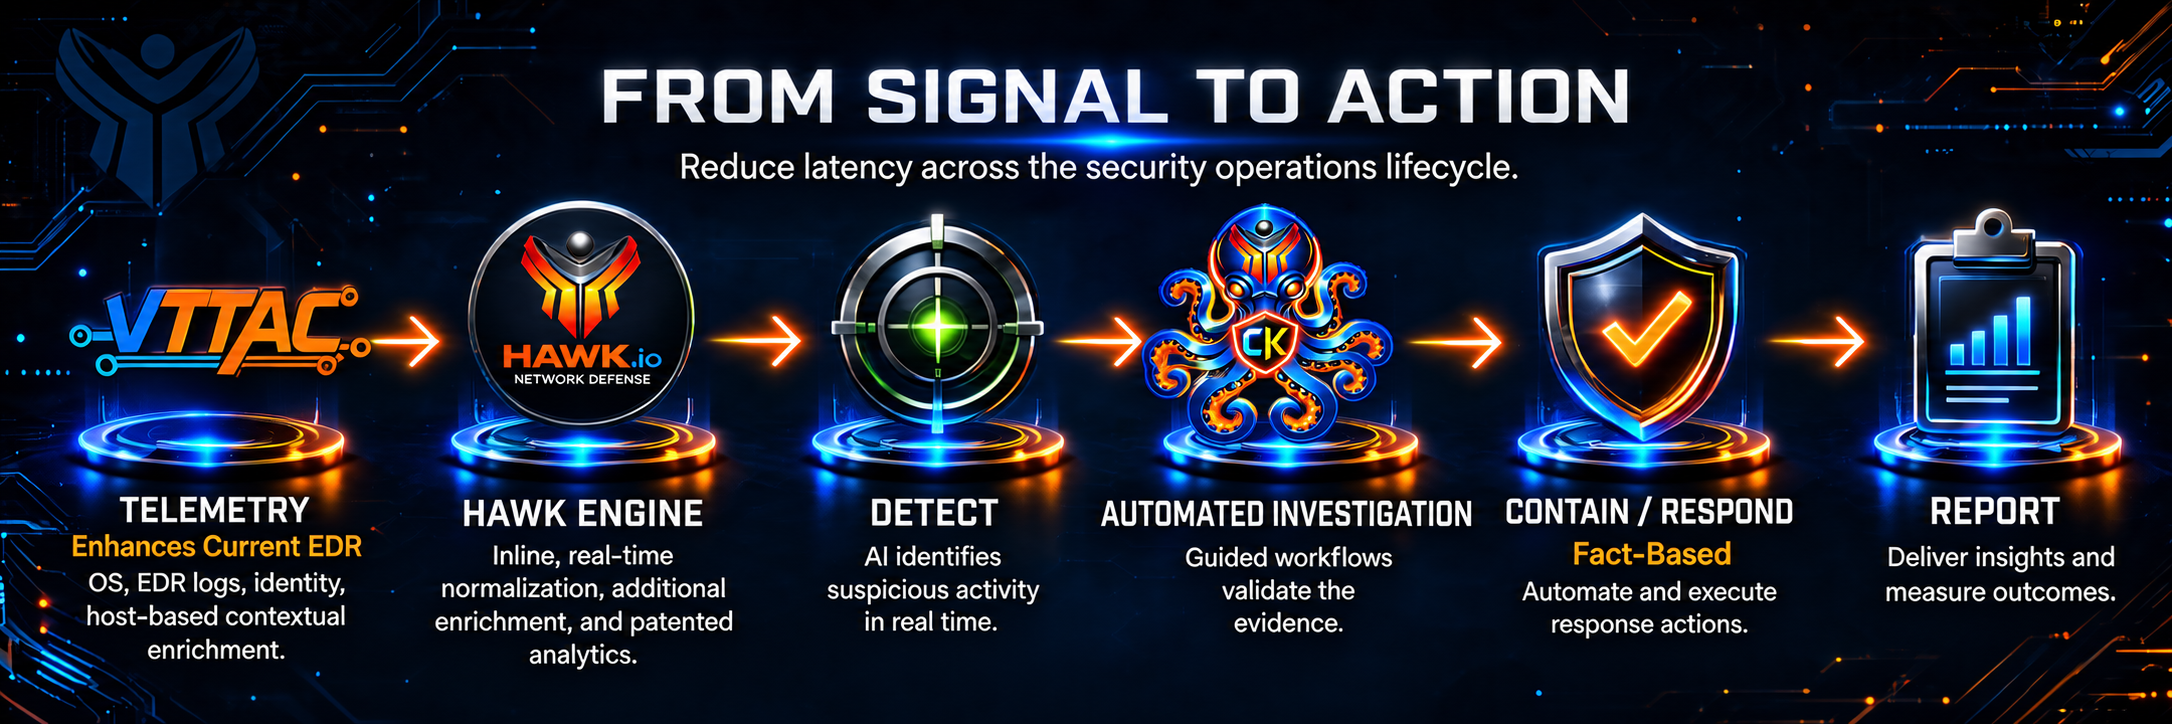
HAWK.io works with the security technologies organizations already own to extend security operations beyond log management, detection, and alerting. vTTAC™ enriches security telemetry with additional host and operational context, patent-pending HAWK.io ClaimKit identifies, extracts, and cites relevant evidence, and Octopus cAI autonomously investigates, reasons across that evidence, and validates findings.
Together, these capabilities help reduce manual investigation and response work, accelerate decision-making, and move validated threats toward authorized containment without requiring organizations to replace their existing SIEM or security stack.
Real-time visibility → enriched context → evidence-driven autonomous investigation → authorized containment → measurable outcomes
Managed Detection & Response
24/7 managed detection and response that combines real-time telemetry, contextual enrichment, evidence-driven autonomous investigation, coordinated containment, and expert security support to identify and respond to threats before they become larger business events.
Security Operations Automation
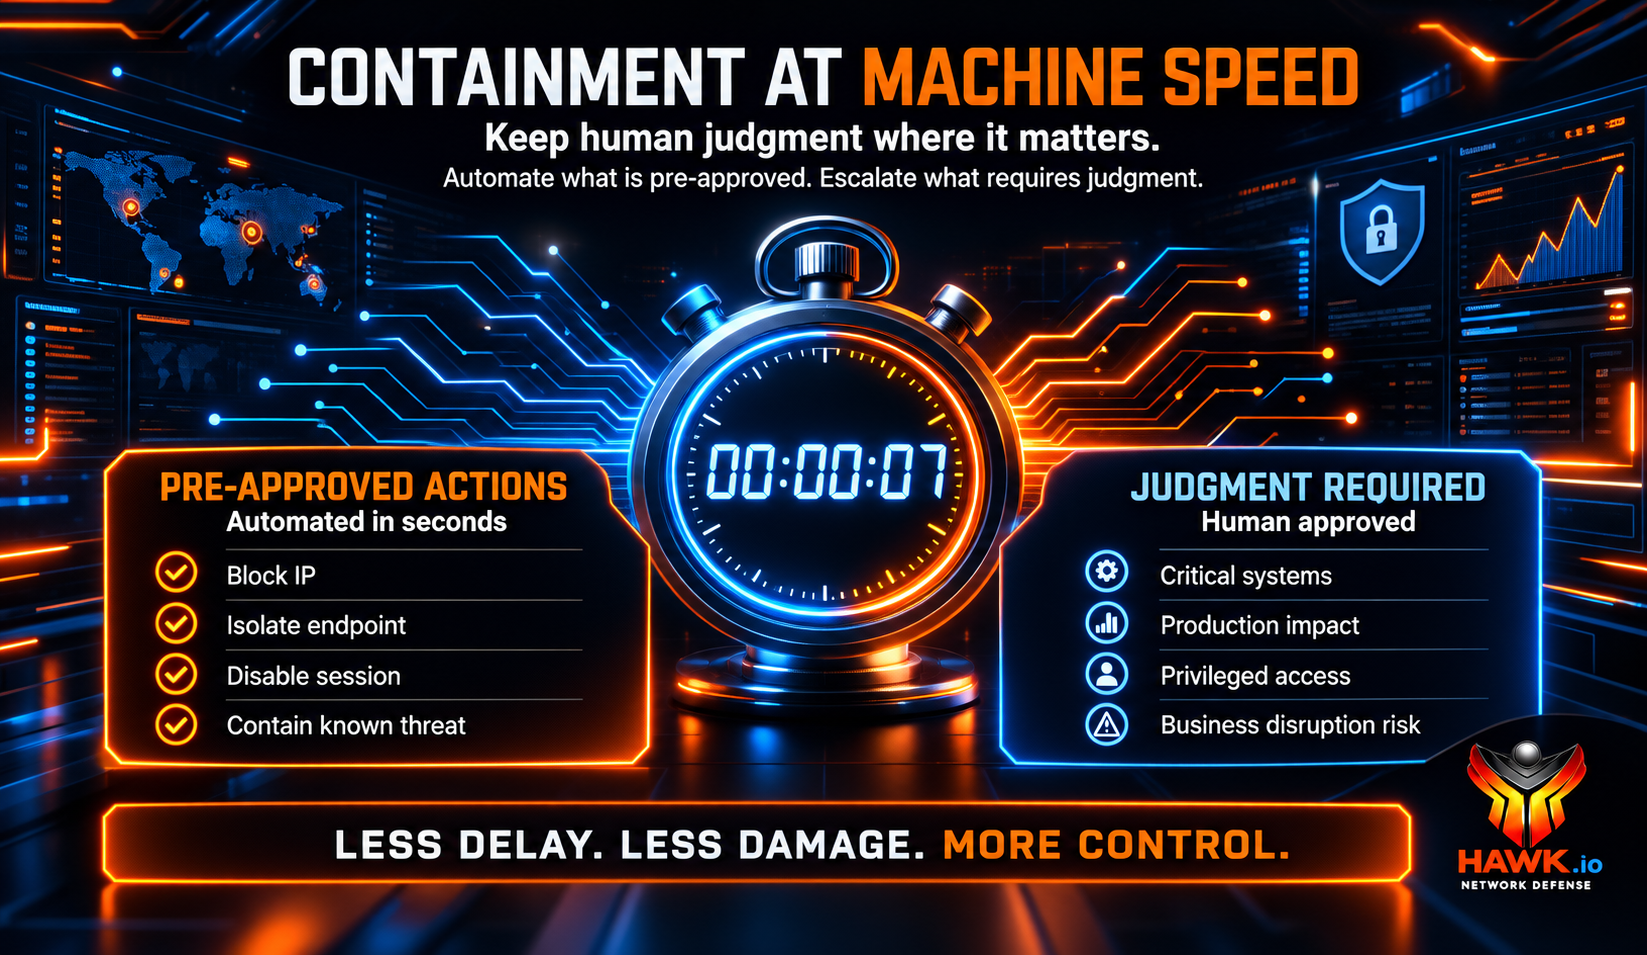
Automate repeatable security response actions while keeping human judgment where it matters. HAWK.io uses validated evidence, customer-defined policies, and authorization boundaries to execute pre-approved actions automatically while routing higher-impact decisions for human review.
Overcome the Barriers That Keep Security Operations at Human Speed
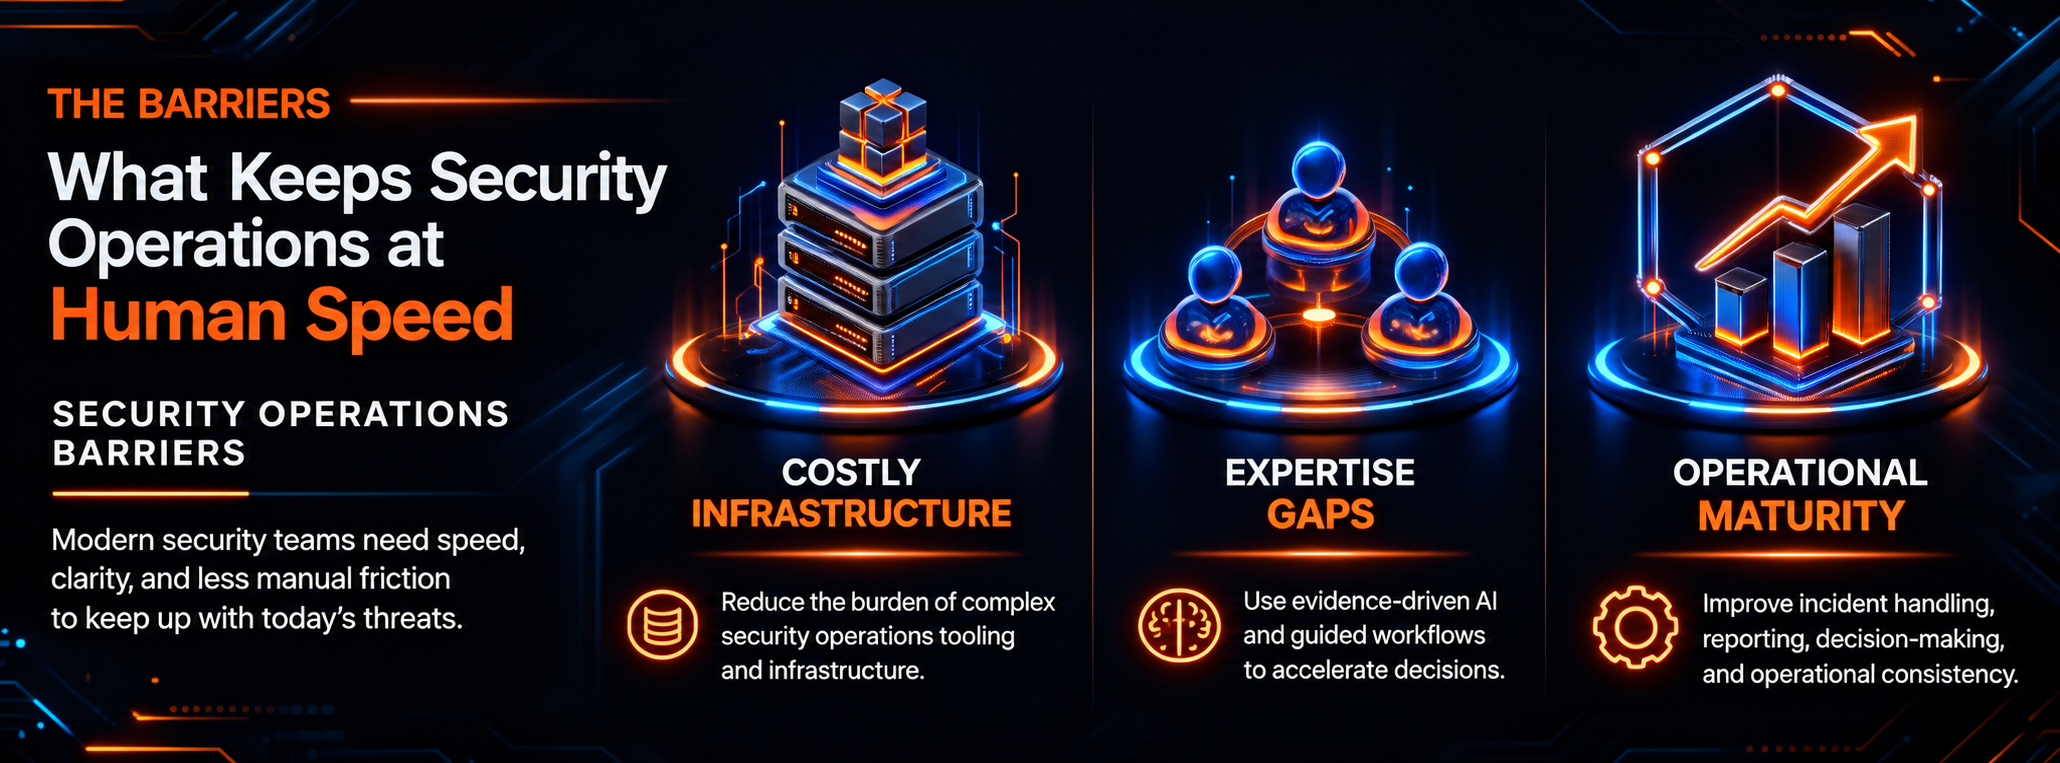
HAWK.io helps organizations reduce the infrastructure burden, expertise gaps, and operational friction that slow security operations. By combining real-time analytics, evidence intelligence, autonomous investigation, and coordinated response, HAWK enables security teams to make faster, more consistent decisions without continually adding tools, infrastructure, or manual processes.
HOW HAWK RESPONDS
Security Operations Solutions That Remove the Barriers
Security Operations Solutions That Remove the Barriers
HAWK.io brings together Managed Detection and Response (MDR), Security Operations Automation, Cloud and Hybrid Security Operations, and Incident Response and Containment to help organizations move from security signals to evidence, investigation, decisions, and coordinated action faster.
Built to work with the security technologies organizations already own, HAWK combines real-time telemetry, evidence intelligence, autonomous investigation, policy-governed response, and expert security support to reduce operational friction and contain threats before they become larger business events.
Explore Security Operations Automation
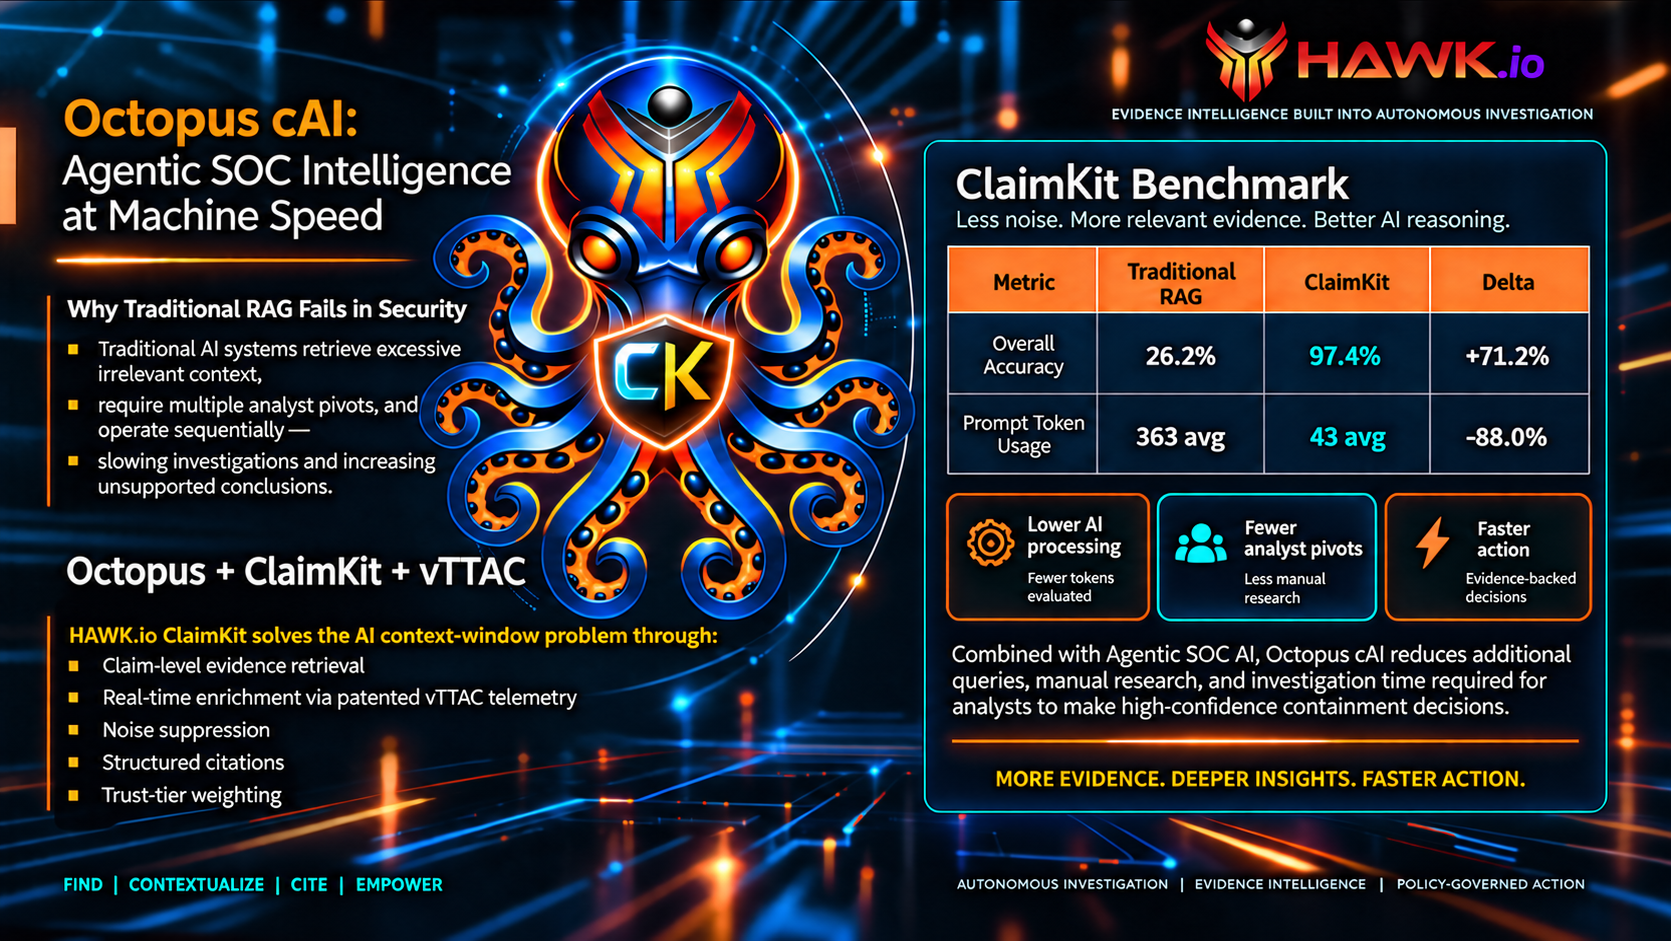
From Retrieved Context to Focused Evidence
Traditional Retrieval-Augmented Generation (RAG) retrieves information to give AI additional context. ClaimKit identifies, extracts, and cites relevant investigative evidence, preserving its connection to supporting sources.
Octopus cAI uses that focused, traceable evidence to support autonomous investigation, reasoning, and validation—helping connect findings to the evidence behind them.