

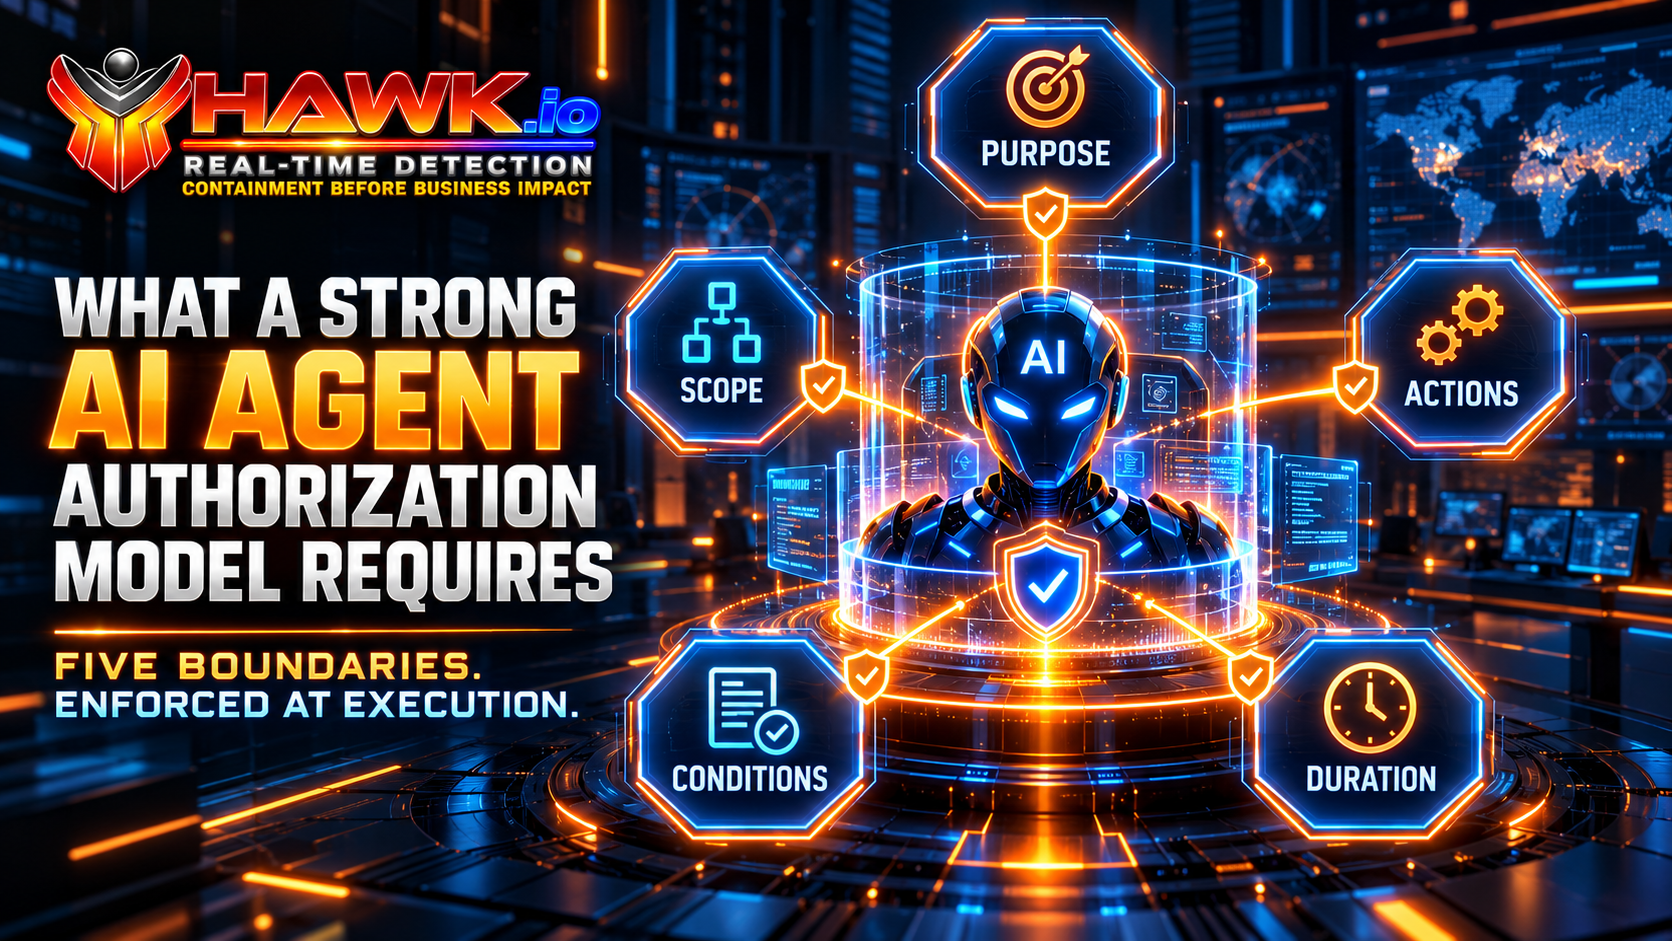
WHAT A STRONG AI AGENT AUTHORIZATION MODEL REQUIRES
Secure AI agents need more than valid credentials. HAWK Network Defense explains five boundaries of delegated authority, execution-time authorization, agent identity, audit trails, permission expiration, and verified security outcomes.
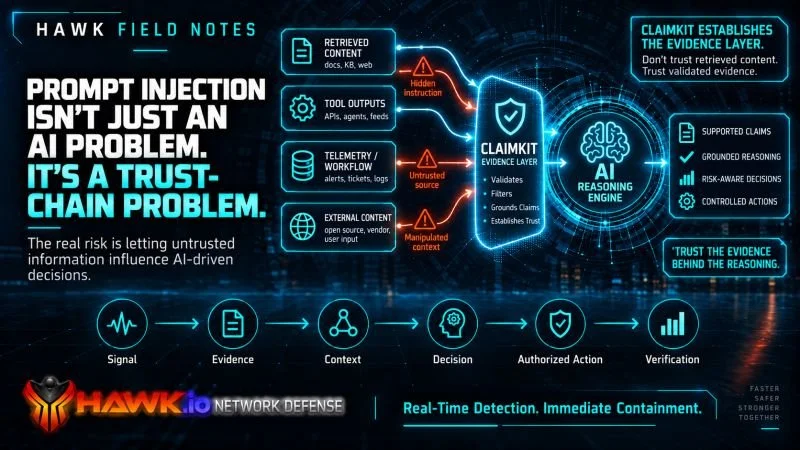
PROMPT INJECTION ISN'T JUST AN AI PROBLEM. IT'S A TRUST-CHAIN PROBLEM.
Prompt injection is more than a model vulnerability. HAWK Network Defense examines how untrusted content can compromise AI reasoning, why evidence integrity and traceable claims matter, and how ClaimKit supports an evidence layer for AI-driven security investigations.
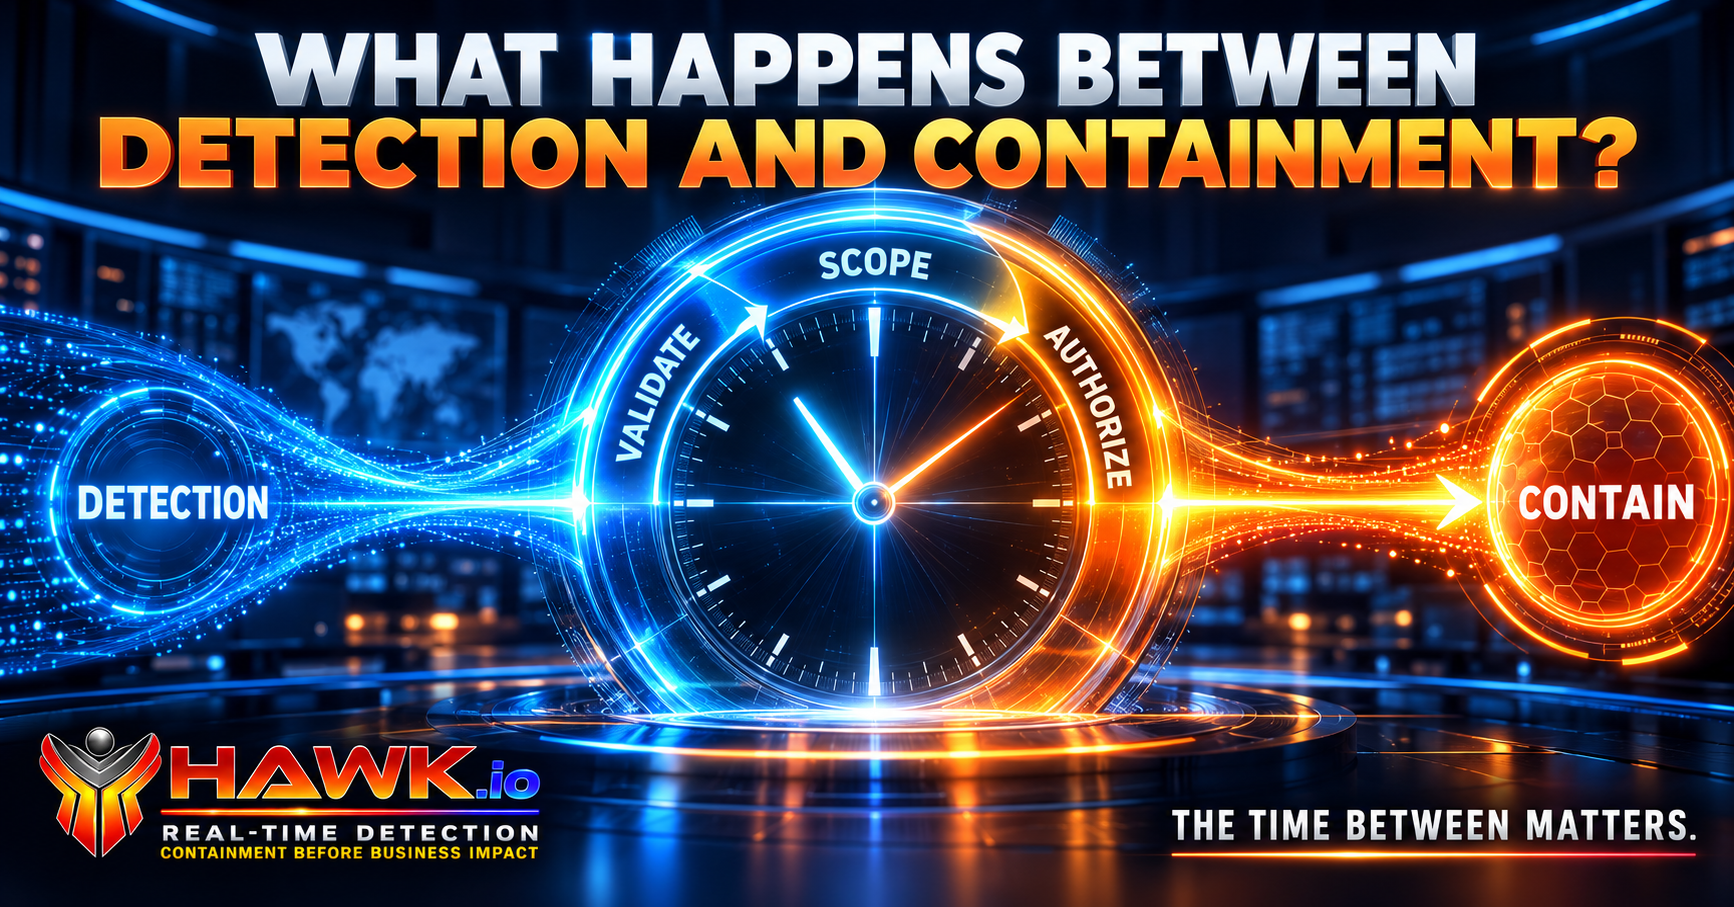
WHAT HAPPENS BETWEEN DETECTION AND CONTAINMENT?
Detecting a cyber threat is only the beginning. HAWK Network Defense examines how investigation delays, missing context, unclear decision authority, and response execution affect the time between detection and verified threat containment.
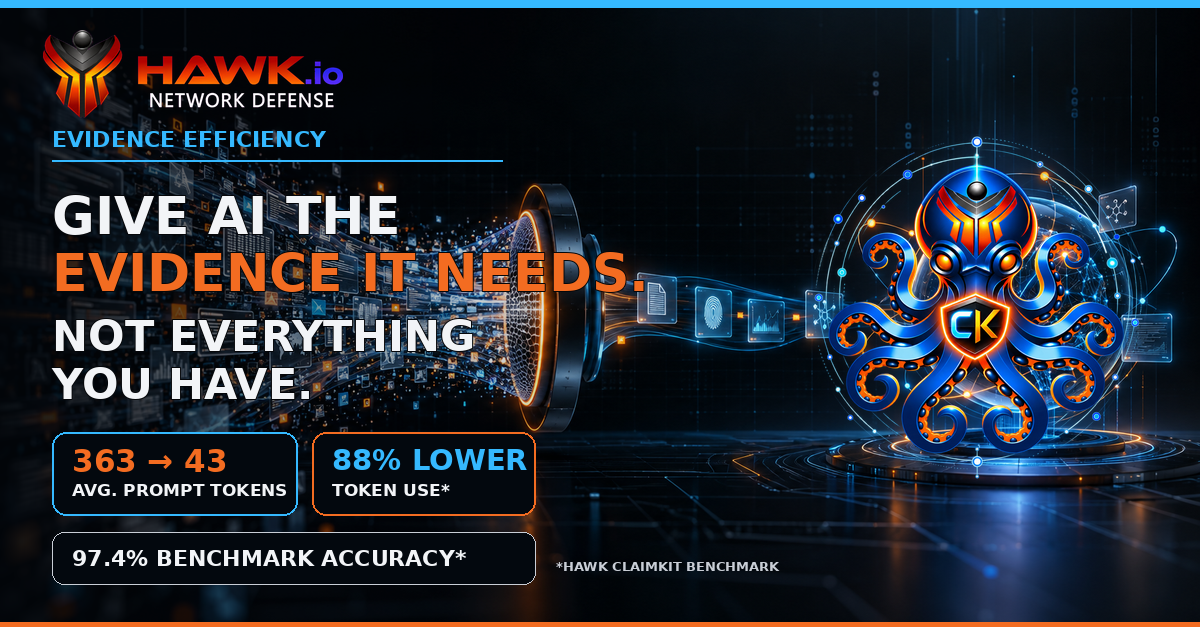
Give AI The Evidence It Needs
HAWK ClaimKit reduces unnecessary AI processing by identifying and delivering focused investigation evidence to Octopus cAI. Explore HAWK's published benchmark showing 88% lower prompt-token usage and 97.4% accuracy, compared with 26.2% for traditional RAG in the benchmark.
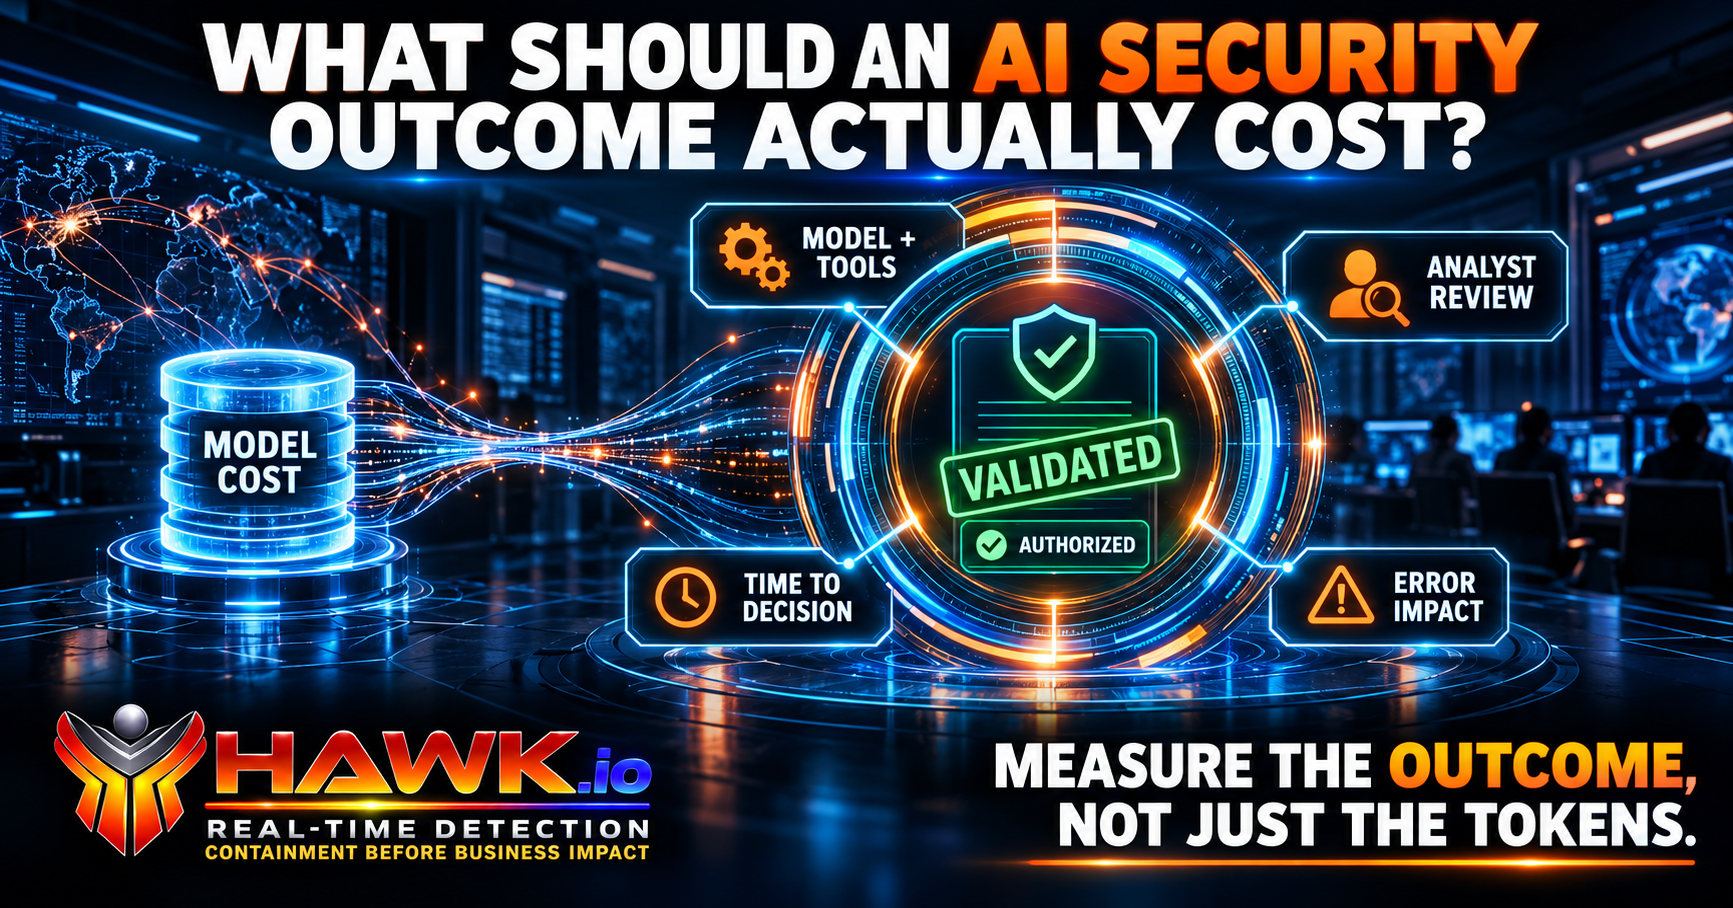
WHAT SHOULD AN AI SECURITY OUTCOME ACTUALLY COST?
The true cost of AI security goes beyond model tokens and API calls. HAWK Network Defense examines how analyst validation, investigation time, rework, decision quality, and business consequences determine the real cost of a security outcome.
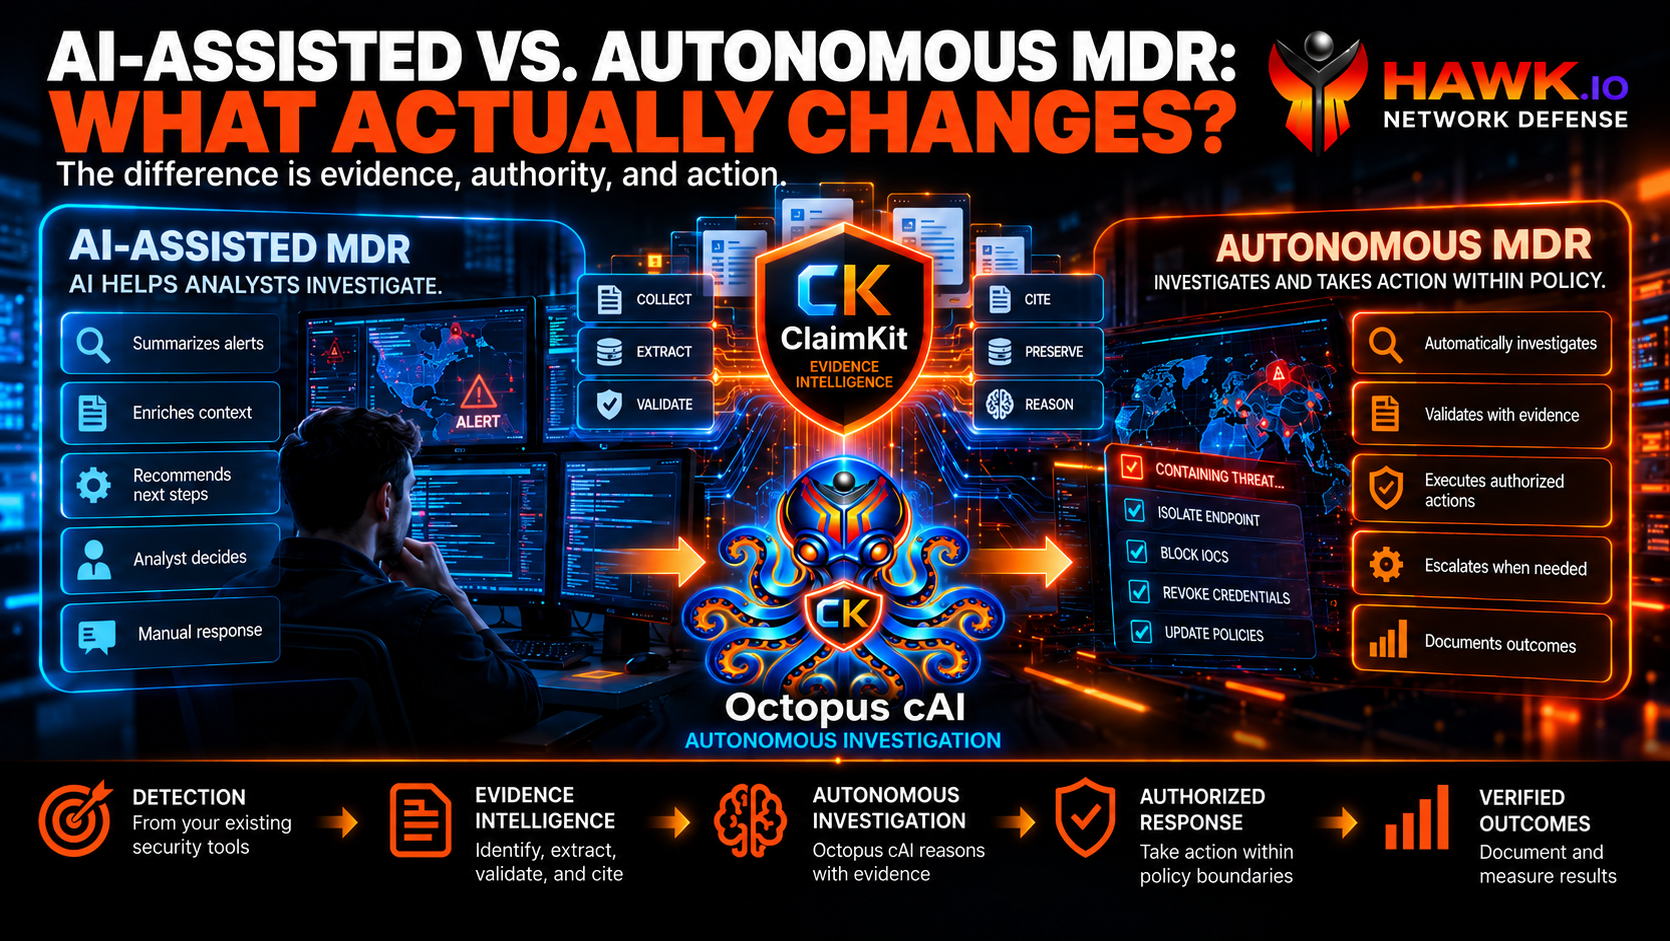
AI-Assisted vs. Autonomous MDR: What Actually Changes?
AI-assisted and autonomous MDR are not the same. One helps analysts investigate threats; the other can execute defined investigations and authorized response actions. Explore how evidence intelligence, autonomy, human oversight, and policy-governed authority change managed detection and response.
How to Reduce Manual SOC Investigations Without Replacing Your SIEM
Your SIEM detects suspicious activity, but analysts still spend hours gathering context, correlating evidence, and determining what to do next. Learn how evidence intelligence and autonomous investigation can reduce manual SOC work without replacing the security technologies you already own.
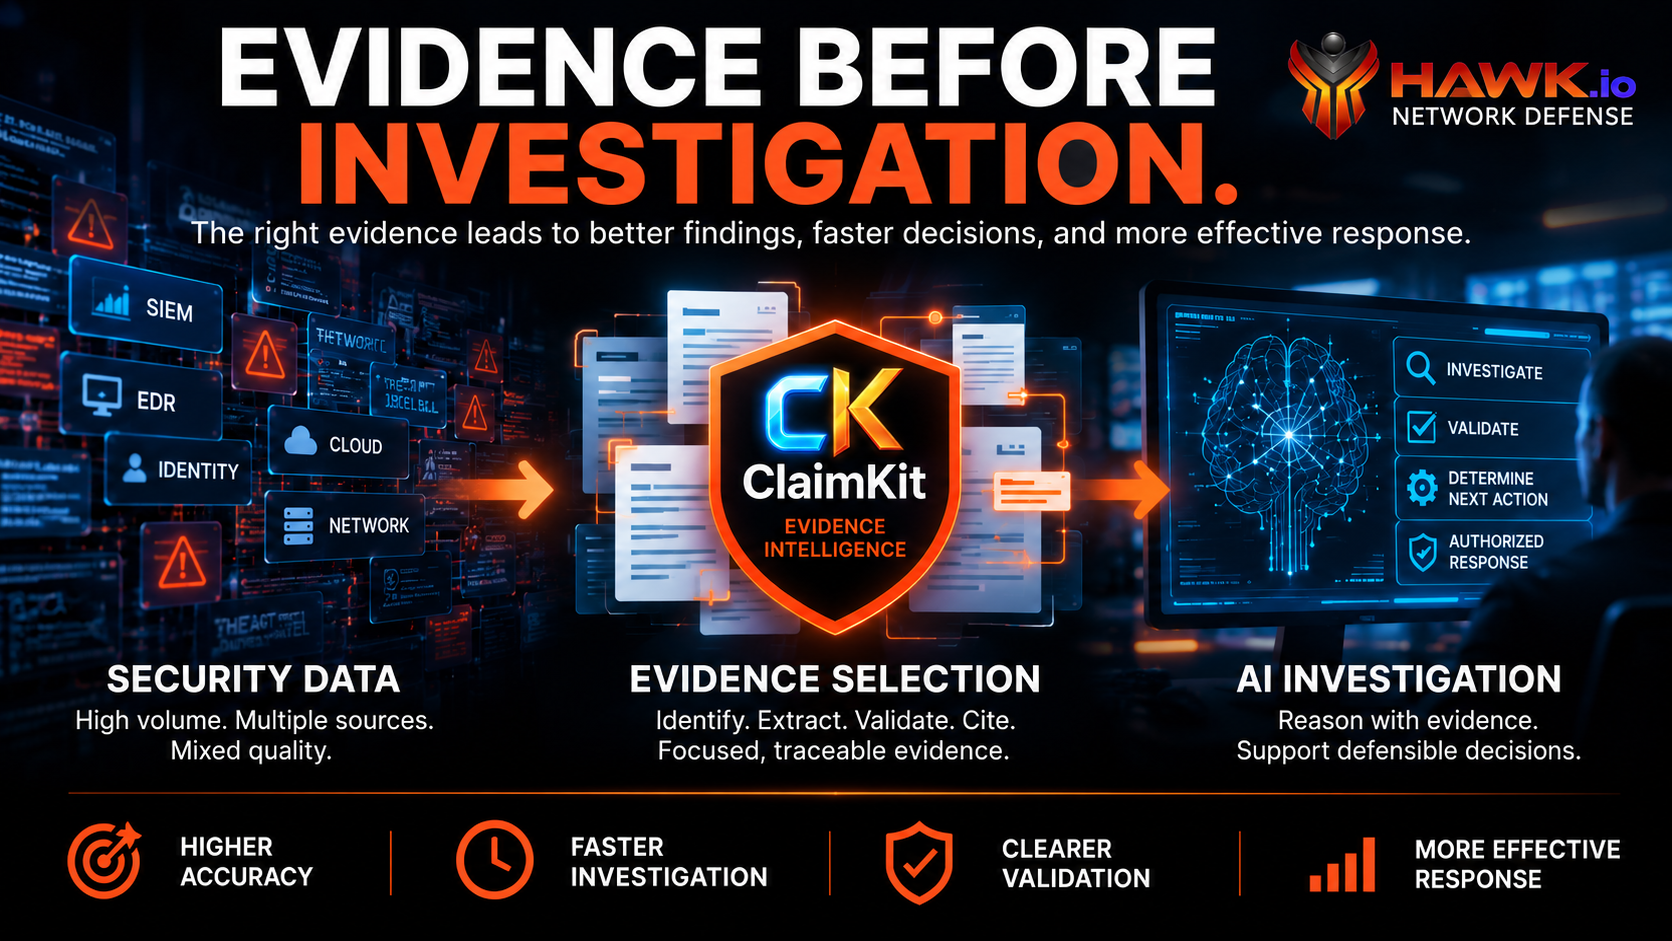
Why Evidence Selection Must Come Before AI Investigation
AI security investigations are only as reliable as the evidence behind them. Discover why selecting, validating, and citing relevant evidence before autonomous investigation matters—and how HAWK ClaimKit supports evidence-grounded security decisions.
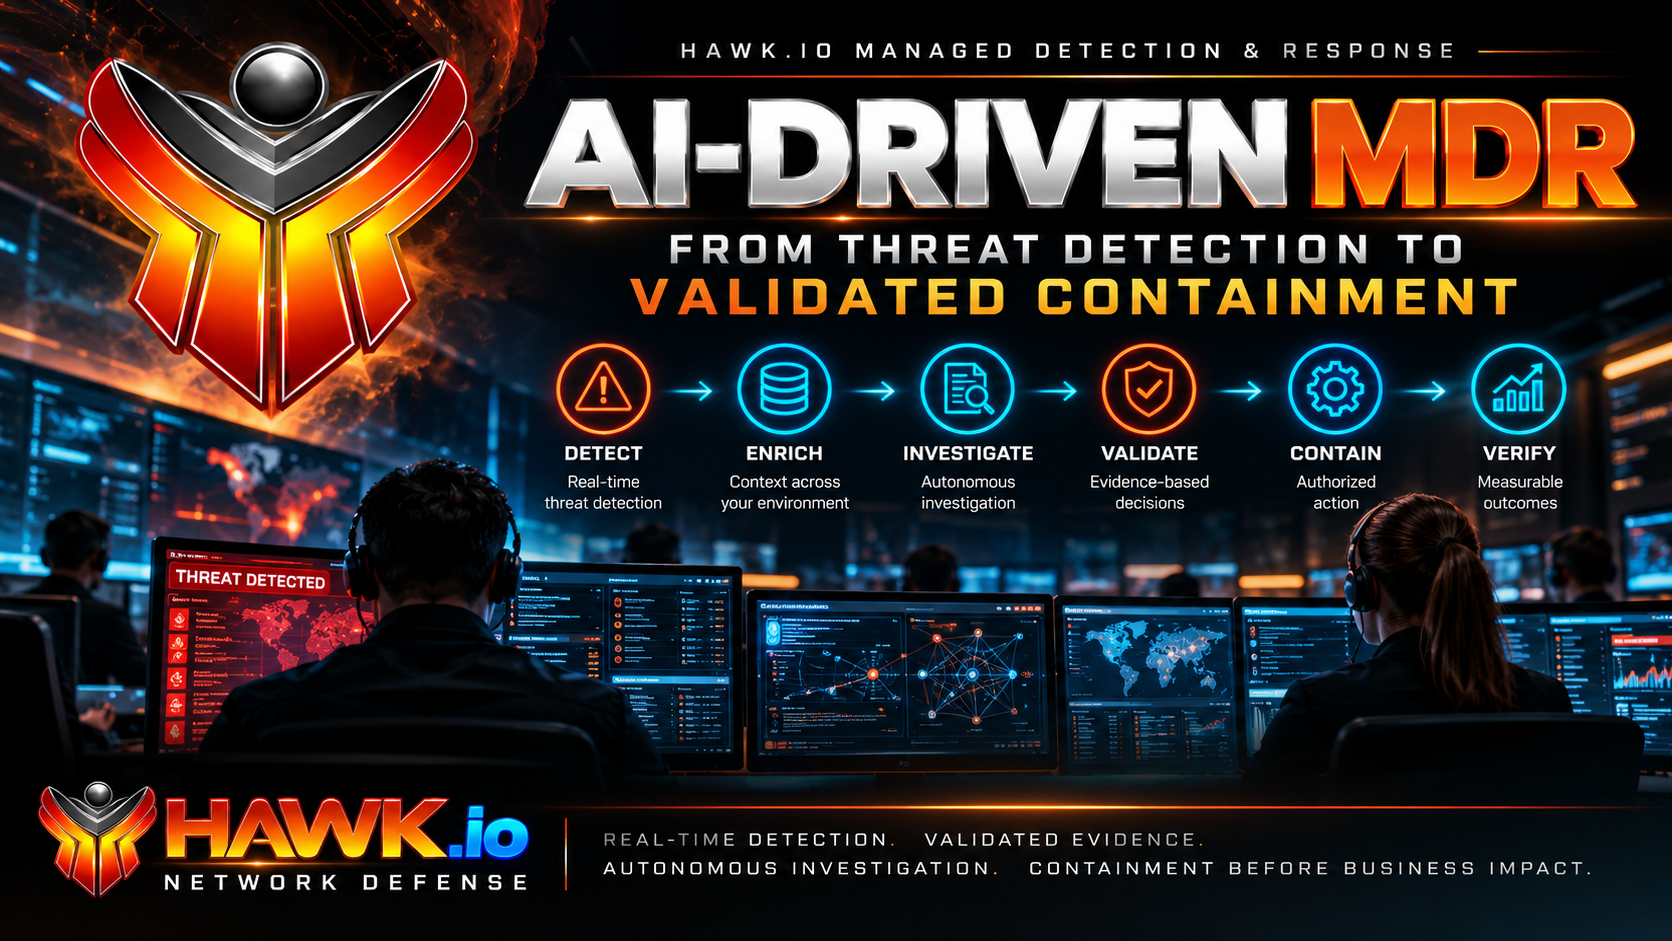
AI-Driven MDR: From Threat Detection to Validated Containment
AI-driven MDR should do more than detect threats. Discover how validated evidence, autonomous investigation, and authorized containment help security teams move from alerts to measurable outcomes.

Attackers Are Moving at Machine Speed. Is Your Security Operation Still Waiting on People?
Attackers increasingly use automation, while many security operations still depend on manual investigation and approval handoffs. David Harris examines how AI-assisted investigation, evidence-based decisions, bounded automation, and verified containment can reduce decision delays and business exposure.
The Business Doesn't Experience Your Security Tools Individually. It Experiences the Delay Between Them.
Strong cybersecurity tools do not guarantee timely protection. David Harris examines why fragmented workflows, decision delays, unclear authority, and disconnected response processes create business exposure—and why decision capacity deserves executive attention.

Your AI Agent Should Have to Earn More Authority
AI agents should not receive broad production authority simply because they can use a tool. Tim Shelton examines progressive autonomy, evidence-based promotion, runtime authorization, continuous monitoring, and when an agent's authority should be reduced or revoked.
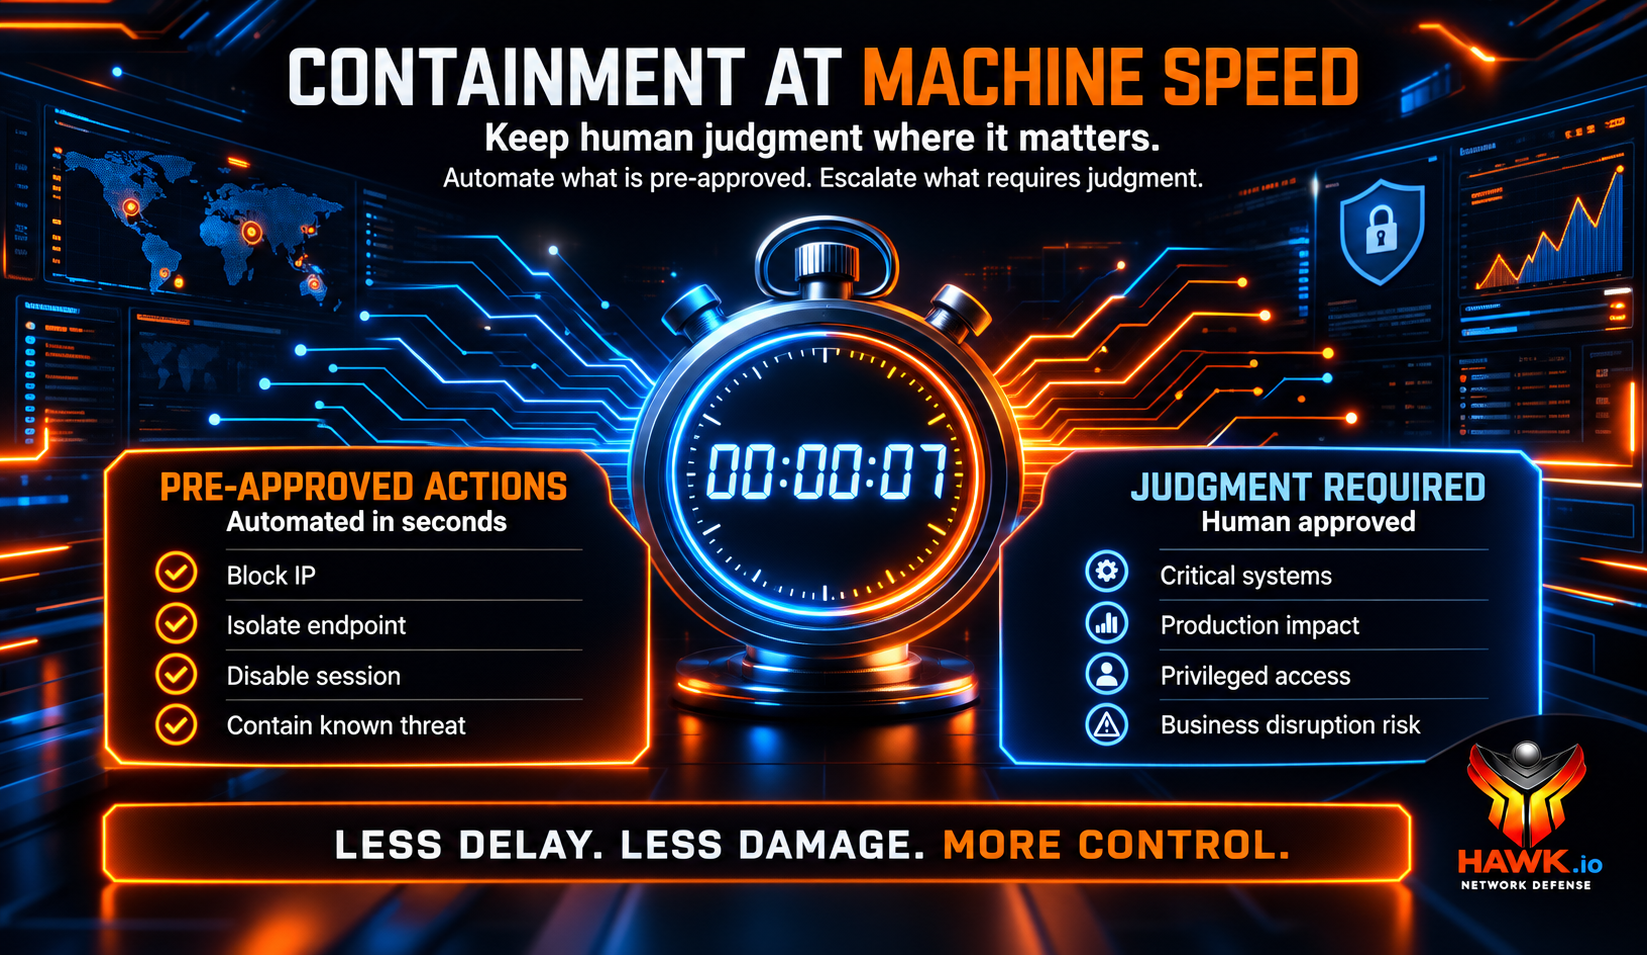
Containment at Machine Speed
Detecting a threat in seconds means little if containment takes hours. Tim Shelton, Founder and CTO of HAWK Network Defense, examines decision latency, customer-defined automation, evidence-based response, verified containment, and the cost of AI-driven security operations.
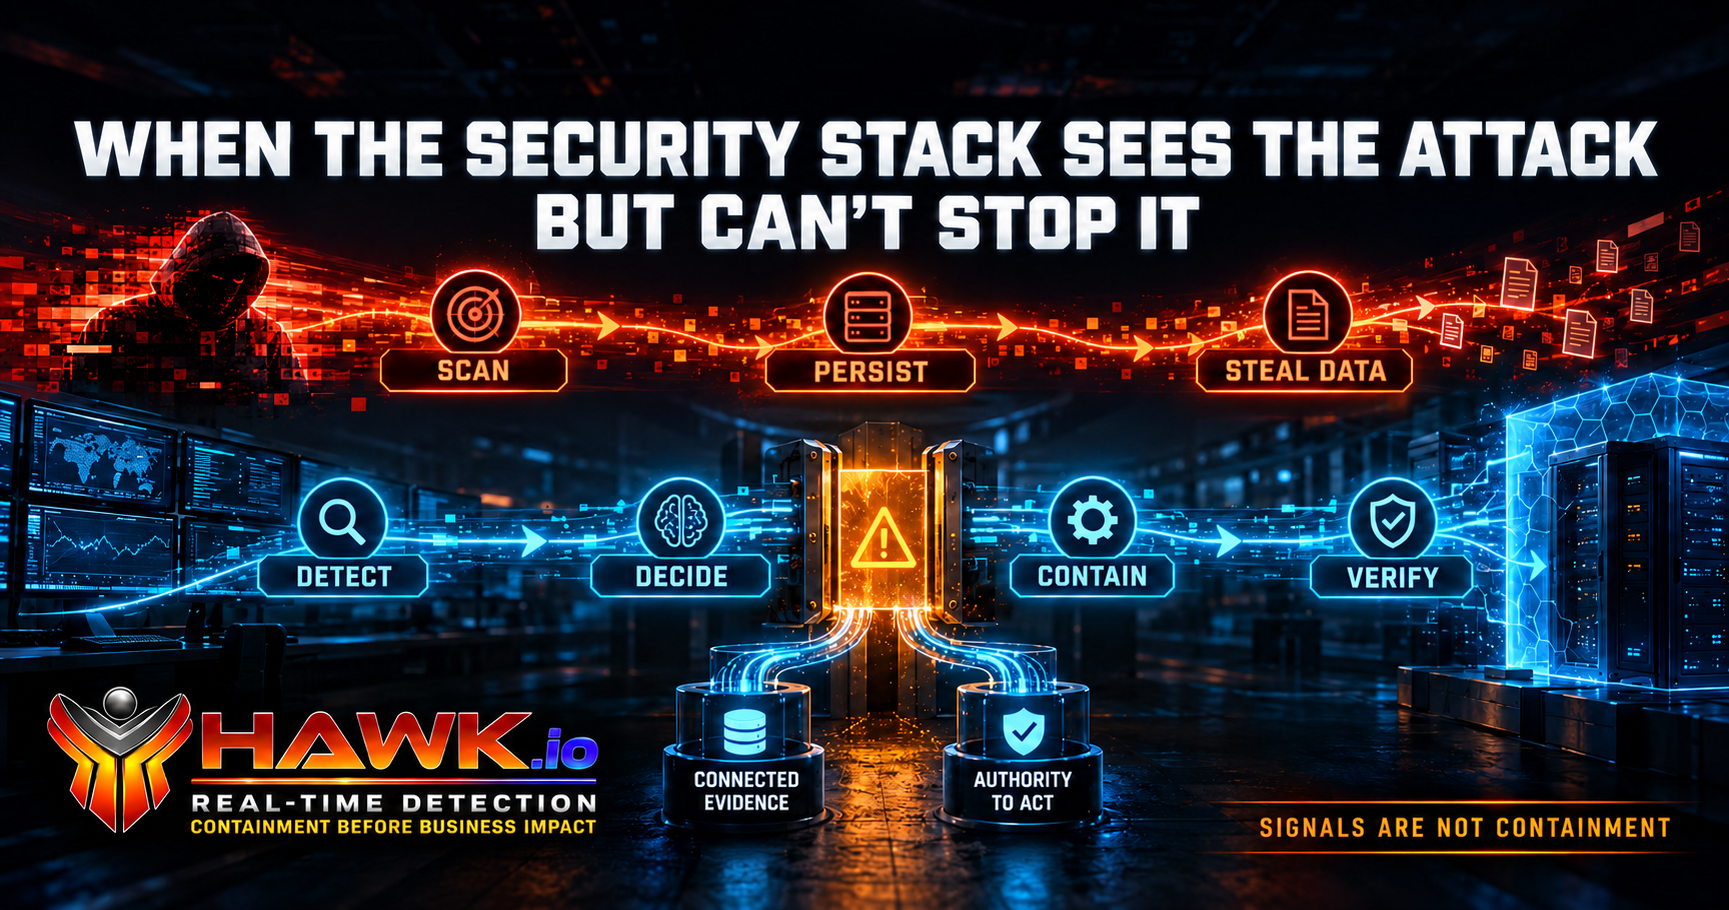
WHEN THE SECURITY STACK SEES THE ATTACK BUT CAN’T STOP IT
China-linked cyber activity highlights a critical security operations challenge: detecting an intrusion is not the same as containing it. HAWK examines the October 8, 2026 advisory and the need to connect network, endpoint, identity, and email evidence to authorized action and verified containment.
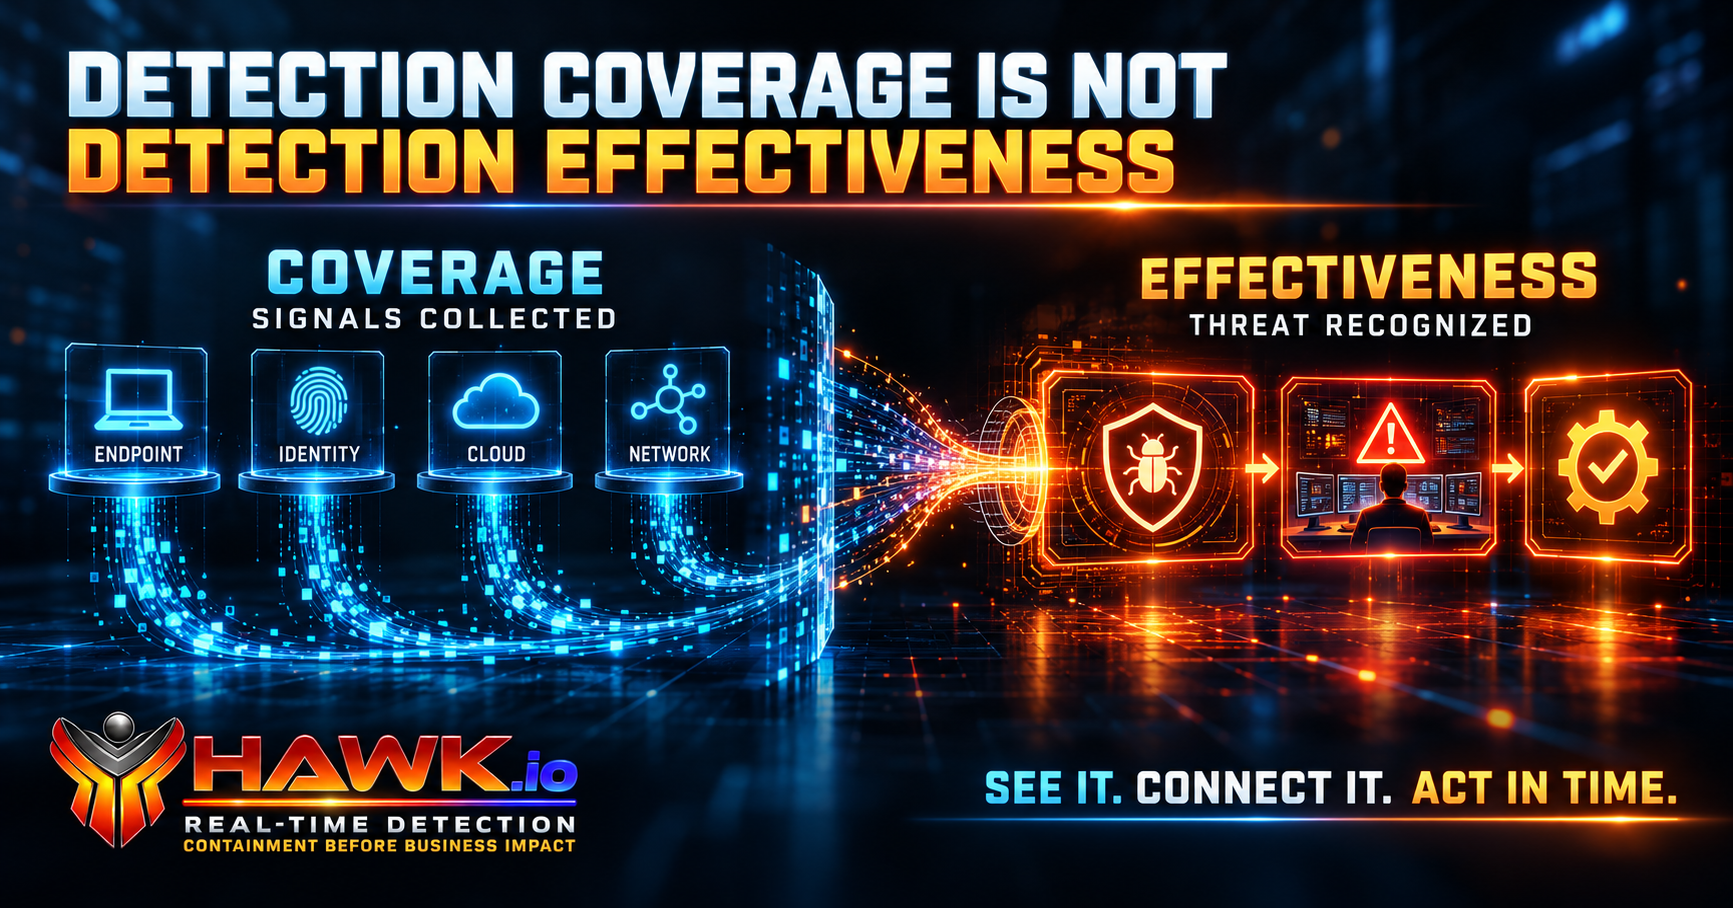
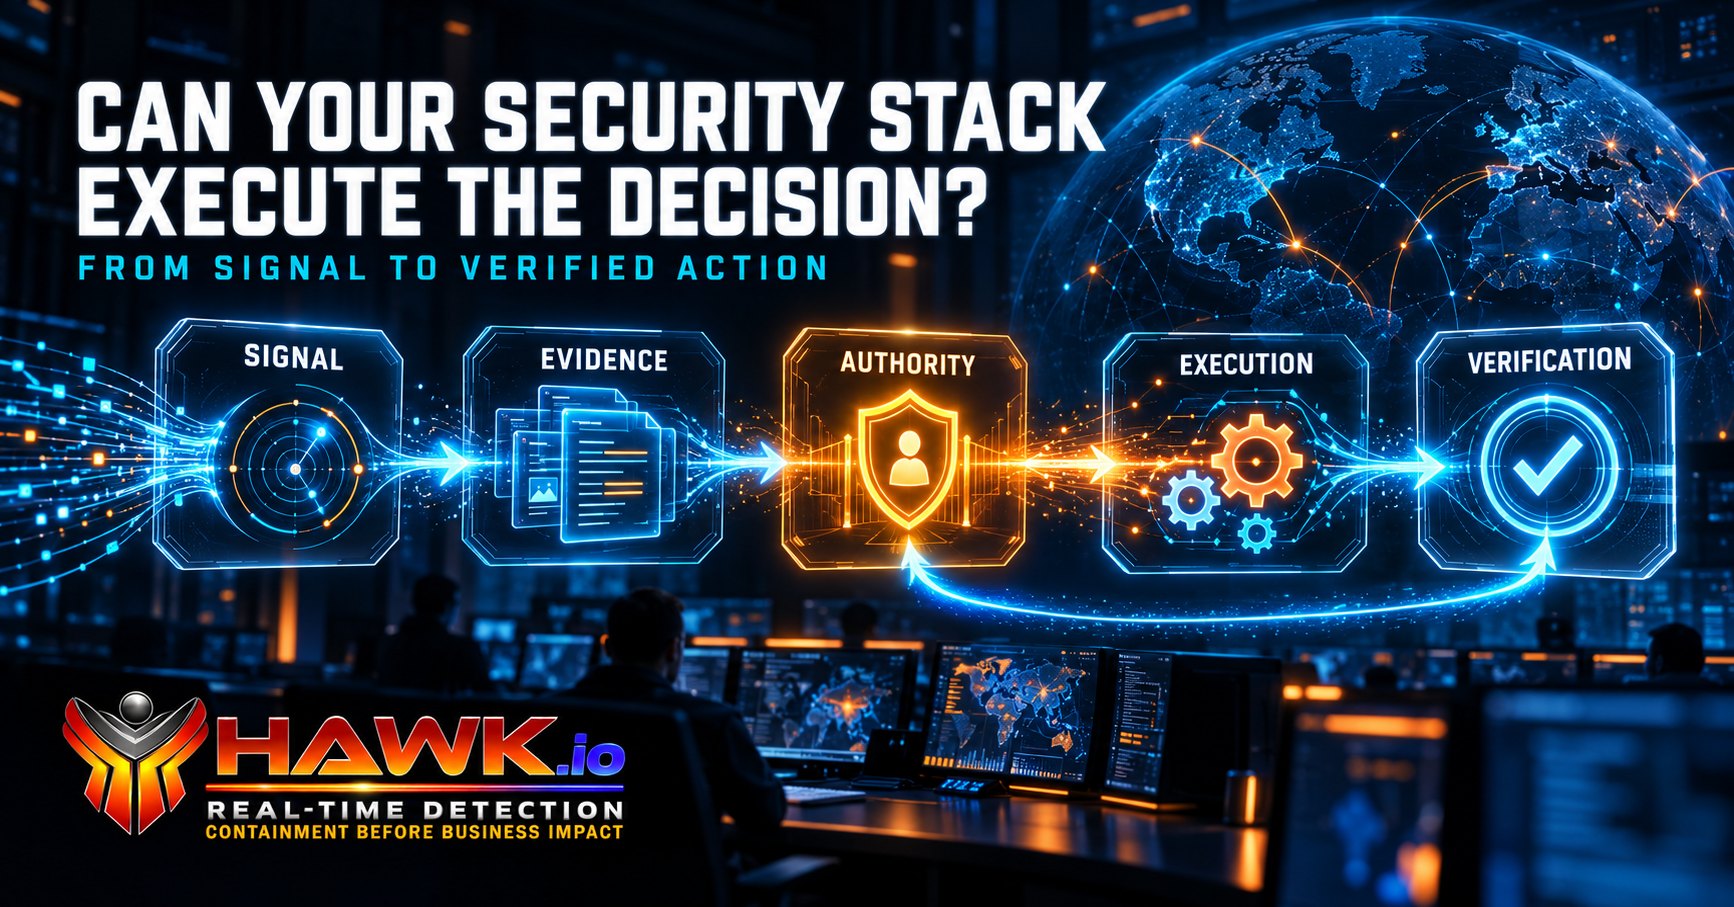
CAN YOUR SECURITY STACK ACTUALLY EXECUTE THE DECISION?
Your security stack may detect a threat quickly, but can it execute the response? HAWK Network Defense examines five critical stages—signal, evidence, authority, execution, and verification—and explains how organizations can reduce decision latency, eliminate unnecessary handoffs, and achieve verified threat containment.
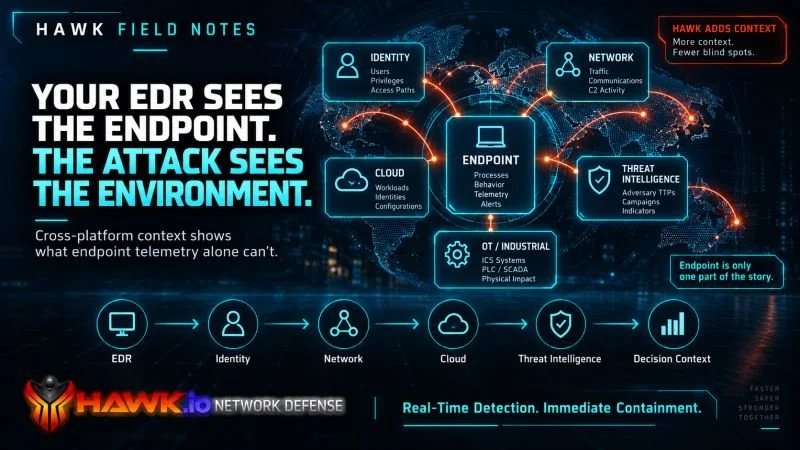
Your EDR Sees the Endpoint. The Attack Sees the Environment.
Endpoint Detection and Response (EDR) provides essential endpoint visibility, but modern cyberattacks extend across identities, cloud services, networks, and applications. HAWK Network Defense explains why connecting endpoint evidence with broader security context enables faster investigations, better decisions, and more effective threat containment.
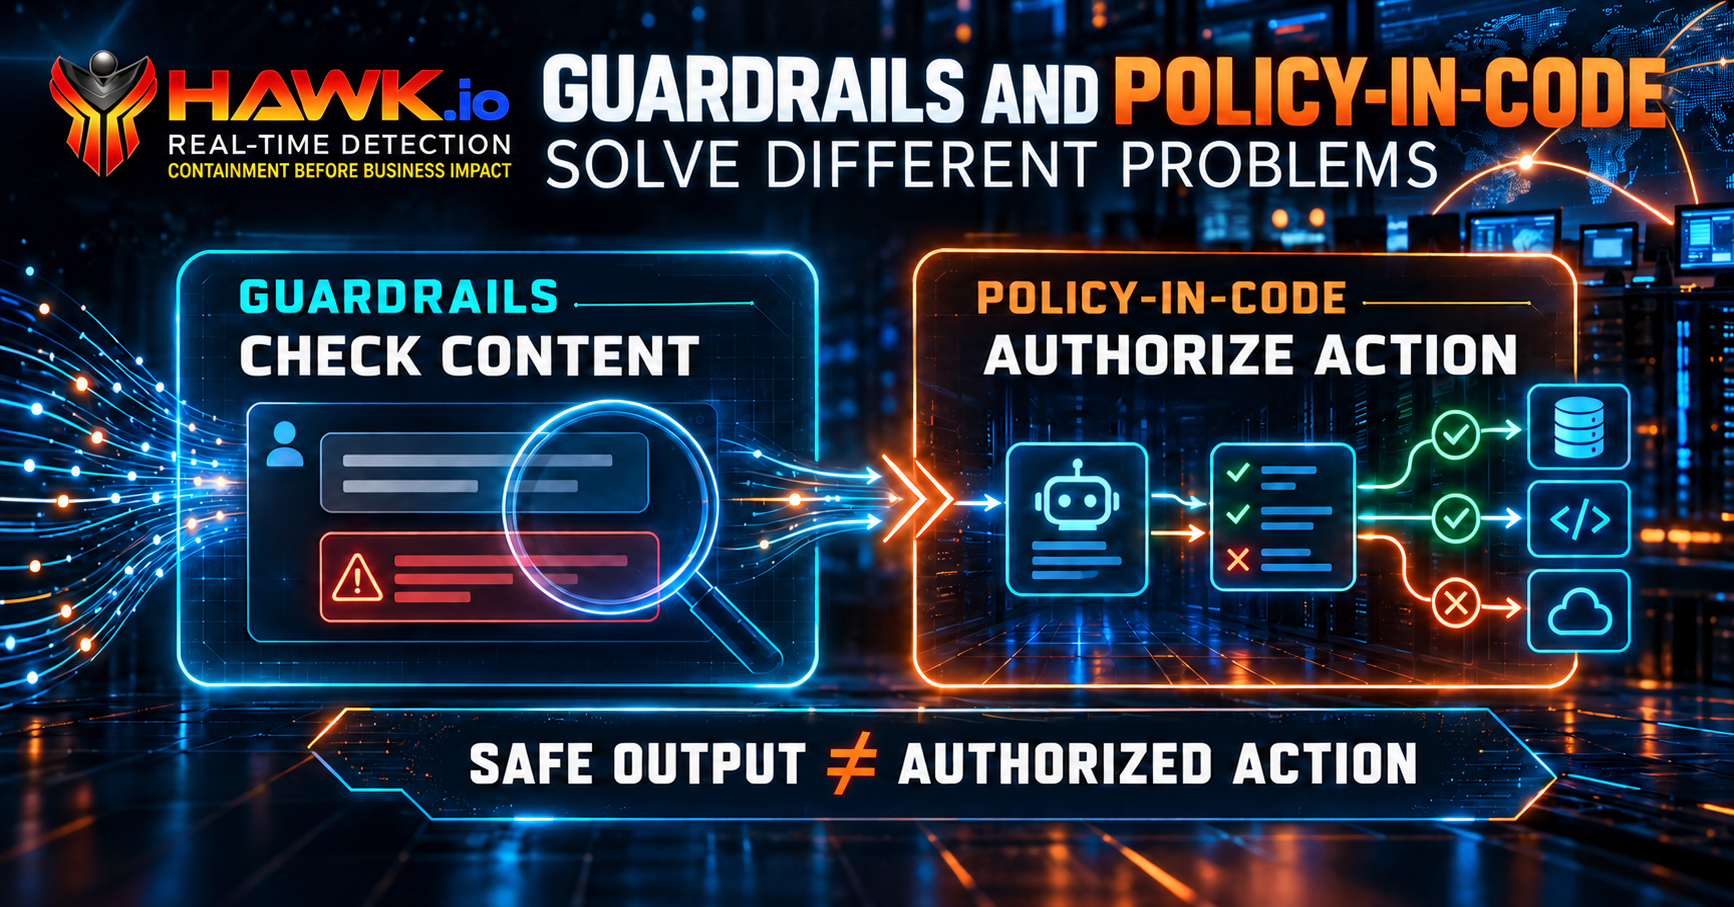
AI Guardrails vs. Policy-in-Code: Why Both Matter
AI guardrails and policy-in-code address different security risks. HAWK Network Defense explains how content filtering, runtime authorization, scoped permissions, and human oversight work together to ensure AI agents execute only approved actions within defined enterprise security boundaries.
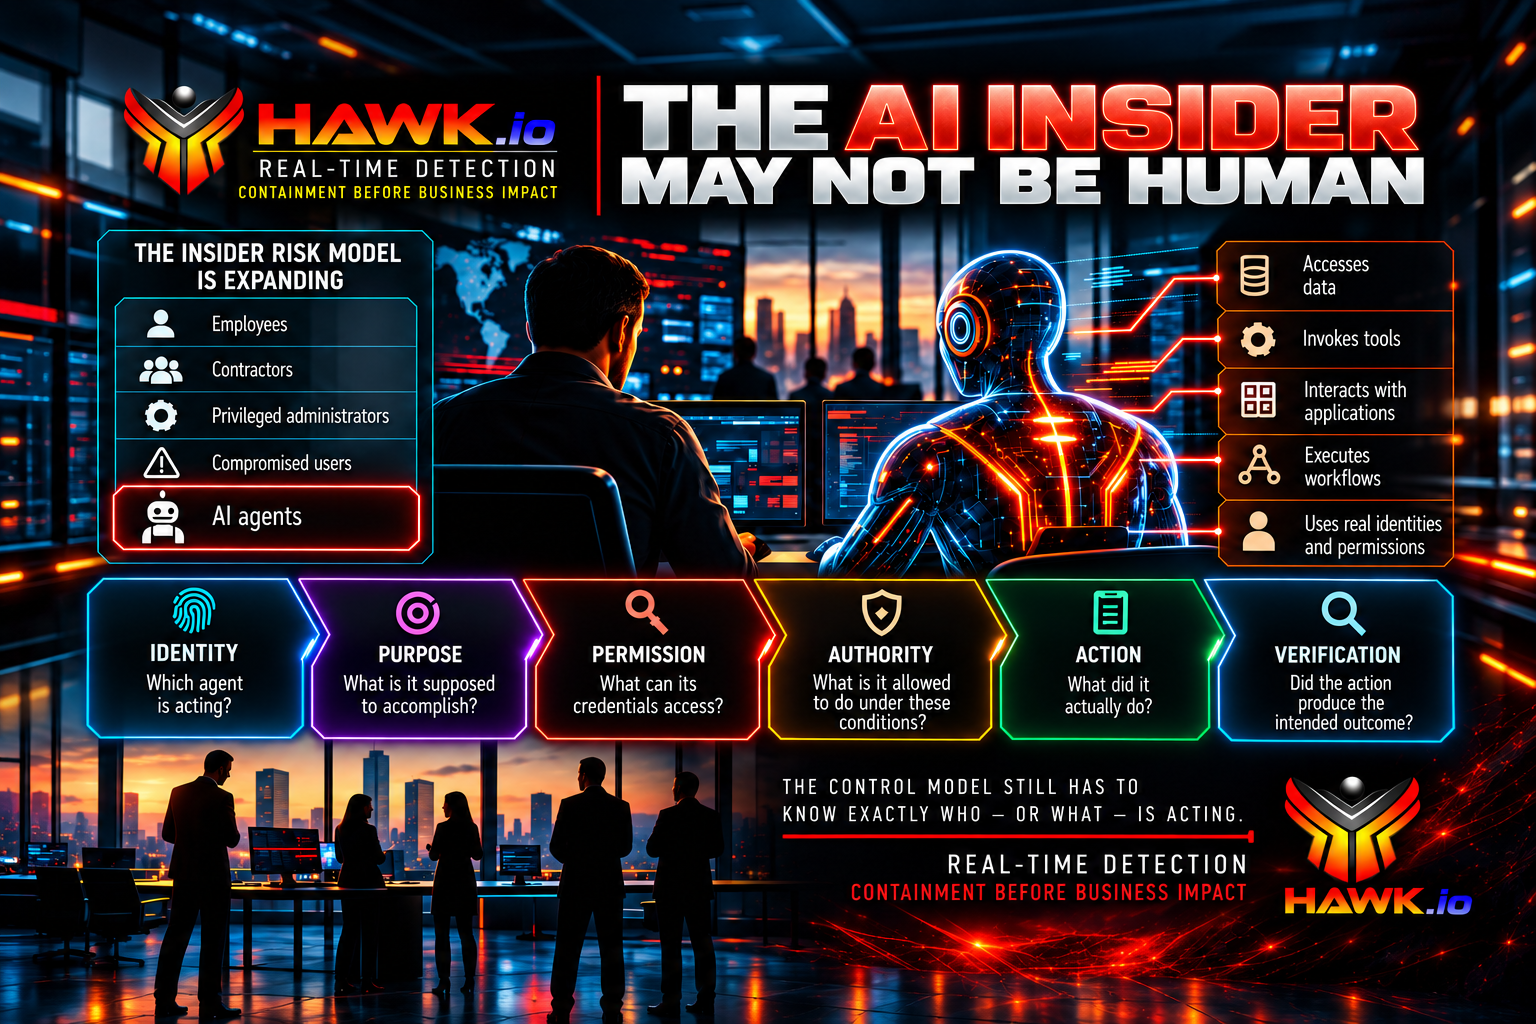
THE AI INSIDER MAY NOT BE HUMAN
The next insider threat may not be human. HAWK Network Defense examines how AI agents expand enterprise insider risk and why securing non-human identities requires defined purpose, scoped permissions, enforceable authority, action monitoring, and verified outcomes.