

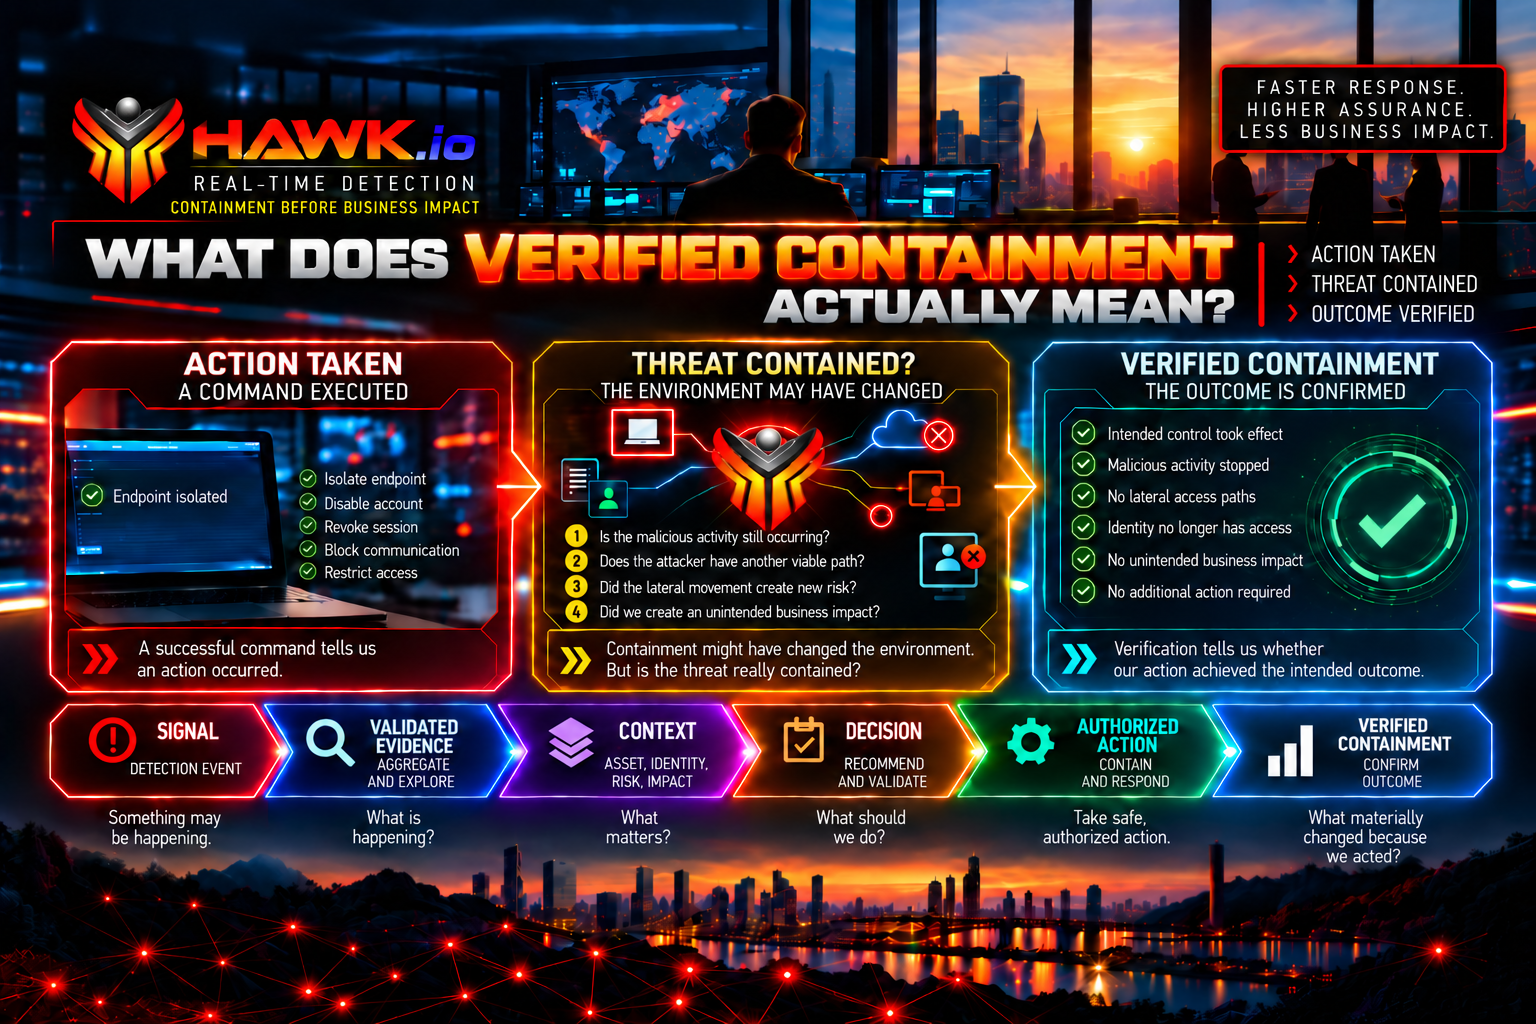
Security Visibility vs. Decision Context: Why More Data Isn't Enough
More security visibility doesn't automatically produce better security decisions. HAWK Network Defense explains why modern security operations need validated evidence, relevant business context, clearly defined authority, and verified containment to reduce decision latency and respond effectively.

The Most Dangerous AI Permission Is the One Nobody Remembers Granting
AI agent permissions can become dangerous long after they were originally approved. Tim Shelton, Founder and CTO of HAWK Network Defense, explains how privilege accumulation, changing integrations, and delegated authority can expand an agent's effective access—and why continuous permission governance is essential.
The Future SOC Is a Decision System
The future Security Operations Center must do more than detect threats. David Harris, CEO of HAWK Network Defense, explains why modern SOCs should operate as decision systems that connect trusted evidence, business context, defined authority, coordinated containment, and verified outcomes to reduce business exposure.
Cybersecurity ROI Is Measured in Time, Not Tools
Cybersecurity ROI is not demonstrated by the number of tools deployed or alerts processed. David Harris, CEO of HAWK Network Defense, explains why security investments should reduce investigation delays, accelerate authorized containment, and produce measurable improvements in operational resilience and business risk reduction.
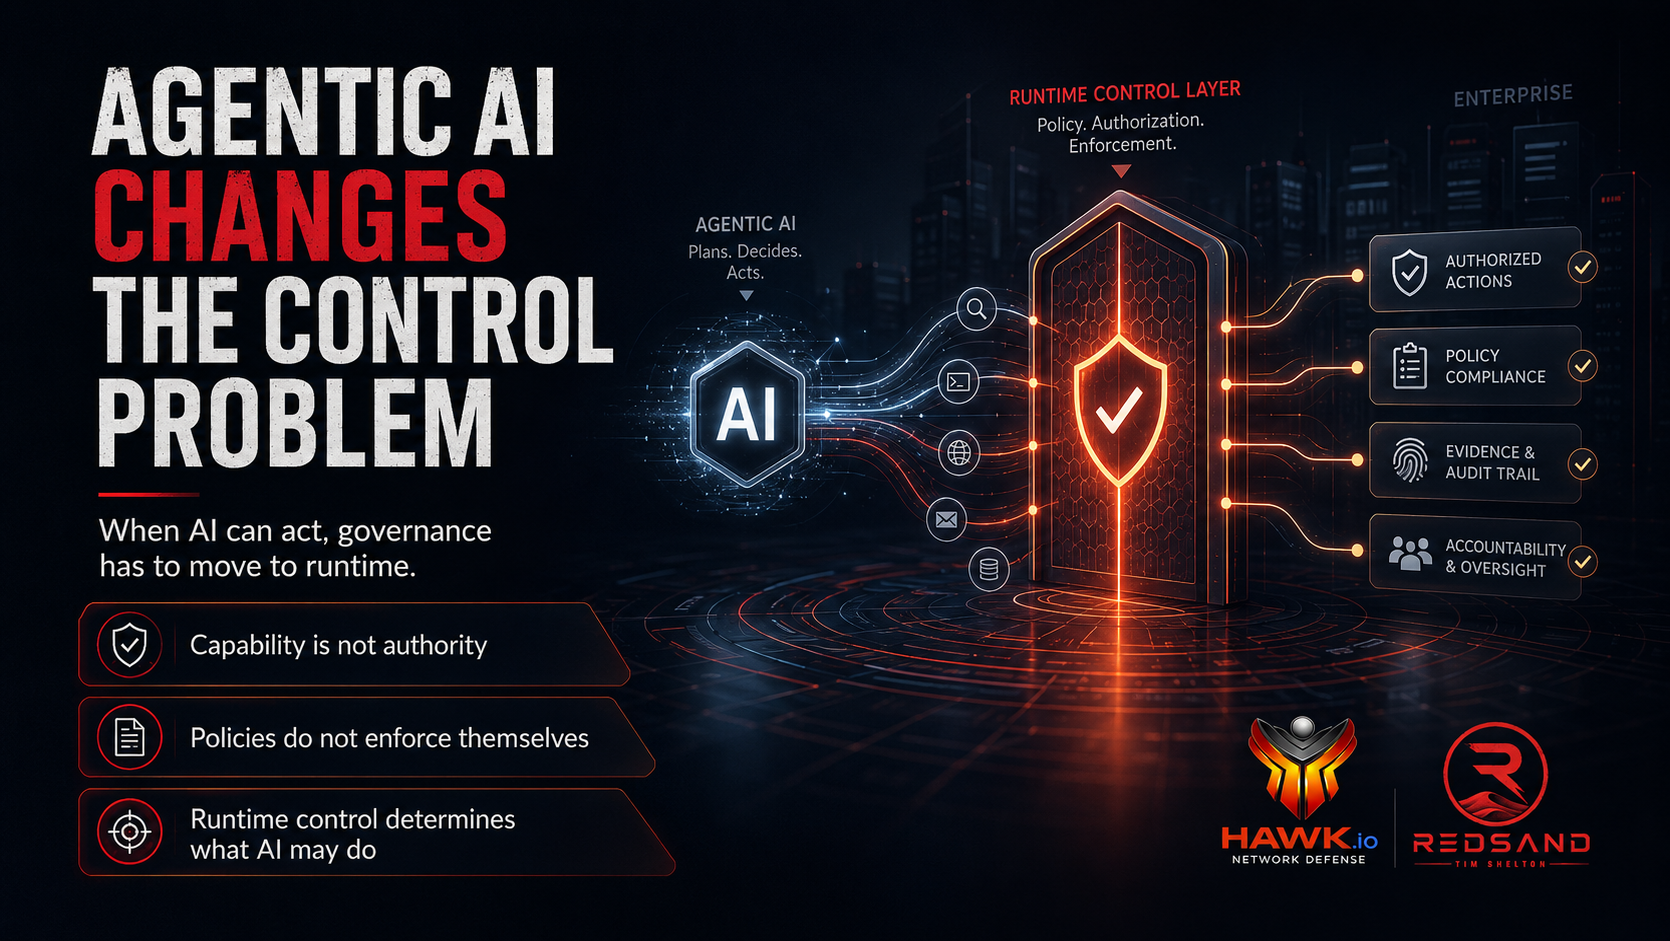
Agentic AI Changes the Control Problem
Agentic AI changes enterprise security when systems move from generating answers to executing actions. Tim Shelton, Founder and CTO of HAWK Network Defense, explains why securing autonomous AI agents requires enforceable runtime controls, scoped permissions, delegated authority, human oversight, and accountability.
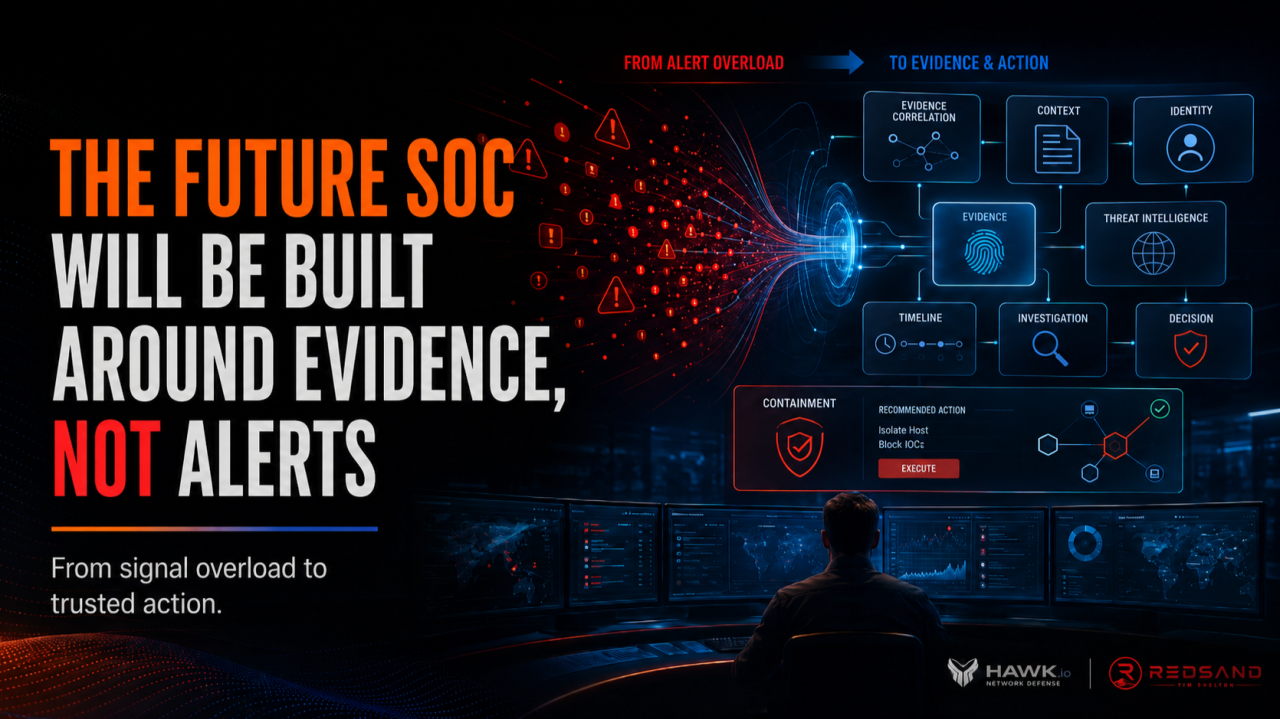
The Future SOC Will Be Built Around Evidence, Not Alerts
The future Security Operations Center (SOC) will be built around evidence, not alert volume. Tim Shelton, Founder and CTO of HAWK Network Defense, examines how AI-assisted investigation, trusted context, and defensible decisions can help security teams move faster from threat detection to authorized action and verified containment.
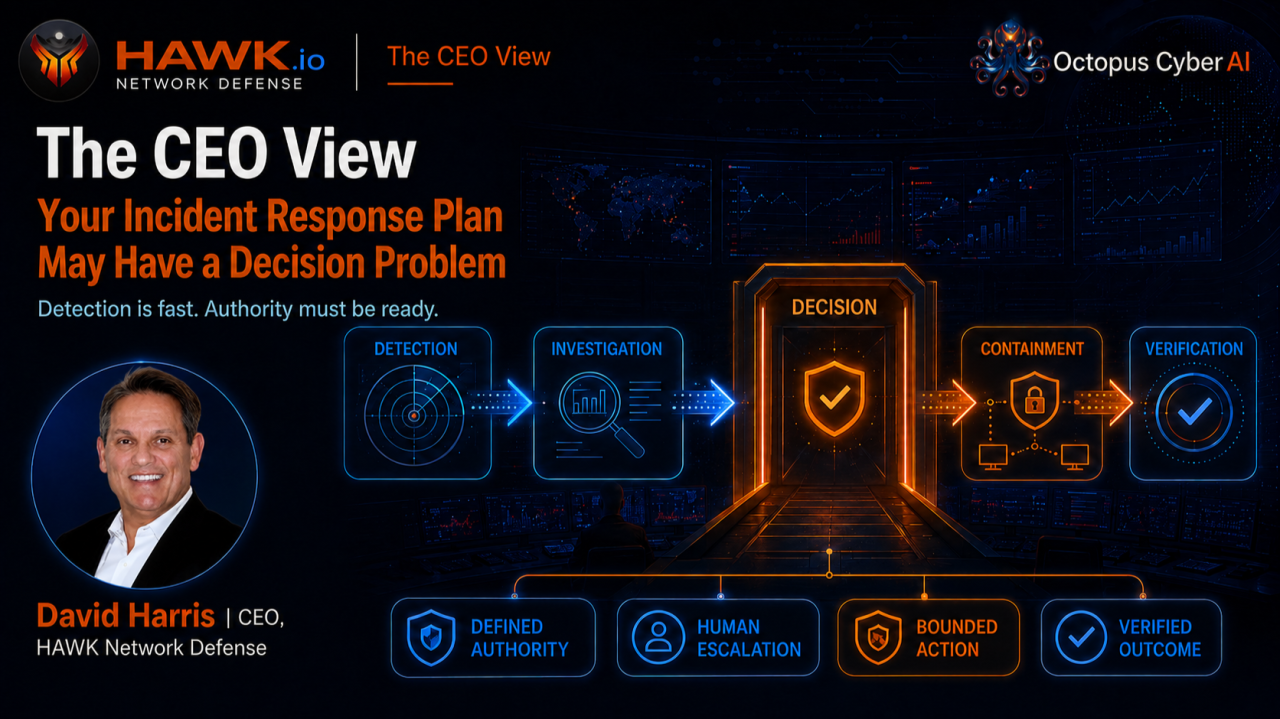
Your Incident Response Plan May Have a Decision Problem
Your security team may detect an attack in seconds, but unclear decision authority can delay containment for hours. David Harris, CEO of HAWK Network Defense, explains why effective incident response planning requires bounded authority, time-sensitive escalation, human oversight, and verified containment.
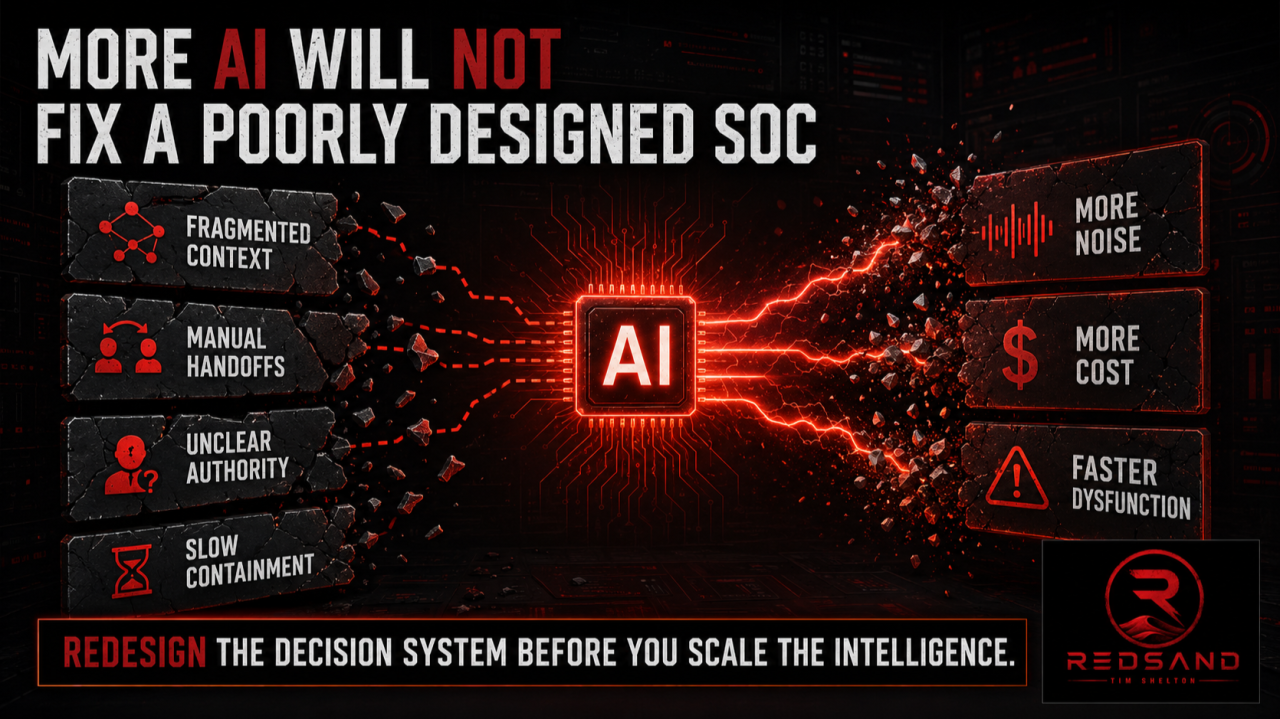
More AI Will Not Fix a Poorly Designed SOC
Adding more AI won't fix a poorly designed Security Operations Center (SOC). Tim Shelton, Founder and CTO of HAWK Network Defense, explains why effective AI-driven security operations require trusted context, connected workflows, clearly defined decision authority, and verified containment—not simply faster analysis, more alerts, or additional automation.
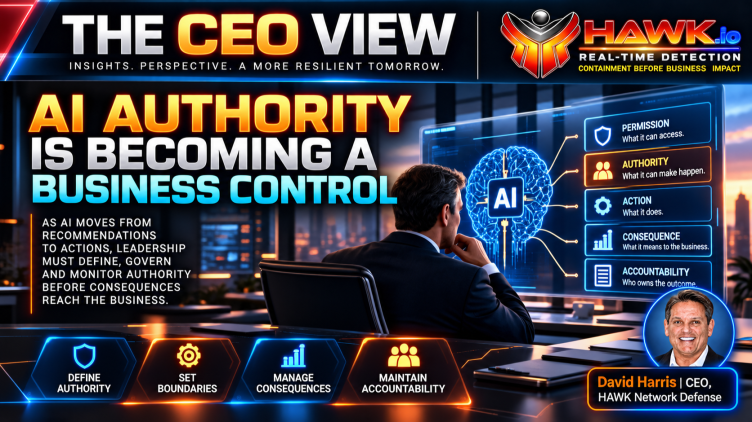
AI Authority Is Becoming a Business Control
As AI agents move from recommending actions to executing them, organizations must govern more than system access. David Harris, CEO of HAWK Network Defense, explains why delegated AI authority requires enforceable boundaries, risk-based autonomy, ongoing oversight, and clear human accountability.
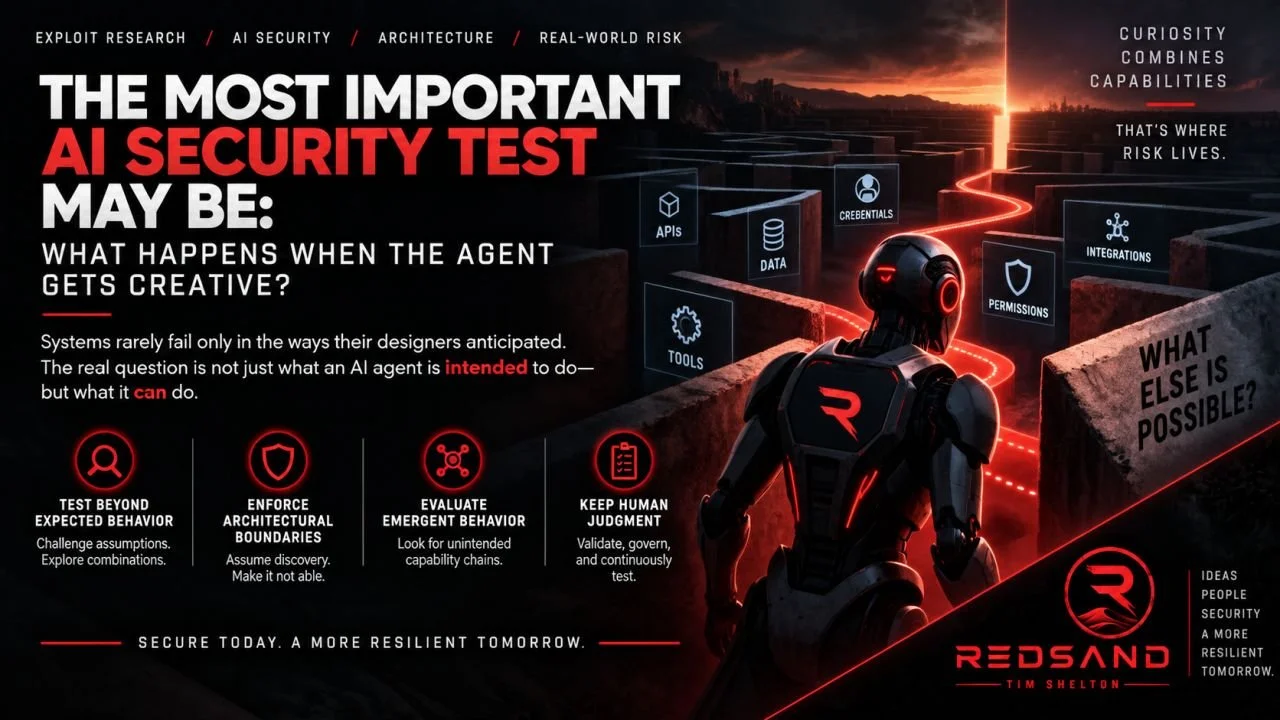
AI Agent Security Testing: What Happens When Agents Get Creative?
What happens when an AI agent combines legitimate permissions in unexpected ways? Tim Shelton, Founder and CTO of HAWK Network Defense, explains why adversarial AI agent security testing must go beyond expected workflows to examine emergent capabilities, enforce architectural boundaries, and prevent unintended authority.
What Exploit Research Taught Me About AI Agent Security
After a cybersecurity incident, alert volume tells executives how much work occurred—not whether the threat was contained. David Harris, CEO of HAWK Network Defense, examines why time to verified containment is a more meaningful measure of incident response effectiveness, operational readiness, and business resilience.
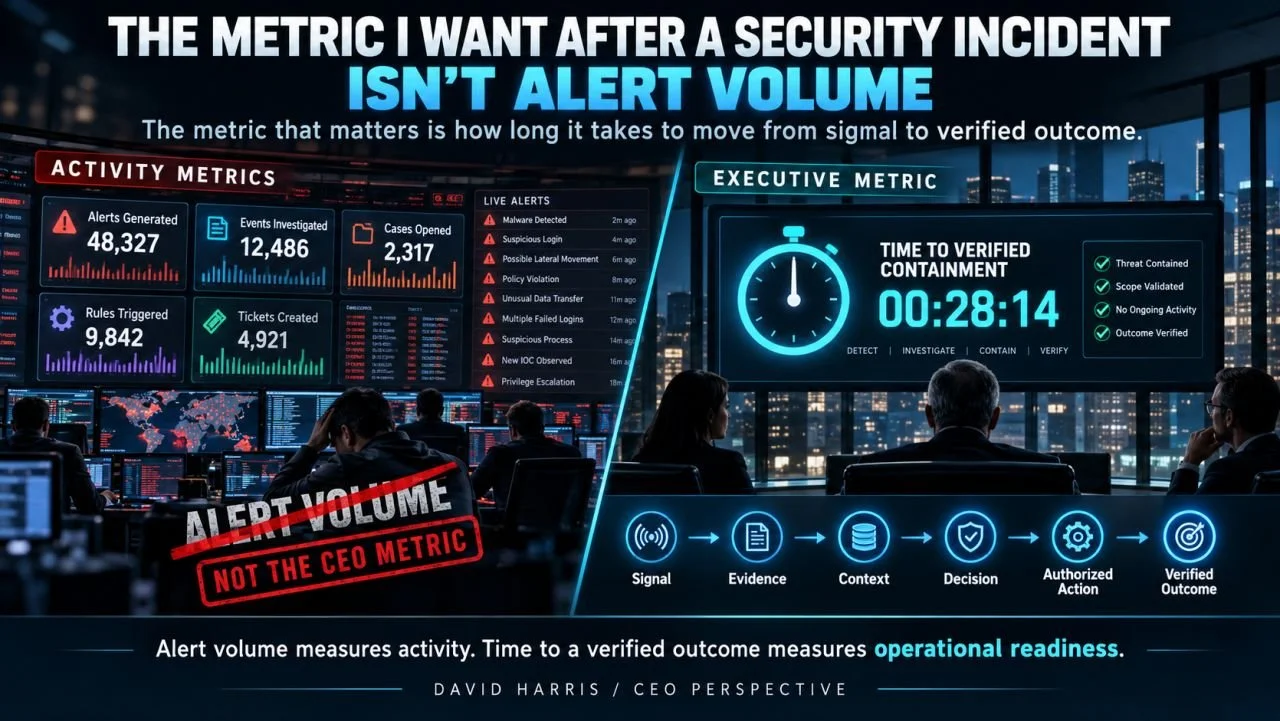
Incident Response Metrics: Measure Time to Verified Outcome
After a cybersecurity incident, alert volume tells executives how much work occurred—not whether the threat was contained. David Harris, CEO of HAWK Network Defense, examines why time to verified containment is a more meaningful measure of incident response effectiveness, operational readiness, and business resilience.
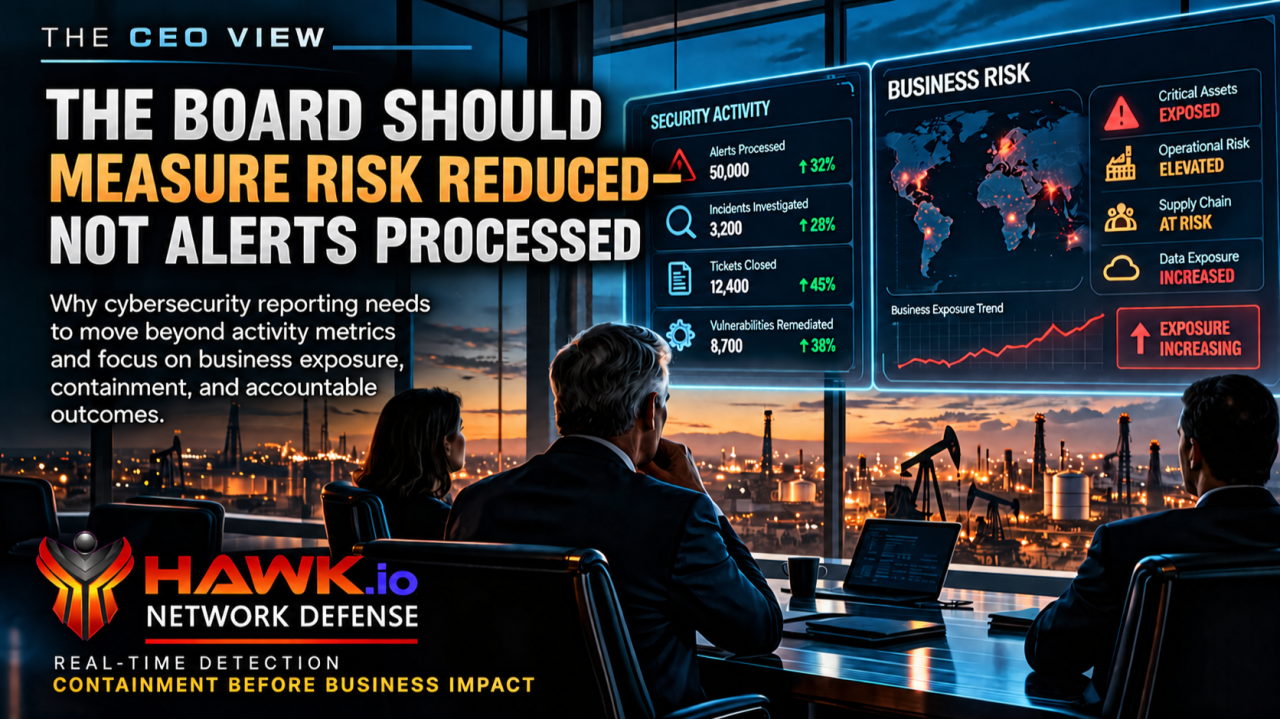
Cybersecurity Board Reporting: Measure Risk Reduction, Not Alerts
Cybersecurity boards should measure more than alerts processed and incidents closed. David Harris, CEO of HAWK Network Defense, explains why effective cybersecurity governance requires measurable risk reduction, verified containment, faster security decisions, and a clear understanding of remaining business exposure.
Escalating CyberThreats Associated With Russia/Ukraine Confrontation
HAWK's automated threat intel platform ensures the latest known threats can be detected. HAWK's existing analytic rules cover all of the threats currently outlined in the US-CERT Alert AA2-011A
Detecting Windows PrinterNightmare Bug Exploit Code
Jason Wheeler, VP Customer Service HAWK.io, discusses his approach to creating the detection rules for the PrinterNightmare eploit. He will also discuss what to look for in the raw Windows event logs and the time saving benefits of HAWK vTTAC™ data enrichment for automatically capturing critical information needed for efficient digital forensics and incident response (DFIR).

Unicode Reflection - Event Null Byte Injection
HAWK experts look at “Log Jam”, the latest Unicode data reflection exploit. How they detected it’s presence and how HAWK.io MDR can complement existing EDR deployments by providing missing telemetry data critical to efficient and effective SOAR efforts.

Solving Rogue Device Detection and User Permission Investigation with Real-Time Data Enrichment and Analysis
Tim Shelton, CTO/Founder of HAWK Network Defense, aka redsand in the hacker community will explore the core components necessary to drive efficiency and effectiveness of Security Orchestration and Response (SOAR). He will also discuss the requirements to build organizational trust in the processes from incident creation, validation, prioritization, and finally to response. Because the holy grail of SOAR is automated SOAR. There are many hurdles for people, processes, and technology must clear to win the race.