

What Is Your Organization Still Doing Because Nobody Has Questioned It?
Give recurring work a current explanation and test a bounded change before retiring an approval, report or control.
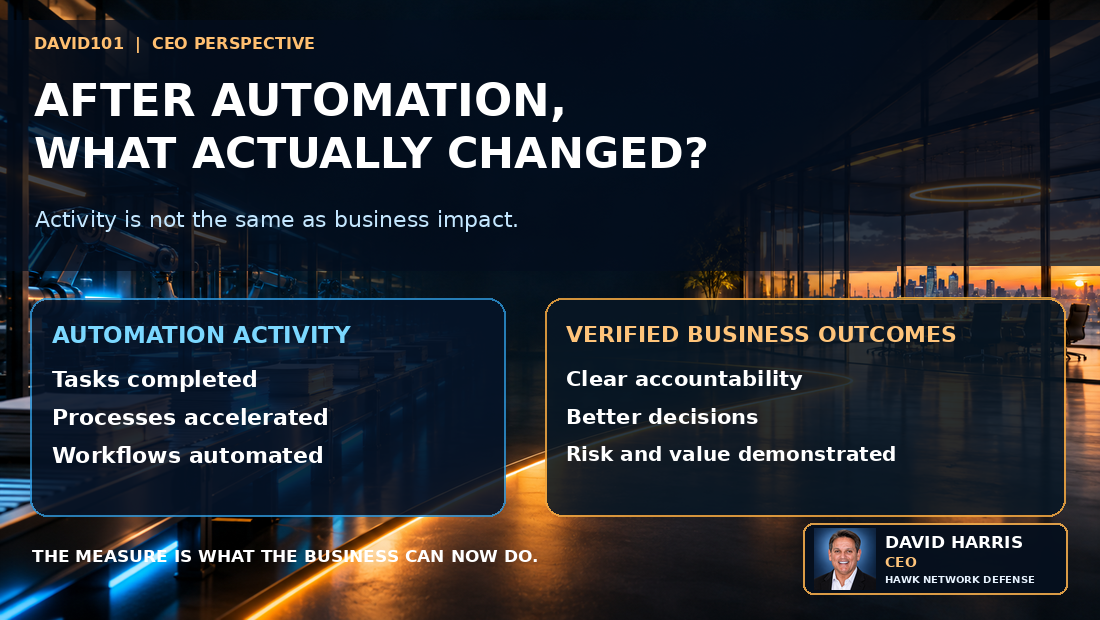
The Question After Automation Isn't “How Much Did We Automate?”
Separate deployment activity, released capacity and actual expense changes before deciding how an automation investment should proceed.
The Board Cannot Govern What It Cannot Interpret
Boards need a clear decision, not another unexplained metric. David Harris outlines how management can translate AI and cyber exposure into choices directors can evaluate.
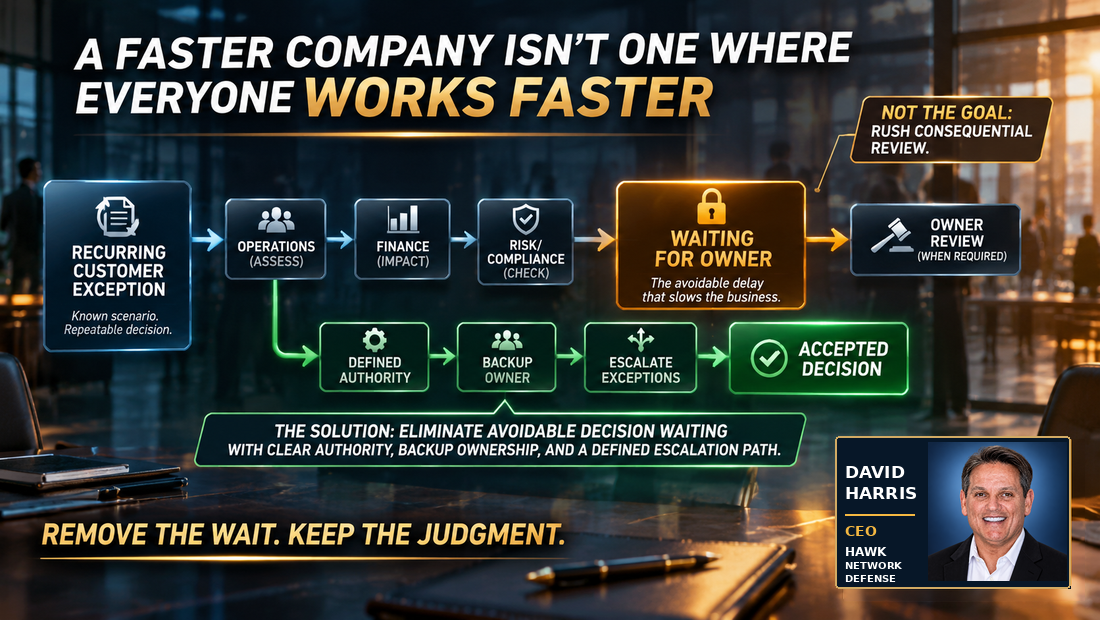
A Faster Company Isn't One Where Everyone Works Faster
Examine where recurring decisions wait, what review contributes, and how leadership can define a reliable path to an accepted outcome.
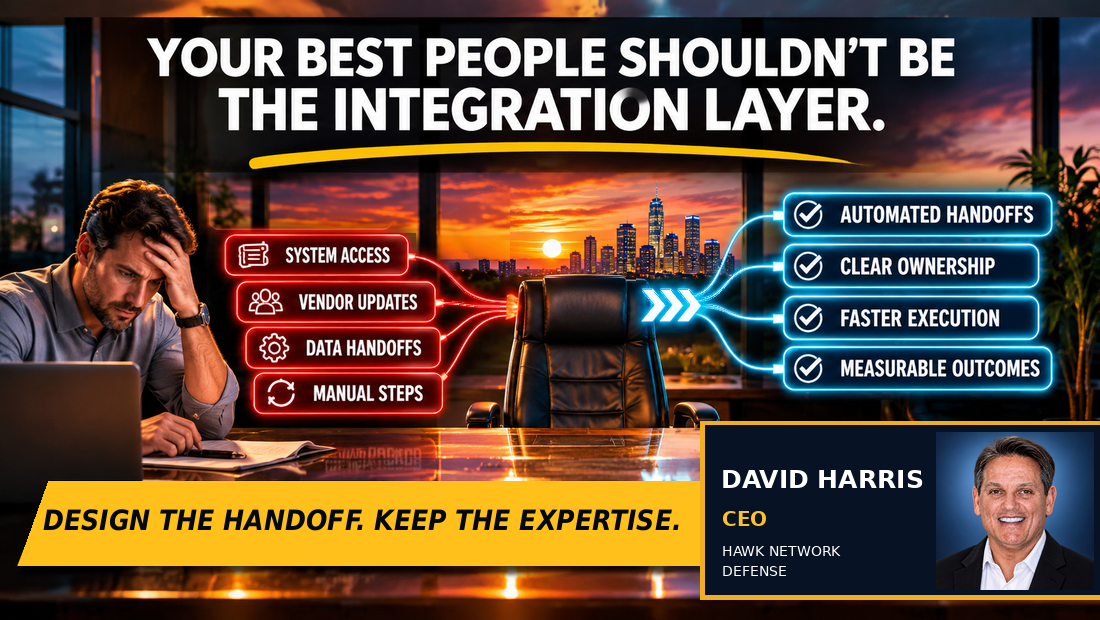
Your Best People Shouldn't Be the Integration Layer
Find where personal intervention repeatedly repairs a routine handoff, then define acceptance and ownership before choosing an integration investment.
Resilience Is Really About Preserving Options
Resilience gives leadership usable choices under pressure. David Harris examines dependencies, decision rights and the investment needed to keep alternatives credible.
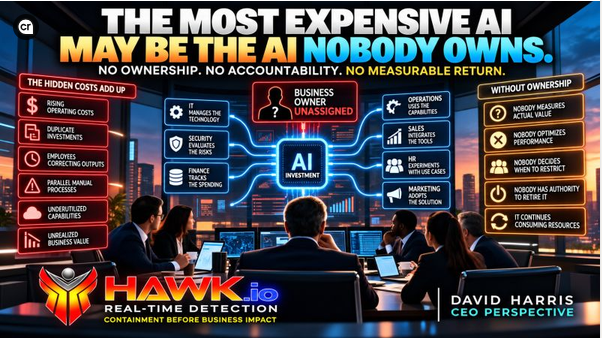
The Most Expensive AI May Be the AI Nobody Owns
The hidden cost of enterprise AI may be unclear ownership after deployment. David Harris outlines five requirements for connecting AI investment to measurable business value, decision authority, and ongoing accountability.

The Board Will Eventually Ask: What Did AI Actually Change?
AI adoption is not the same as business value. David Harris examines what boards should expect from AI investments, including measurable ROI, operating efficiency, decision quality, risk reduction, and executive accountability. The real question isn't how much AI an organization deploys. It's what actually changes because of it.

Attackers Are Moving at Machine Speed. Is Your Security Operation Still Waiting on People?
Cyber threats can move faster than traditional security approval processes. David Harris examines why decision latency, manual handoffs, and unclear response authority can leave organizations exposed—and how AI-driven MDR, governed automation, and executive accountability can improve security outcomes.

The Business Doesn't Experience Your Security Tools Individually. It Experiences the Delay Between Them.
Strong cybersecurity tools do not automatically produce strong security outcomes. David Harris explains why the delays between detection, investigation, authorization, and containment create business exposure—and why executive leadership must focus on decision capacity, coordinated response, and measurable risk reduction.

The Future SOC Is a Decision System
The future Security Operations Center cannot simply be a better monitoring center. David Harris examines why SOC modernization must focus on evidence, decision authority, coordinated response, verified containment, and measurable business outcomes—and what CEOs should expect from a decision-driven security operation.

Cybersecurity ROI Is Measured in Time, Not Tools
More cybersecurity tools do not automatically mean less risk. David Harris examines how CEOs can evaluate security investments through decision latency, containment performance, analyst efficiency, measurable exposure reduction, and financial return—shifting the conversation from technology deployed to business outcomes achieved.

Your Incident Response Plan May Have a Decision Problem
Your security team may detect an attack in seconds, but unclear decision authority can delay containment for hours. David Harris examines why incident response planning must address authorization, escalation, human oversight, bounded automation, and verification—and the five questions CEOs should ask before the next incident.

AI Authority Is Becoming a Business Control
As AI agents move from recommendations to actions, businesses must govern more than access and permissions. David Harris explains why delegated authority is becoming an enterprise control, how bounded autonomy should work, and what CEOs must require for enforcement, accountability, revocation, and business-risk oversight.