

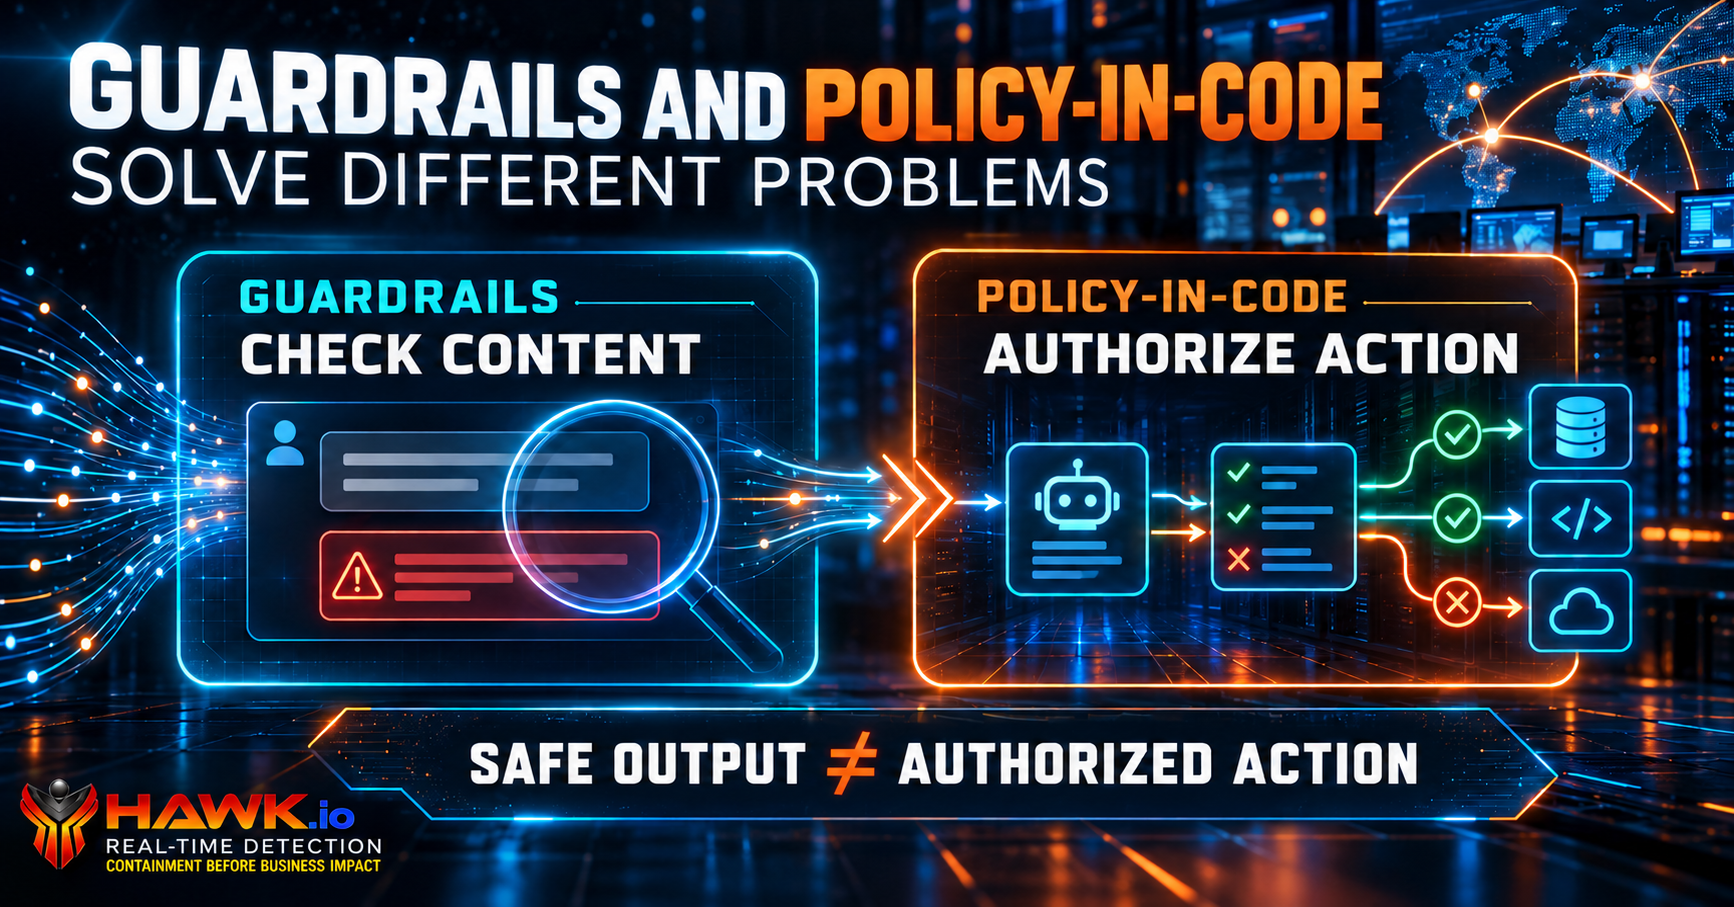
Guardrails and Policy-in-Code Solve Different Problems
AI guardrails and policy-in-code protect different security boundaries. HAWK Network Defense explains how prompt-injection defenses, evidence validation, runtime authorization, and enforceable policies work together to secure agentic AI operations.

Your AI Agent Should Have to Earn More Authority
AI agents should not receive unrestricted authority simply because they can perform an action. Tim Shelton explores progressive autonomy, evidence-based authorization, runtime enforcement, continuous evaluation, and why agent permissions must be capable of expanding—or contracting—as operational conditions change.