

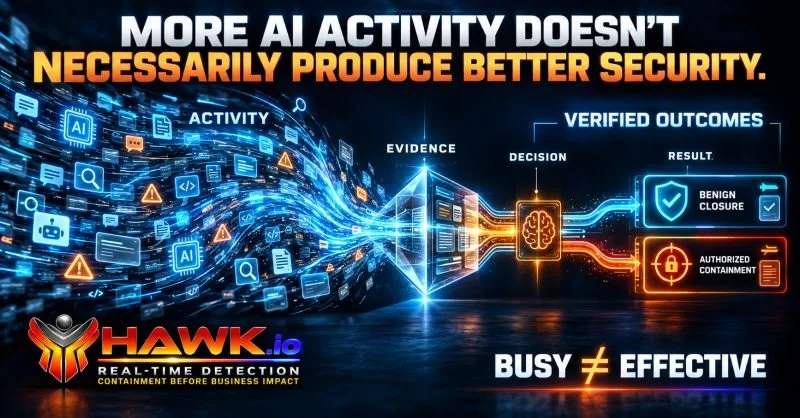
More AI Activity Doesn’t Necessarily Produce Better Security
More AI-generated alerts, investigations, and summaries do not automatically improve cybersecurity. HAWK Network Defense explains how validated findings, decision quality, analyst rework, response timeliness, and verified outcomes reveal whether AI is improving security operations.

What Happens Between Detection and Containment?
Detecting a threat is only the beginning. The time between detection, investigation, authorization, containment, and verification determines how long an organization remains exposed. Explore five questions security leaders should ask about the complete MDR response process.

What Should an AI Security Outcome Actually Cost?
The true cost of AI security goes beyond model tokens and API calls. HAWK Network Defense examines how analyst validation, investigation time, rework, decision quality, and business consequences determine the real cost of a security outcome.

AI-Driven MDR: From Threat Detection to Validated Containment
AI-driven MDR should do more than detect threats. Discover how validated evidence, autonomous investigation, and authorized containment help security teams move from alerts to measurable outcomes.

Attackers Are Moving at Machine Speed. Is Your Security Operation Still Waiting on People?
Cyber threats can move faster than traditional security approval processes. David Harris examines why decision latency, manual handoffs, and unclear response authority can leave organizations exposed—and how AI-driven MDR, governed automation, and executive accountability can improve security outcomes.

Detection Coverage is not Detection Effectiveness
Connected security tools do not automatically deliver effective threat detection. HAWK Network Defense explains the difference between detection coverage and detection effectiveness, including telemetry quality, cross-system correlation, scenario-based testing, and the ability to produce timely, actionable security findings.

Can Your Security Stack Actually Execute the Decision?
Detecting a cyber threat is only the beginning. HAWK Network Defense examines the operational gap between security decisions and response execution, including evidence gathering, authorization, automated containment, and verification. Learn five questions security leaders can use to evaluate whether their existing security stack can act when it matters.