

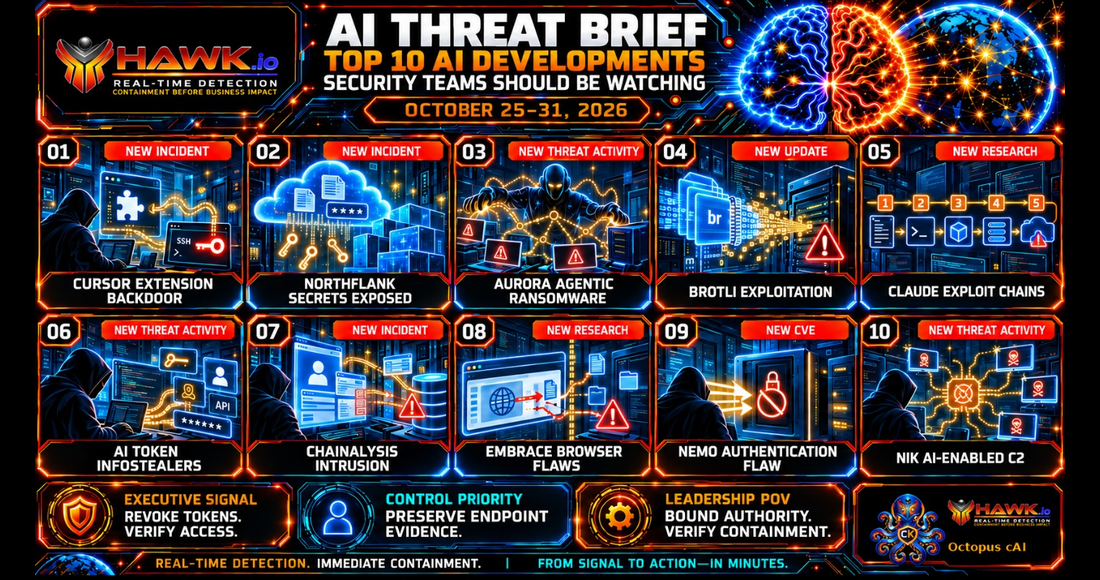
HAWK AI Threat Brief: Top 10 AI Developments Security Teams Should Be Watching
HAWK's AI Threat Brief covers 10 key security developments from October 25–31, 2026, including malicious extensions, stolen AI credentials and agentic attacks.

What Happens Between Detection and Containment?
Detecting a threat is only the beginning. The time between detection, investigation, authorization, containment, and verification determines how long an organization remains exposed. Explore five questions security leaders should ask about the complete MDR response process.
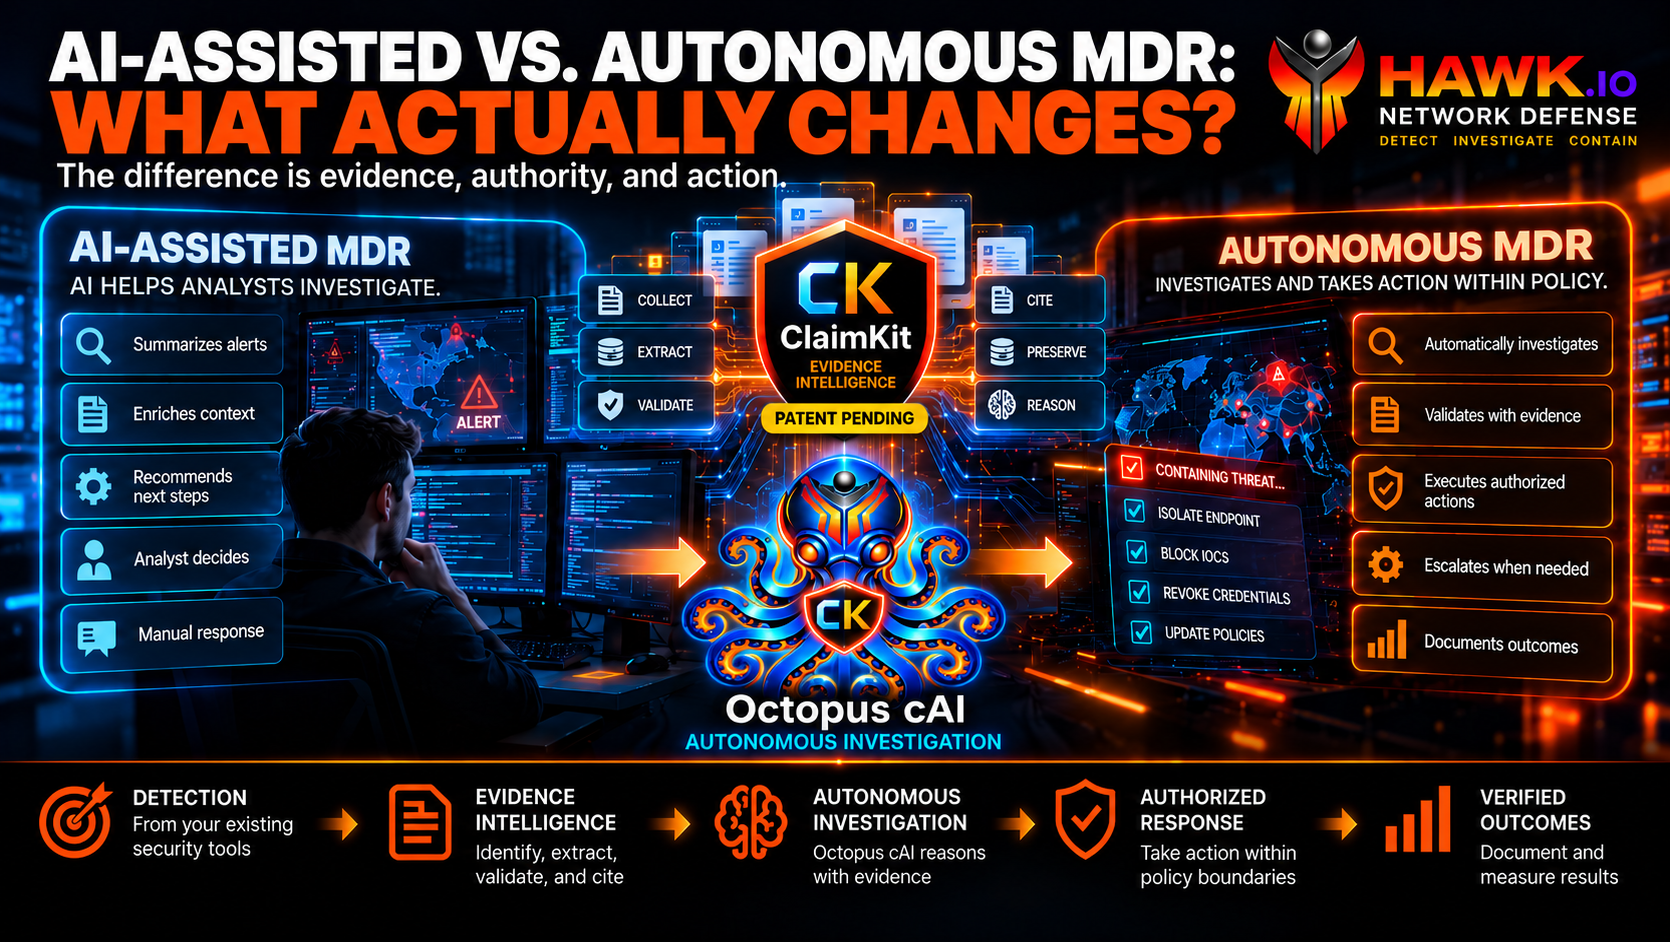
AI-Assisted vs. Autonomous MDR: What Actually Changes?
AI-assisted and autonomous MDR are not the same. One helps analysts investigate threats; the other can execute defined investigations and authorized response actions. Explore how evidence intelligence, autonomy, human oversight, and policy-governed authority change managed detection and response.

The Business Doesn't Experience Your Security Tools Individually. It Experiences the Delay Between Them.
Strong cybersecurity tools do not automatically produce strong security outcomes. David Harris explains why the delays between detection, investigation, authorization, and containment create business exposure—and why executive leadership must focus on decision capacity, coordinated response, and measurable risk reduction.

Containment at Machine Speed
Fast threat detection means little when containment takes hours. Tim Shelton examines three levels of security automation, how to establish response authority, why containment must be verified, and how AI-driven security operations can reduce decision latency without sacrificing human control.

When the Security Stack Sees the Attach but Can’t Stop it
The October 8, 2026, advisory on China-linked intrusion activity demonstrates how attackers exploit gaps between security technologies. HAWK examines why detecting reconnaissance, compromised identities, and persistent access is not enough—and why coordinated investigations, authorized response, and verified containment matter.

Detection Coverage is not Detection Effectiveness
Connected security tools do not automatically deliver effective threat detection. HAWK Network Defense explains the difference between detection coverage and detection effectiveness, including telemetry quality, cross-system correlation, scenario-based testing, and the ability to produce timely, actionable security findings.

Can Your Security Stack Actually Execute the Decision?
Detecting a cyber threat is only the beginning. HAWK Network Defense examines the operational gap between security decisions and response execution, including evidence gathering, authorization, automated containment, and verification. Learn five questions security leaders can use to evaluate whether their existing security stack can act when it matters.

Your EDR Sees the Endpoint. The Attack Sees the Environment.
EDR is essential, but modern cyberattacks extend beyond individual endpoints. HAWK Network Defense examines why security teams need broader identity, network, cloud, and business context to investigate threats effectively—and how coordinated security operations and AI-driven MDR can extend existing EDR investments without requiring wholesale replacement.

Security Visibility vs. Decision Context: Why More Data Isn't Enough
More security data does not automatically lead to better security decisions. HAWK Network Defense examines the difference between visibility and decision context, including validated evidence, business criticality, decision latency, authorized response, and verified containment.

The Future SOC Is a Decision System
The future Security Operations Center cannot simply be a better monitoring center. David Harris examines why SOC modernization must focus on evidence, decision authority, coordinated response, verified containment, and measurable business outcomes—and what CEOs should expect from a decision-driven security operation.

Cybersecurity ROI Is Measured in Time, Not Tools
More cybersecurity tools do not automatically mean less risk. David Harris examines how CEOs can evaluate security investments through decision latency, containment performance, analyst efficiency, measurable exposure reduction, and financial return—shifting the conversation from technology deployed to business outcomes achieved.

The Future SOC Will Be Built Around Evidence, Not Alerts
The future Security Operations Center will not be defined by alert volume. Tim Shelton examines how evidence-driven investigations, AI-assisted correlation, contextual analysis, and policy-governed automation can help security teams make defensible decisions faster and verify that their responses worked.

Your Incident Response Plan May Have a Decision Problem
Your security team may detect an attack in seconds, but unclear decision authority can delay containment for hours. David Harris examines why incident response planning must address authorization, escalation, human oversight, bounded automation, and verification—and the five questions CEOs should ask before the next incident.

More AI Will Not Fix a Poorly Designed SOC
Adding AI does not automatically fix fragmented security operations. Tim Shelton examines how disconnected tools, unreliable context, unclear response authority, and inefficient workflows can limit the value of SOC automation—and why organizations must redesign their decision processes before scaling AI.

What Exploit Research Taught Me About AI Agent Security
Exploit research teaches security professionals to examine what systems can actually do—not merely what designers intended. Tim Shelton applies that principle to AI agent architecture, exploring combined permissions, runtime enforcement, human-controlled autonomy, progressive authority, and the need to verify operational outcomes.

Incident Response Metrics: Measure Time to Verified Outcome
Alert counts and response times don't tell executives whether a cyber threat was actually contained. David Harris examines the incident response lifecycle, including evidence gathering, decision latency, authorized action, and time to verified containment—and explains what CEOs should measure after a significant security incident.