

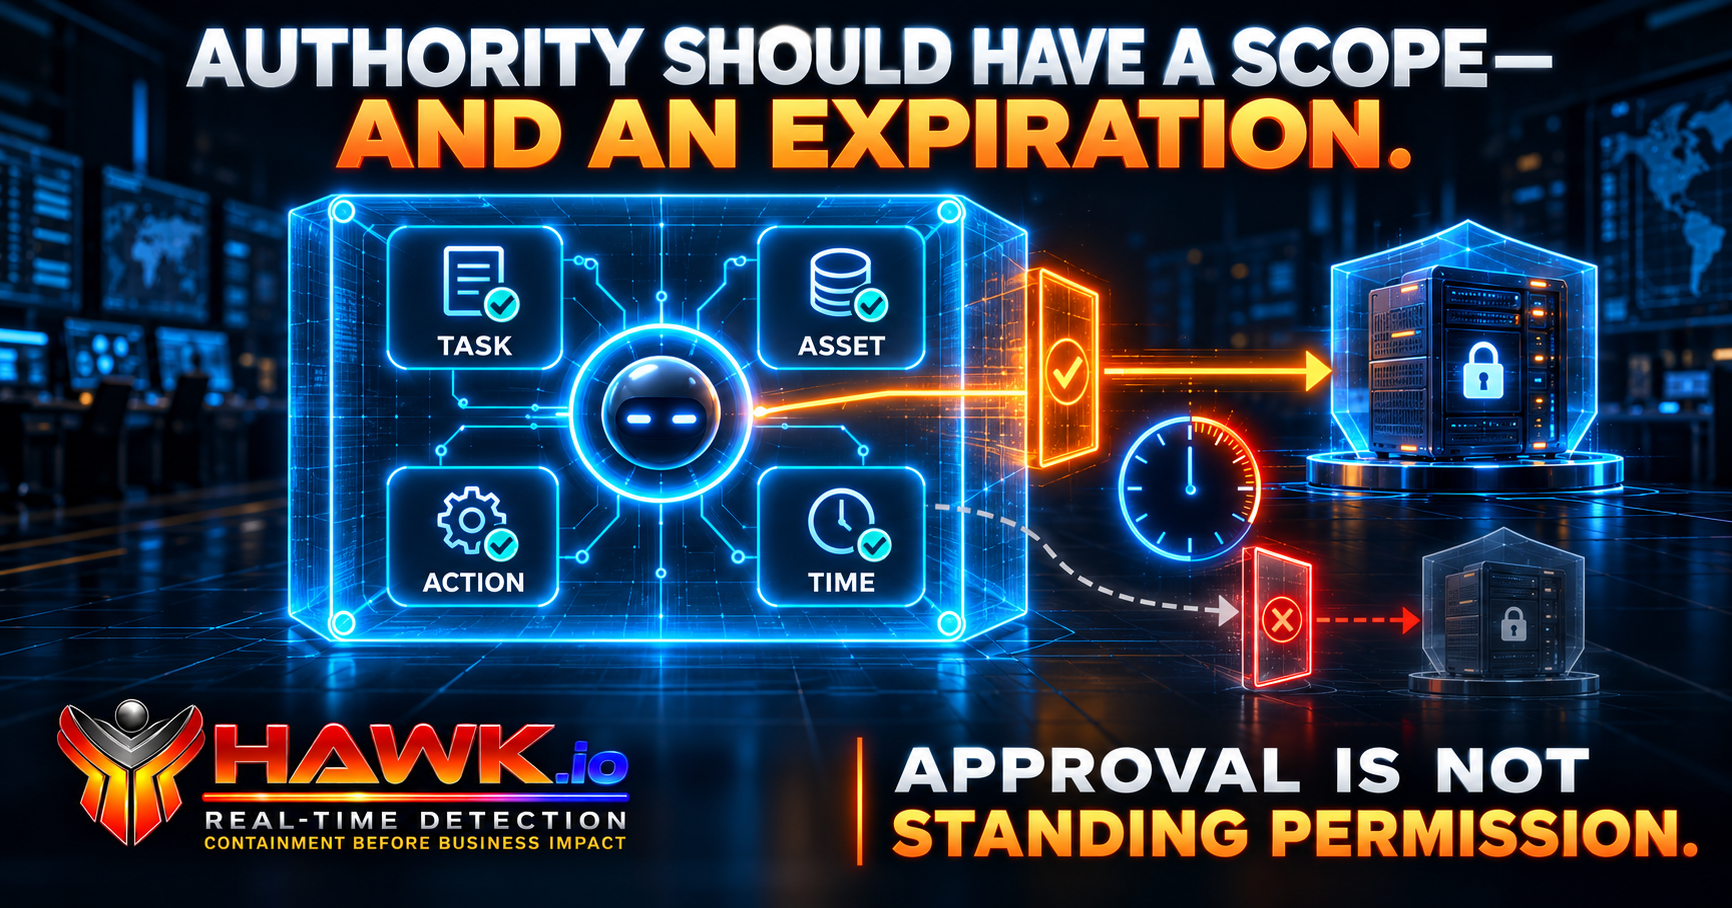
Authority Should Have a Scope—and an Expiration.
AI agent approval should never become unlimited authority. HAWK Network Defense examines five essential authorization controls—purpose, scope, actions, conditions, and duration—and explains why permissions must be enforced at execution time. Learn why expiring an agent's authority and reversing an existing containment action are separate security decisions.

The AI Insider May Not Be Human
The next insider threat may not be human. AI agents can use legitimate credentials and approved tools while taking actions outside their intended authority. HAWK Network Defense examines non-human identity security, least-privilege permissions, enforceable authorization, continuous governance, and why a valid identity does not guarantee a valid action.

The Most Dangerous AI Permission Is the One Nobody Remembers Granting
AI agents rarely begin with unlimited authority. Their effective permissions expand as integrations, credentials, APIs, and delegated workflows change. Tim Shelton examines permission drift, cumulative capabilities, temporary access, continuous authorization reviews, and why runtime enforcement must reflect what an agent can actually do—not merely what was approved at deployment.