

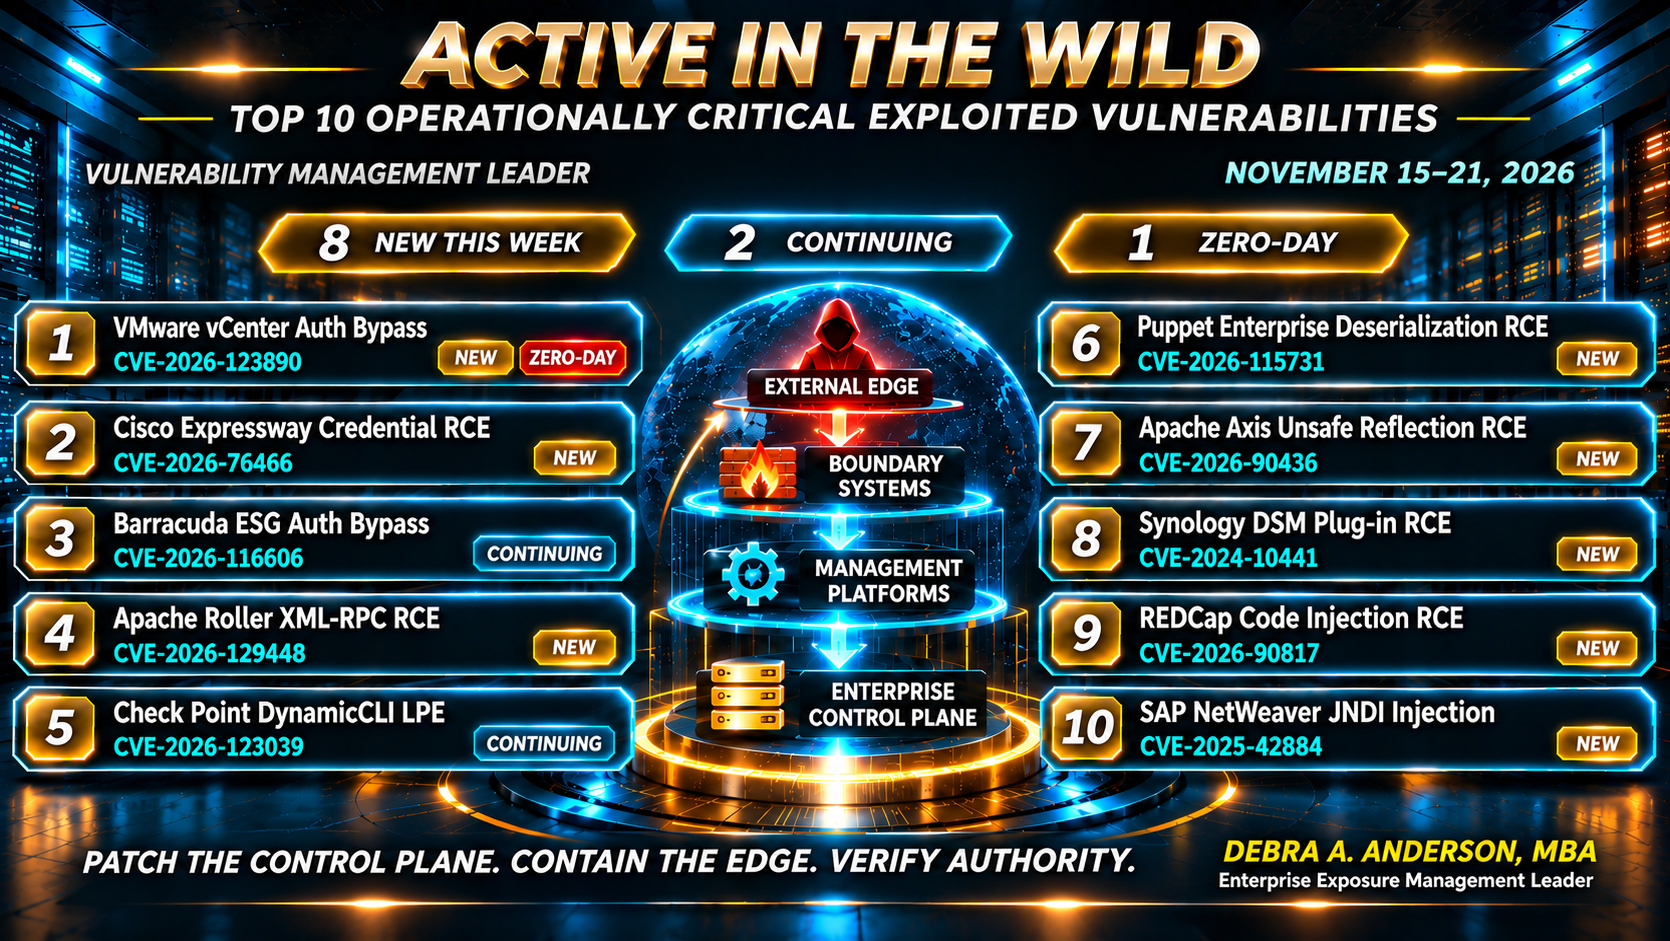
Active in the Wild: The 10 Exploited Vulnerabilities That Matter Most | Nov. 15–21, 2026
VMware vCenter exploitation before patch release leads this week’s operational risk ranking. Debra A. Anderson examines ten active attack paths across virtualization, edge infrastructure, automation, legacy middleware, storage and enterprise applications—and the verification leaders should require after remediation.

Attackers Are Moving at Machine Speed. Is Your Security Operation Still Waiting on People?
Cyber threats can move faster than traditional security approval processes. David Harris examines why decision latency, manual handoffs, and unclear response authority can leave organizations exposed—and how AI-driven MDR, governed automation, and executive accountability can improve security outcomes.

The Business Doesn't Experience Your Security Tools Individually. It Experiences the Delay Between Them.
Strong cybersecurity tools do not automatically produce strong security outcomes. David Harris explains why the delays between detection, investigation, authorization, and containment create business exposure—and why executive leadership must focus on decision capacity, coordinated response, and measurable risk reduction.