

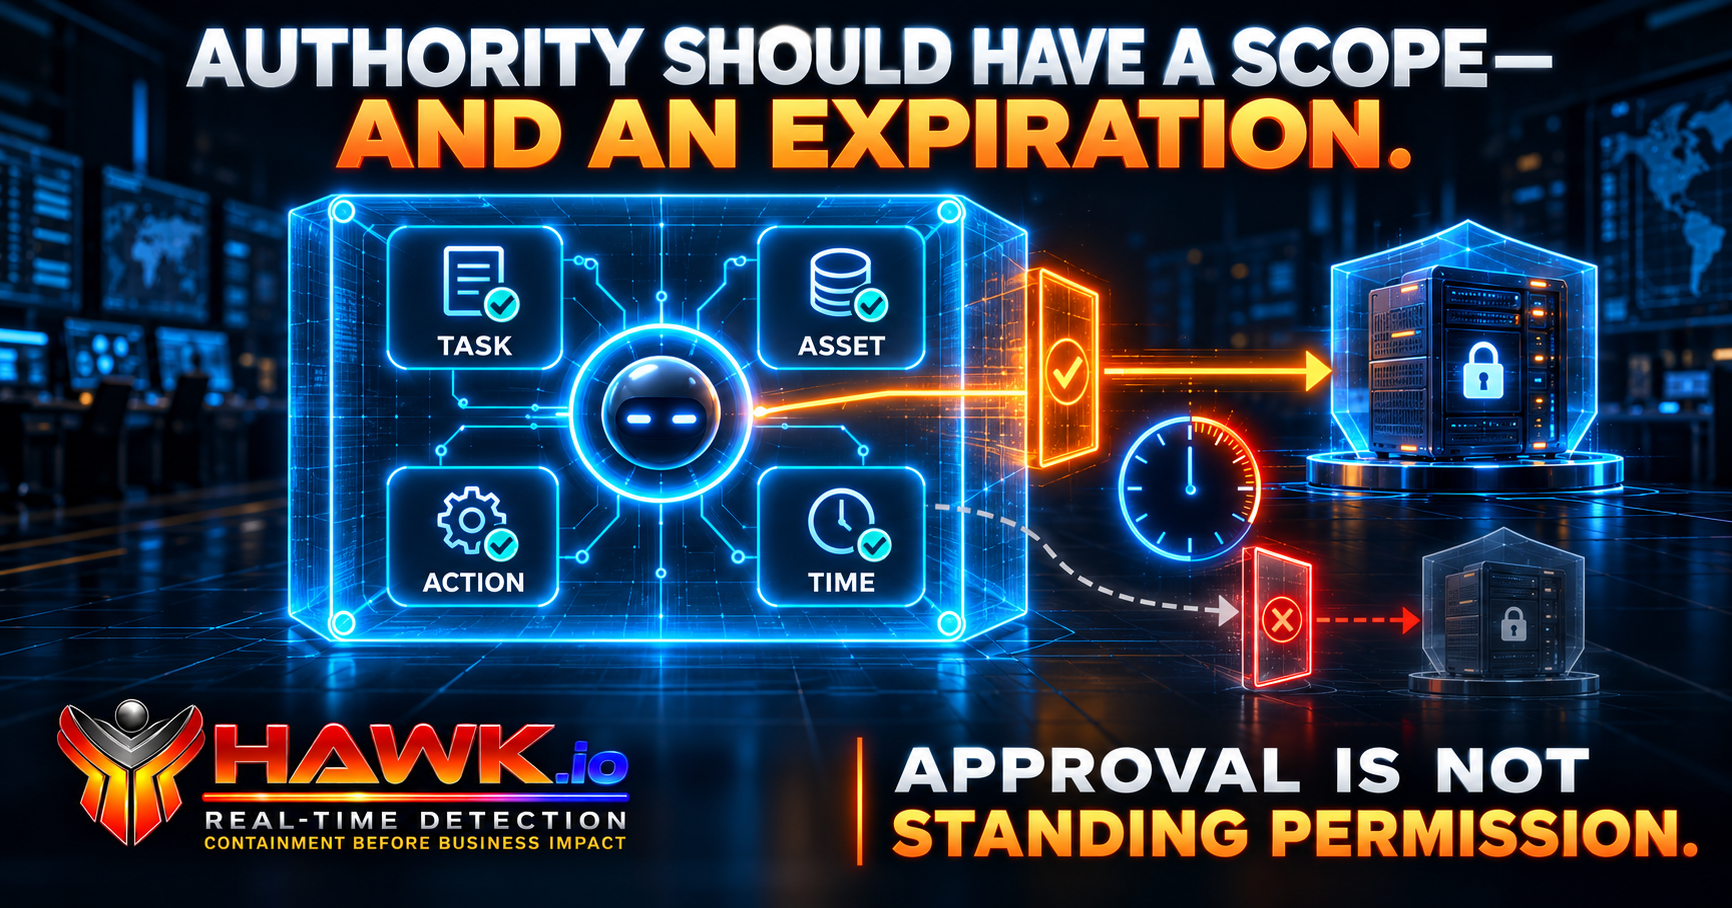
Authority Should Have a Scope—and an Expiration.
AI agent approval should never become unlimited authority. HAWK Network Defense examines five essential authorization controls—purpose, scope, actions, conditions, and duration—and explains why permissions must be enforced at execution time. Learn why expiring an agent's authority and reversing an existing containment action are separate security decisions.

What Happens Between Detection and Containment?
Detecting a threat is only the beginning. The time between detection, investigation, authorization, containment, and verification determines how long an organization remains exposed. Explore five questions security leaders should ask about the complete MDR response process.

What Should an AI Security Outcome Actually Cost?
The true cost of AI security goes beyond model tokens and API calls. HAWK Network Defense examines how analyst validation, investigation time, rework, decision quality, and business consequences determine the real cost of a security outcome.

The Business Doesn't Experience Your Security Tools Individually. It Experiences the Delay Between Them.
Strong cybersecurity tools do not automatically produce strong security outcomes. David Harris explains why the delays between detection, investigation, authorization, and containment create business exposure—and why executive leadership must focus on decision capacity, coordinated response, and measurable risk reduction.

When the Security Stack Sees the Attach but Can’t Stop it
The October 8, 2026, advisory on China-linked intrusion activity demonstrates how attackers exploit gaps between security technologies. HAWK examines why detecting reconnaissance, compromised identities, and persistent access is not enough—and why coordinated investigations, authorized response, and verified containment matter.

Detection Coverage is not Detection Effectiveness
Connected security tools do not automatically deliver effective threat detection. HAWK Network Defense explains the difference between detection coverage and detection effectiveness, including telemetry quality, cross-system correlation, scenario-based testing, and the ability to produce timely, actionable security findings.

Can Your Security Stack Actually Execute the Decision?
Detecting a cyber threat is only the beginning. HAWK Network Defense examines the operational gap between security decisions and response execution, including evidence gathering, authorization, automated containment, and verification. Learn five questions security leaders can use to evaluate whether their existing security stack can act when it matters.

The Future SOC Is a Decision System
The future Security Operations Center cannot simply be a better monitoring center. David Harris examines why SOC modernization must focus on evidence, decision authority, coordinated response, verified containment, and measurable business outcomes—and what CEOs should expect from a decision-driven security operation.

Cybersecurity ROI Is Measured in Time, Not Tools
More cybersecurity tools do not automatically mean less risk. David Harris examines how CEOs can evaluate security investments through decision latency, containment performance, analyst efficiency, measurable exposure reduction, and financial return—shifting the conversation from technology deployed to business outcomes achieved.

Your Incident Response Plan May Have a Decision Problem
Your security team may detect an attack in seconds, but unclear decision authority can delay containment for hours. David Harris examines why incident response planning must address authorization, escalation, human oversight, bounded automation, and verification—and the five questions CEOs should ask before the next incident.

AI Authority Is Becoming a Business Control
As AI agents move from recommendations to actions, businesses must govern more than access and permissions. David Harris explains why delegated authority is becoming an enterprise control, how bounded autonomy should work, and what CEOs must require for enforcement, accountability, revocation, and business-risk oversight.

What Exploit Research Taught Me About AI Agent Security
Exploit research teaches security professionals to examine what systems can actually do—not merely what designers intended. Tim Shelton applies that principle to AI agent architecture, exploring combined permissions, runtime enforcement, human-controlled autonomy, progressive authority, and the need to verify operational outcomes.

Incident Response Metrics: Measure Time to Verified Outcome
Alert counts and response times don't tell executives whether a cyber threat was actually contained. David Harris examines the incident response lifecycle, including evidence gathering, decision latency, authorized action, and time to verified containment—and explains what CEOs should measure after a significant security incident.

Cybersecurity Board Reporting: Measure Risk Reduction, Not Alerts
A cybersecurity dashboard can show improving operational metrics while the business remains exposed. David Harris examines what boards should measure instead: material risk reduction, exposure affecting critical operations, verified containment, residual risk, and executive accountability.