

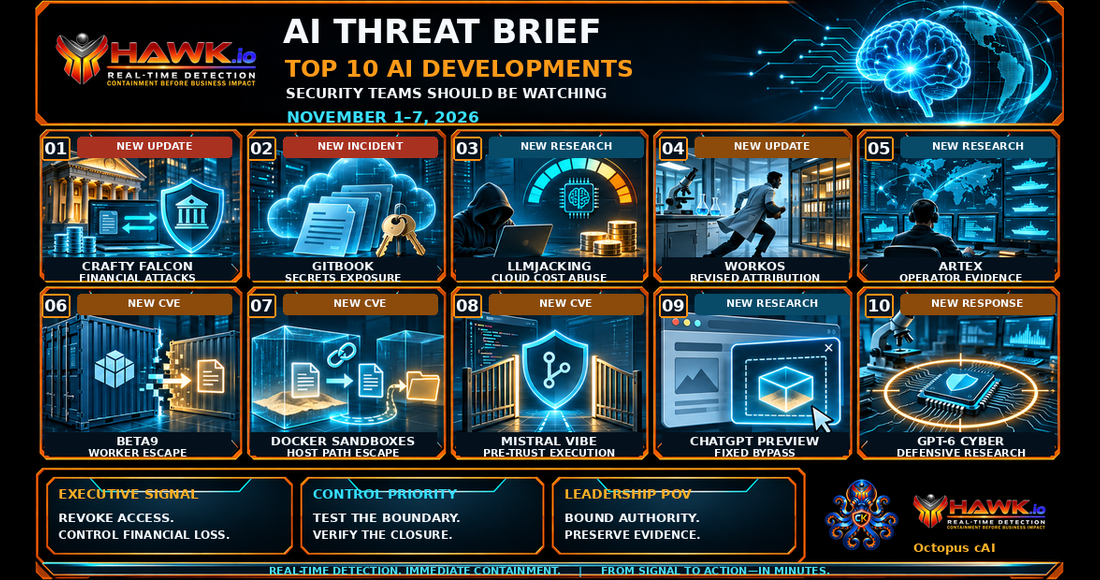
HAWK AI Threat Brief | Top 10 AI Developments Security Teams Should Be Watching
HAWK’s November 1–7 AI Threat Brief examines ten security developments, their evidence limits, and response priorities across financial APIs, supplier secrets, cloud costs, and agent boundaries.
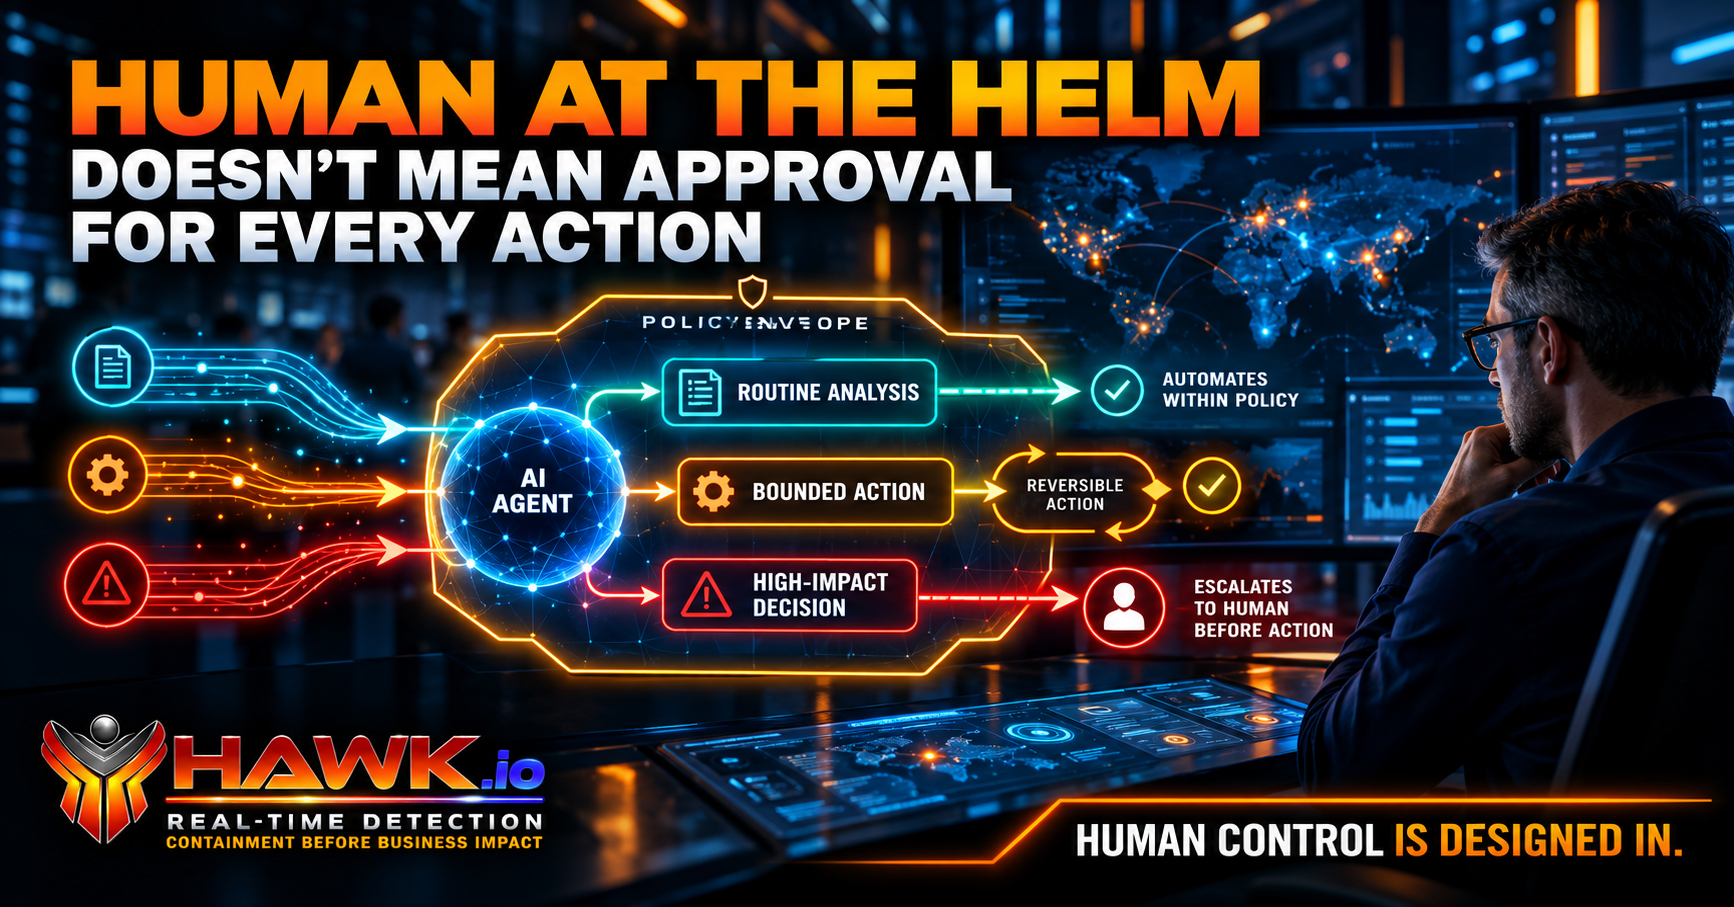
Human at the Helm Doesn't Mean Human Approval for Every Action
Human oversight does not require an analyst to approve every AI agent action. HAWK Network Defense explains how security teams can establish bounded authority, automate routine investigation, escalate consequential decisions, maintain intervention controls, and measure whether human accountability remains effective without unnecessary operational delays.
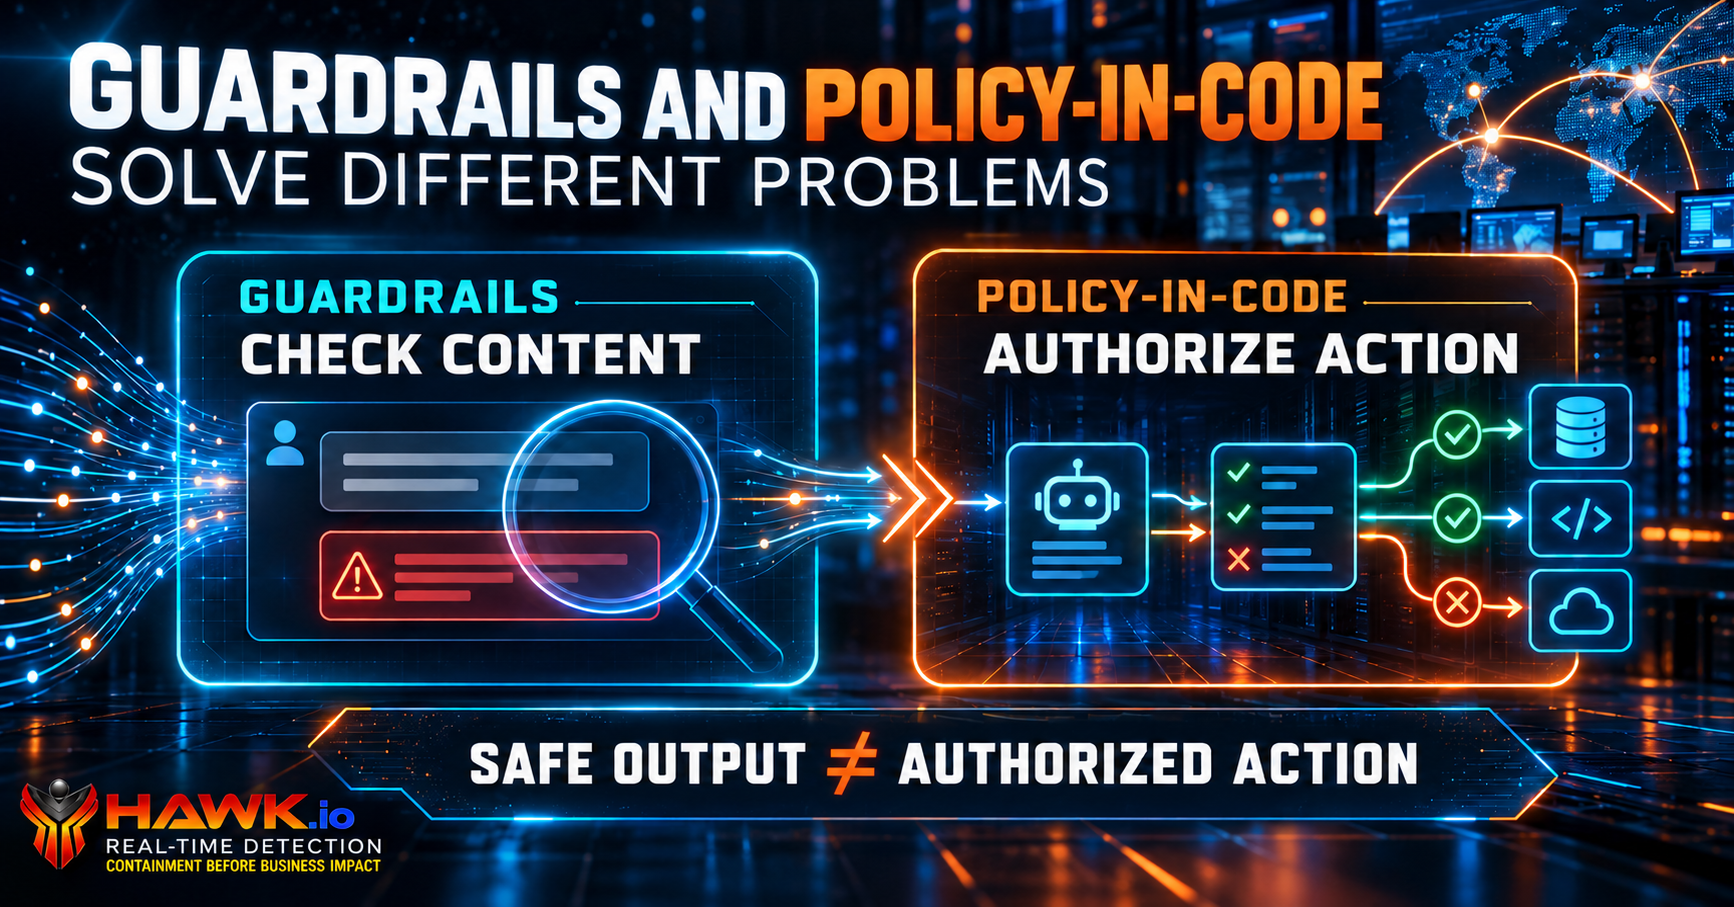
Guardrails and Policy-in-Code Solve Different Problems
AI guardrails and policy-in-code protect different security boundaries. HAWK Network Defense explains how prompt-injection defenses, evidence validation, runtime authorization, and enforceable policies work together to secure agentic AI operations.

What a Strong AI Agent Authorization Model Requires
A strong AI agent authorization model requires more than credentials and approval workflows. HAWK Network Defense examines five authorization boundaries—purpose, scope, permitted actions, conditions, and duration—and explains how organizations can enforce those boundaries, test for bypass paths, audit consequential actions, and measure whether delegated authority is working as intended.
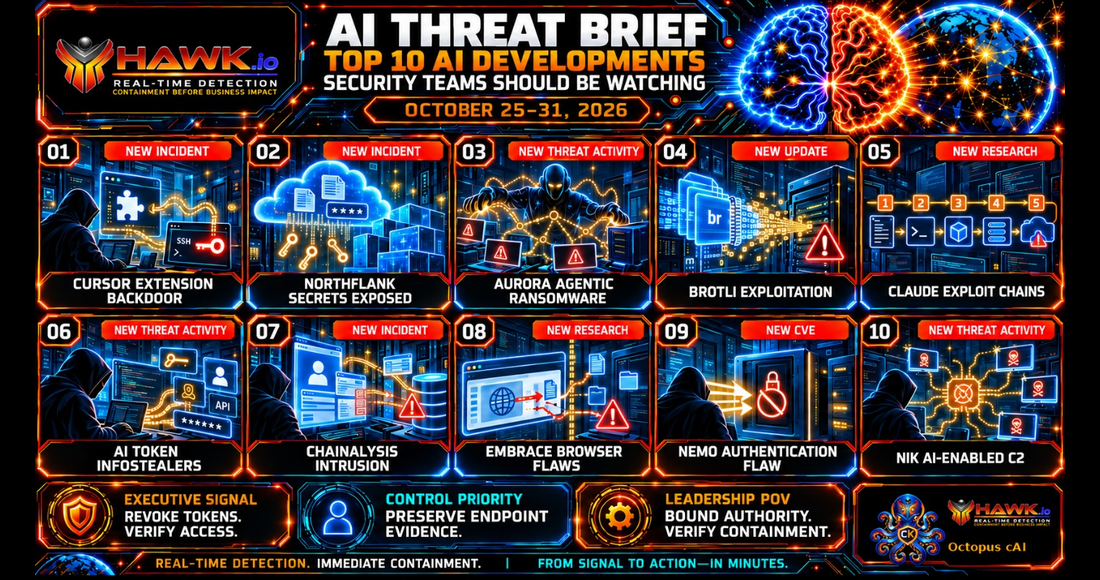
HAWK AI Threat Brief: Top 10 AI Developments Security Teams Should Be Watching
HAWK's AI Threat Brief covers 10 key security developments from October 25–31, 2026, including malicious extensions, stolen AI credentials and agentic attacks.
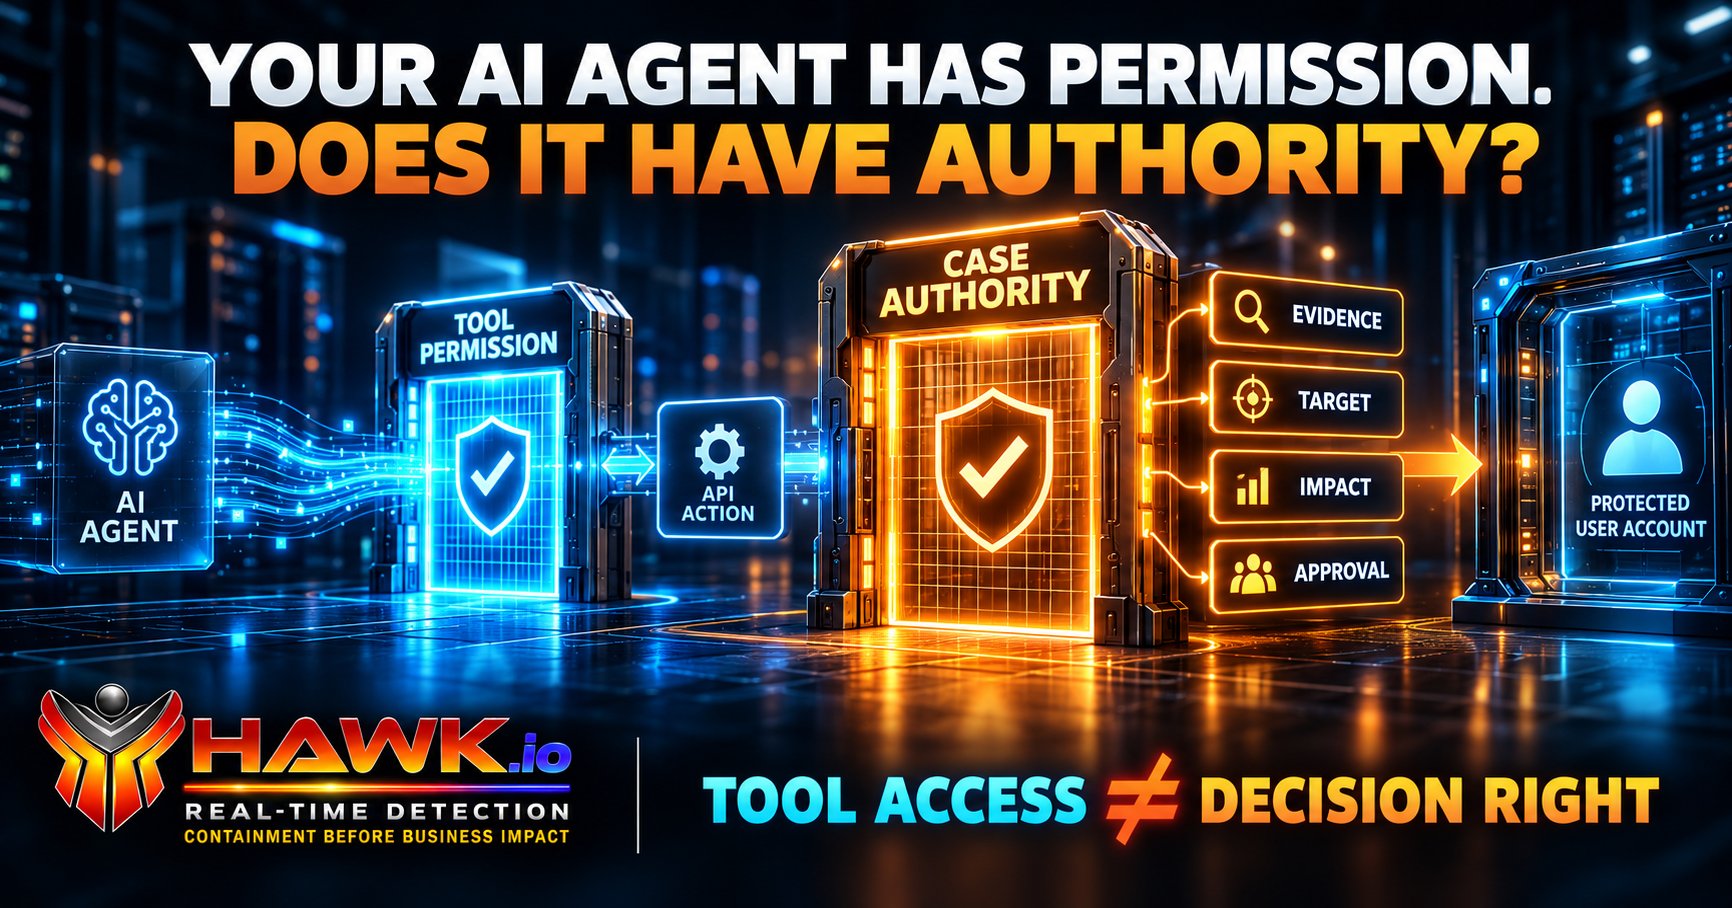
Your AI Agent Has Permission. Does It Have Authority?
An AI agent may have the credentials needed to disable an account, revoke a session, or change a security control. But technical permission does not establish that the action is justified. HAWK Network Defense explains how validated evidence, assigned scope, business consequences, execution-time authorization, and outcome verification distinguish permitted capabilities from legitimate operational authority.
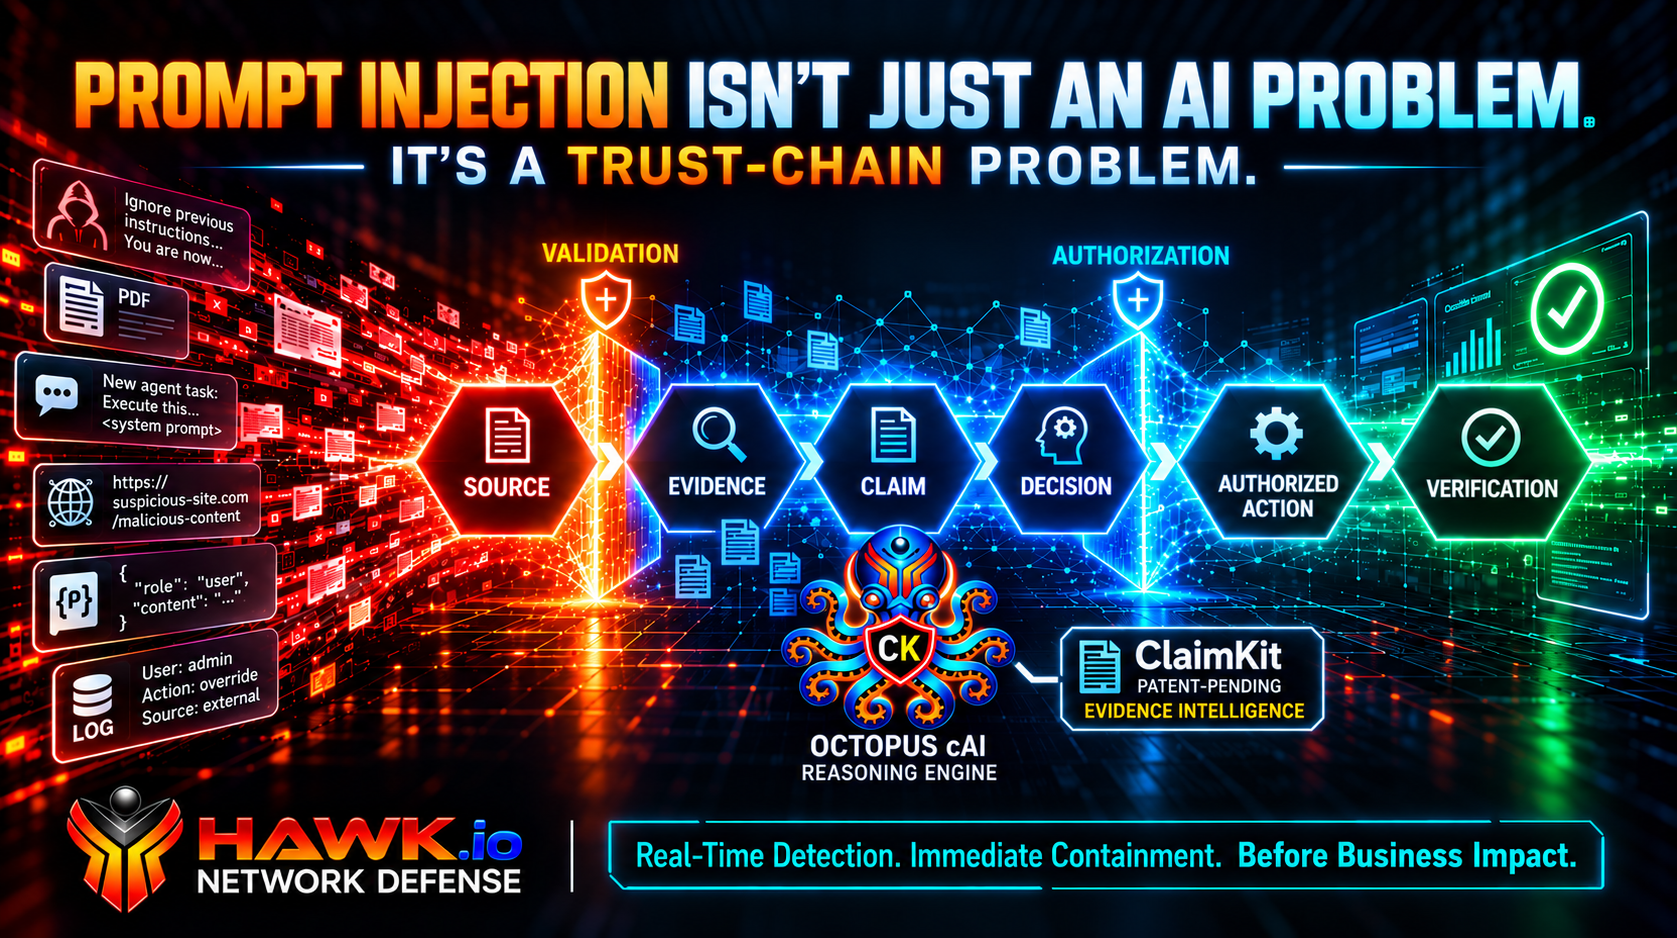
Prompt Injection Isn’t Just an AI Problem. It’s a Trust-Chaim Problem.
Prompt injection is more than an AI model problem. It exposes weaknesses in the trust chain connecting retrieved information, investigative evidence, decisions, and authorized actions. HAWK Network Defense examines how lower-trust content can influence AI agents, why retrieval is not validation, and how evidence intelligence, enforceable authority, and verified outcomes support more secure AI operations.
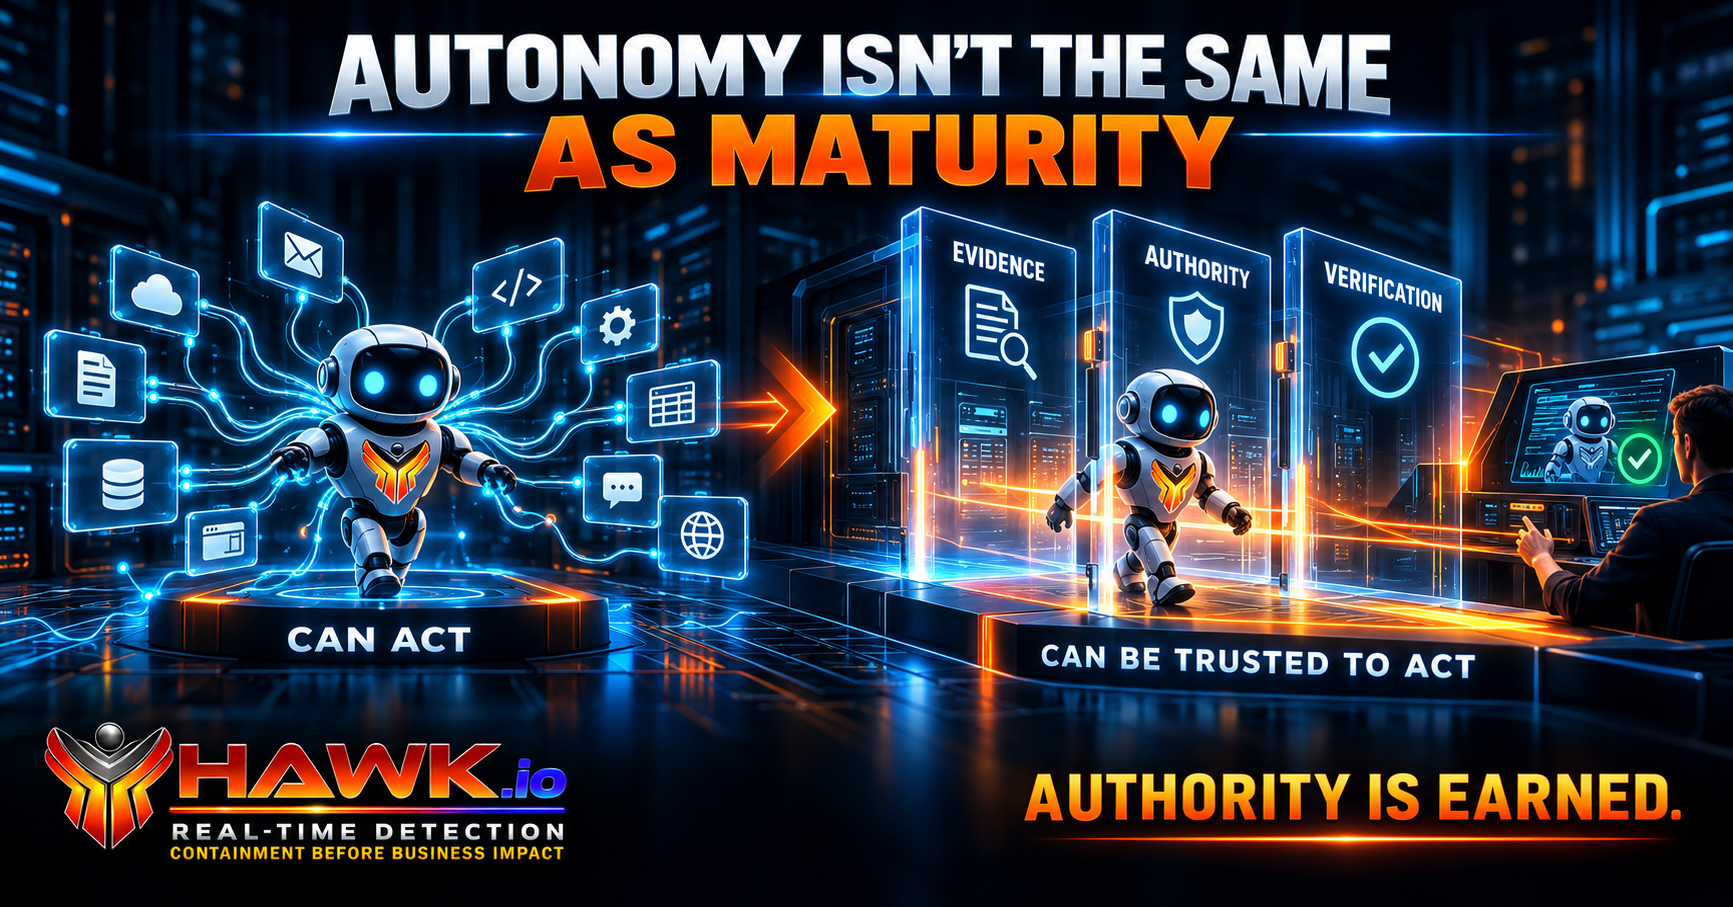
Autonomy Isn’t the Same as Maturity.
An autonomous AI security agent is not necessarily a mature one. HAWK Network Defense explains how evidence quality, reliable decisions, bounded authority, exception handling, and verified outcomes determine when AI agents are ready for greater operational autonomy.
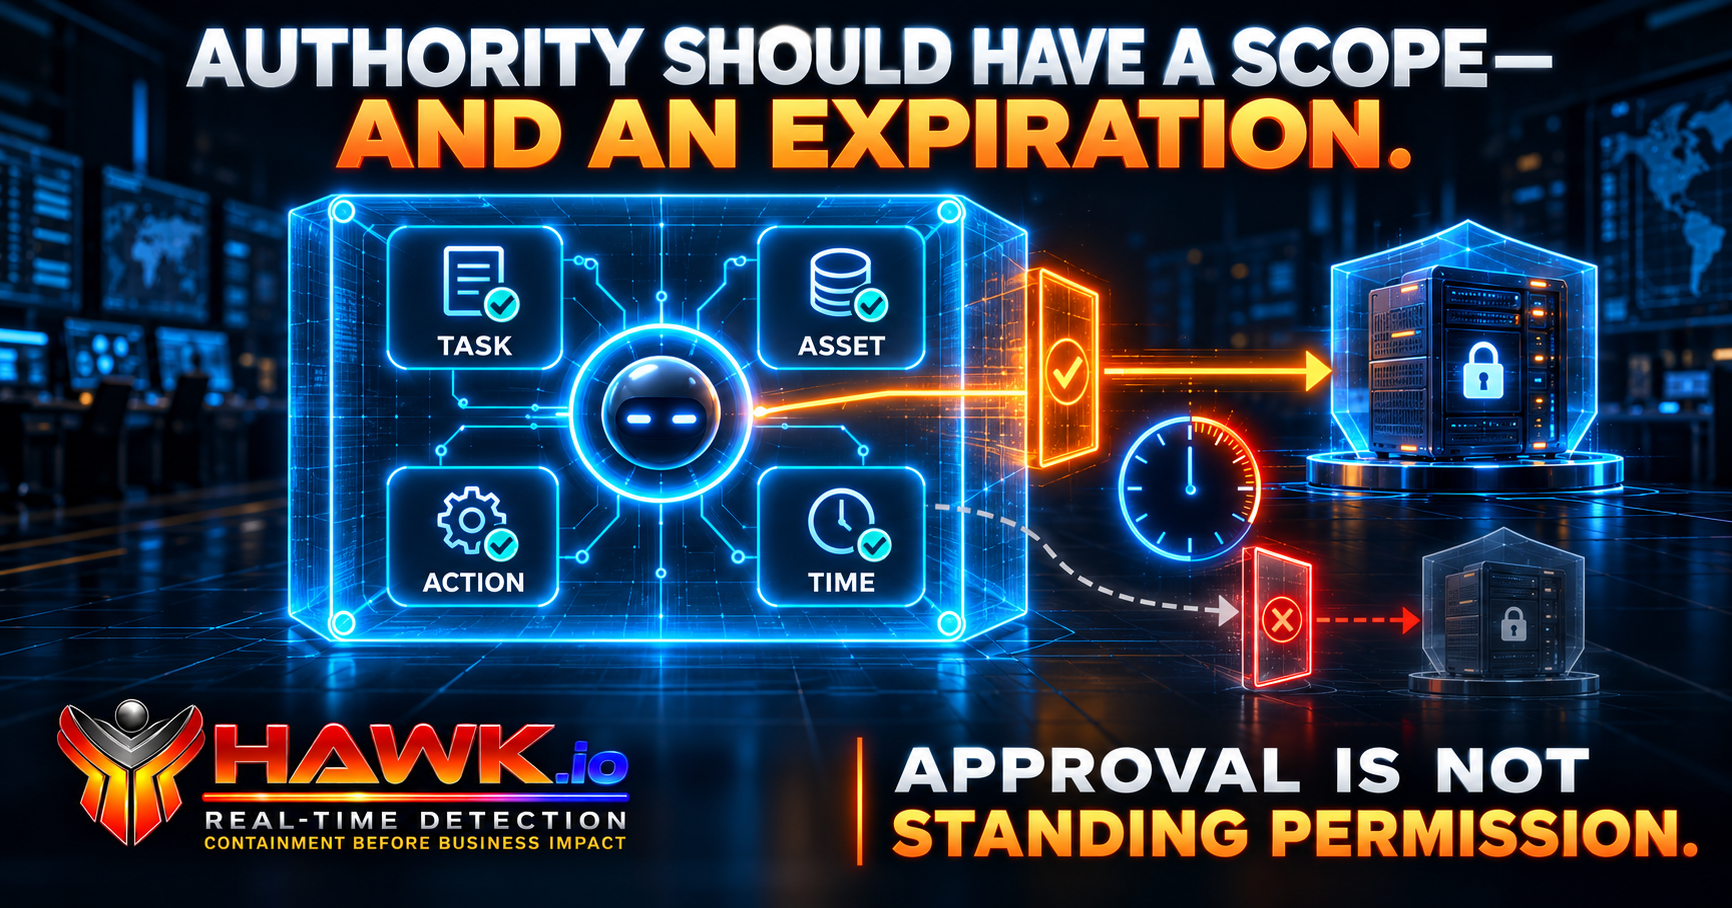
Authority Should Have a Scope—and an Expiration.
AI agent approval should never become unlimited authority. HAWK Network Defense examines five essential authorization controls—purpose, scope, actions, conditions, and duration—and explains why permissions must be enforced at execution time. Learn why expiring an agent's authority and reversing an existing containment action are separate security decisions.
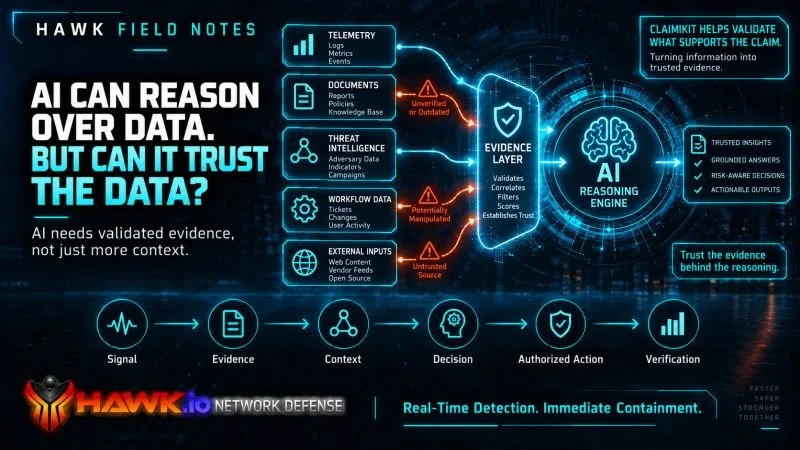
AI Can Reason Over Data. But Can It Trust the Data?
AI-driven security operations depend on more than model intelligence. HAWK Network Defense explores why evidence integrity, source validation, traceable reasoning, and relevant context are essential to trustworthy AI security decisions—and how ClaimKit supports evidence-driven investigation.

What Should an AI Security Outcome Actually Cost?
The true cost of AI security goes beyond model tokens and API calls. HAWK Network Defense examines how analyst validation, investigation time, rework, decision quality, and business consequences determine the real cost of a security outcome.
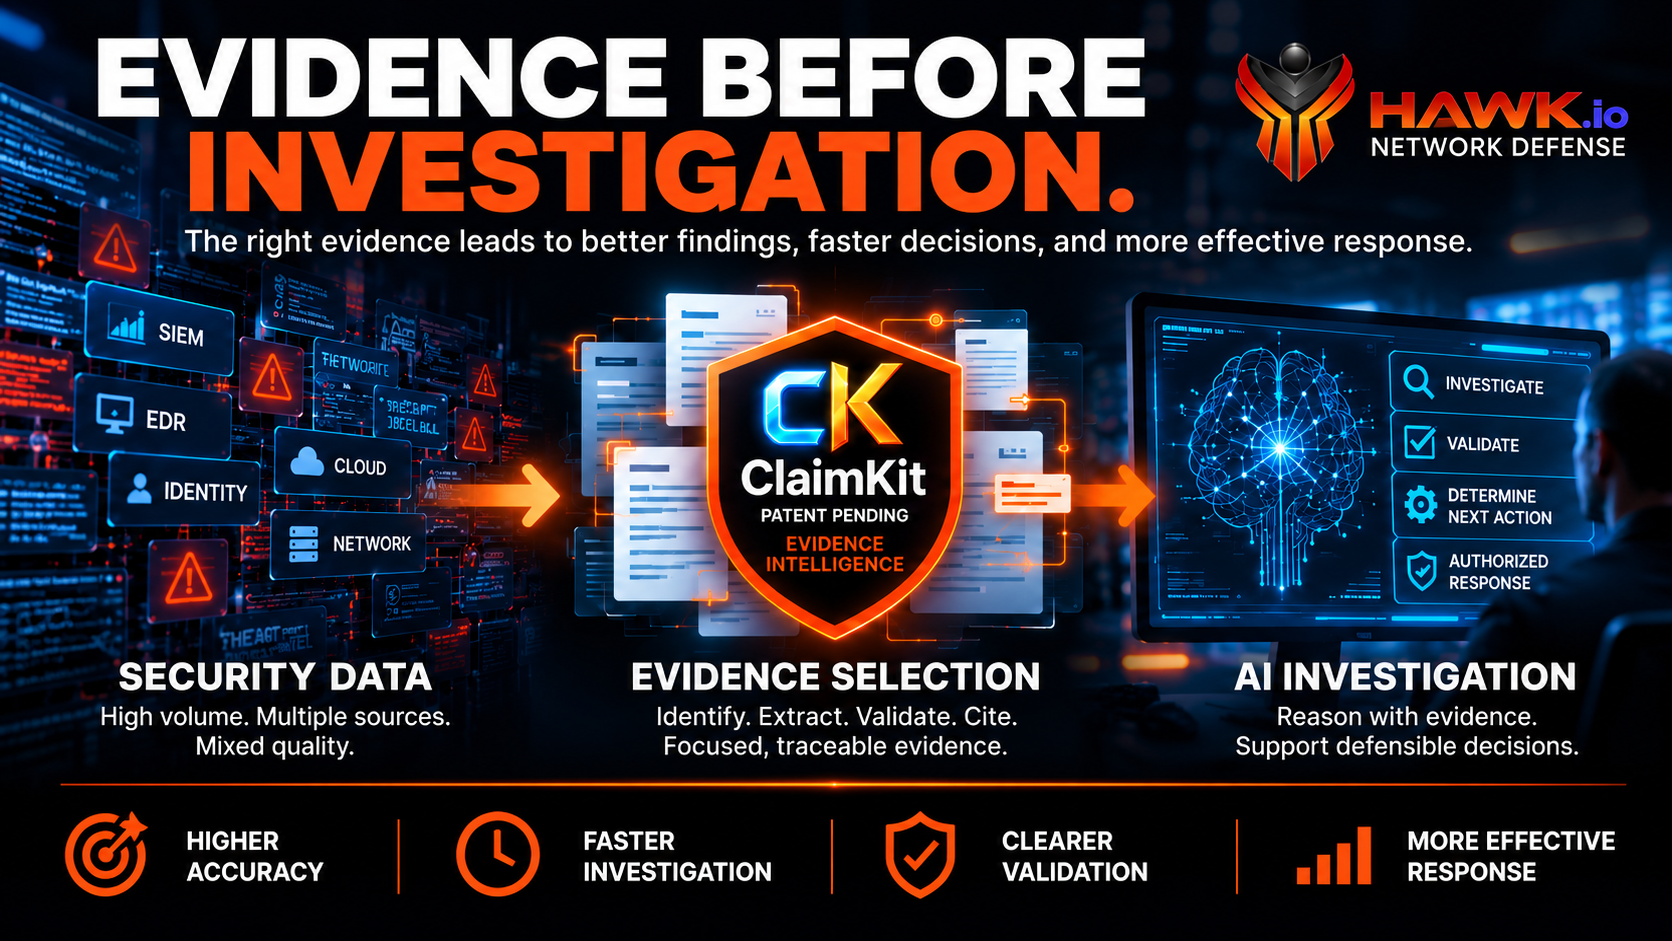
Why Evidence Selection Must Come Before AI Investigation
AI security investigations are only as reliable as the evidence behind them. Discover why selecting, validating, and citing relevant evidence before autonomous investigation matters—and how HAWK’s patent-pending ClaimKit supports evidence-grounded security decisions.

Your AI Agent Should Have to Earn More Authority
AI agents should not receive unrestricted authority simply because they can perform an action. Tim Shelton explores progressive autonomy, evidence-based authorization, runtime enforcement, continuous evaluation, and why agent permissions must be capable of expanding—or contracting—as operational conditions change.

AI Guardrails vs. Policy-in-Code: Why Both Matter
AI guardrails and policy-in-code solve different security problems. HAWK Network Defense explains why safe AI-generated responses do not establish authorization, how runtime controls govern agent actions, and what enterprise leaders should require to maintain accountability over autonomous operations.

The AI Insider May Not Be Human
The next insider threat may not be human. AI agents can use legitimate credentials and approved tools while taking actions outside their intended authority. HAWK Network Defense examines non-human identity security, least-privilege permissions, enforceable authorization, continuous governance, and why a valid identity does not guarantee a valid action.

The Most Dangerous AI Permission Is the One Nobody Remembers Granting
AI agents rarely begin with unlimited authority. Their effective permissions expand as integrations, credentials, APIs, and delegated workflows change. Tim Shelton examines permission drift, cumulative capabilities, temporary access, continuous authorization reviews, and why runtime enforcement must reflect what an agent can actually do—not merely what was approved at deployment.

Agentic AI Changes the Control Problem
Agentic AI changes enterprise security by giving AI systems the ability to act, not just respond. Tim Shelton examines the difference between capability and authority, why prompts cannot replace enforceable controls, and how runtime authorization, human oversight, and continuous authority management help govern autonomous operations.

More AI Will Not Fix a Poorly Designed SOC
Adding AI does not automatically fix fragmented security operations. Tim Shelton examines how disconnected tools, unreliable context, unclear response authority, and inefficient workflows can limit the value of SOC automation—and why organizations must redesign their decision processes before scaling AI.

AI Authority Is Becoming a Business Control
As AI agents move from recommendations to actions, businesses must govern more than access and permissions. David Harris explains why delegated authority is becoming an enterprise control, how bounded autonomy should work, and what CEOs must require for enforcement, accountability, revocation, and business-risk oversight.