

From Cloud Signals to Verified Action
As applications, identities, workloads, and data move across cloud, hybrid, and on-premises environments, security teams face a growing challenge: the evidence needed to understand an incident is often distributed across multiple technologies and environments.
HAWK.io brings that telemetry together into a coordinated security operation—helping teams move from isolated cloud signals to the context, evidence, investigation, and response needed to act.
Turn Cloud Telemetry into Operational Intelligence
HAWK integrates telemetry from cloud platforms and the broader security ecosystem into the HAWK Engine, where security data is normalized, enriched, and analyzed in real time.
Cloud activity can be correlated with endpoint, identity, network, email, threat intelligence, and other security context—giving investigations a broader view of what happened, what is affected, and what should happen next.
Move Beyond Monitoring
Cloud security should not stop with visibility or another alert.
HAWK combines real-time analytics, contextual enrichment, evidence-driven investigation, and policy-governed action to move security operations from detection through investigation, decision, containment, and verification.
Octopus cAI uses the available intelligence and evidence to investigate suspicious activity and coordinate authorized action within customer-defined policies, authority, thresholds, and escalation boundaries.
The result is a security operation designed to reduce the time between signal and action while keeping security professionals at the helm of consequential decisions and exceptions.
Detect | Enrich | Investigate | Decide | Contain | Verify
Security That Moves with Your Cloud
As cloud environments expand and change, security operations need to move with them. HAWK helps maintain a consistent security operating model across cloud, hybrid, and on-premises environments—without creating separate workflows or security silos for each environment.
Extend the Security Investments Already in Place
HAWK works with the cloud and security technologies already deployed across the environment, allowing existing investments to contribute telemetry and context to a broader security operation rather than requiring a replacement strategy.
Connect Security Across Environments
Bring cloud, endpoint, identity, network, email, threat intelligence, and other security context together so activity can be evaluated across the environment instead of as isolated events.
Maintain Operational Consistency
Apply coordinated investigation, evidence, decision, response, and verification processes across cloud, hybrid, and on-premises environments—giving security teams a more consistent way to operate as infrastructure changes.
Scale Security Operations with the Environment
As workloads, services, users, and cloud environments grow, HAWK provides a scalable security operations foundation designed to expand without requiring operational complexity and manual processes to increase at the same rate.
Connect the Environment | Maintain Context | Coordinate Operations | Scale with Confidence
Security Across Hybrid Environments
Follow the Incident Across Infrastructure Boundaries
Security incidents do not remain neatly contained within cloud, on-premises, or private infrastructure. Activity can move across identities, endpoints, workloads, networks, and services—making investigations more difficult when security operations are divided by environment.
HAWK helps security teams maintain context as activity moves across those boundaries.
Investigate Across the Environment
Correlate security activity across on-premises infrastructure, private cloud, public cloud, endpoints, identities, networks, and other connected security technologies to build a broader understanding of an incident.
Preserve Context Across Boundaries
Evidence and investigation context can follow the incident across environments, helping analysts understand how activity is connected rather than investigating each system or location independently.
Coordinate Response Wherever the Incident Moves
Investigation, decision, containment, response, and verification can be coordinated across the environment within customer-defined policies, authority, thresholds, and escalation boundaries.
Operate as One Security Environment
HAWK helps reduce the operational boundaries between cloud and traditional infrastructure so security teams can investigate and respond based on the incident—not where the affected system happens to reside.
Follow the Activity | Preserve the Context | Coordinate the Response | Verify the Outcome
Consistent Security Across
Multi-Cloud Environments
Organizations increasingly operate critical workloads across multiple cloud providers, creating a security challenge that extends beyond visibility. Security teams need to correlate activity, maintain context, investigate incidents, and coordinate response across cloud environments without creating separate security operations for each provider.
Operate Across Multiple Cloud Providers
HAWK provides a consistent security operations approach across heterogeneous cloud environments, allowing security teams to work across AWS, Microsoft Azure, Google Cloud, and other connected infrastructure without creating provider-specific security silos.
Normalize Security Telemetry
Telemetry from different cloud environments can vary significantly in format, structure, and context.
The HAWK Engine normalizes and enriches incoming security telemetry so activity can be analyzed and correlated across providers as part of a broader security operation.
Connect Activity Across Clouds
An incident affecting one cloud environment may have related activity in another.
HAWK brings cloud telemetry together with endpoint, identity, network, threat intelligence, and other security context to help teams understand relationships across environments rather than investigating each cloud independently.
Coordinate Investigation and Response
Investigation, evidence, decision, containment, response, and verification can be coordinated across cloud providers within customer-defined policies, authority, thresholds, and escalation boundaries.
Reduce Multi-Cloud Operational Complexity
The objective is not another cloud-specific security silo.
HAWK provides a consistent operating model across cloud environments—helping security teams reduce fragmented workflows while maintaining the context needed to investigate and respond as infrastructure becomes more distributed.
Connect the Clouds | Normalize the Telemetry | Correlate the Activity | Coordinate the Response
Turn Cloud Security Challenges into Operational Outcomes
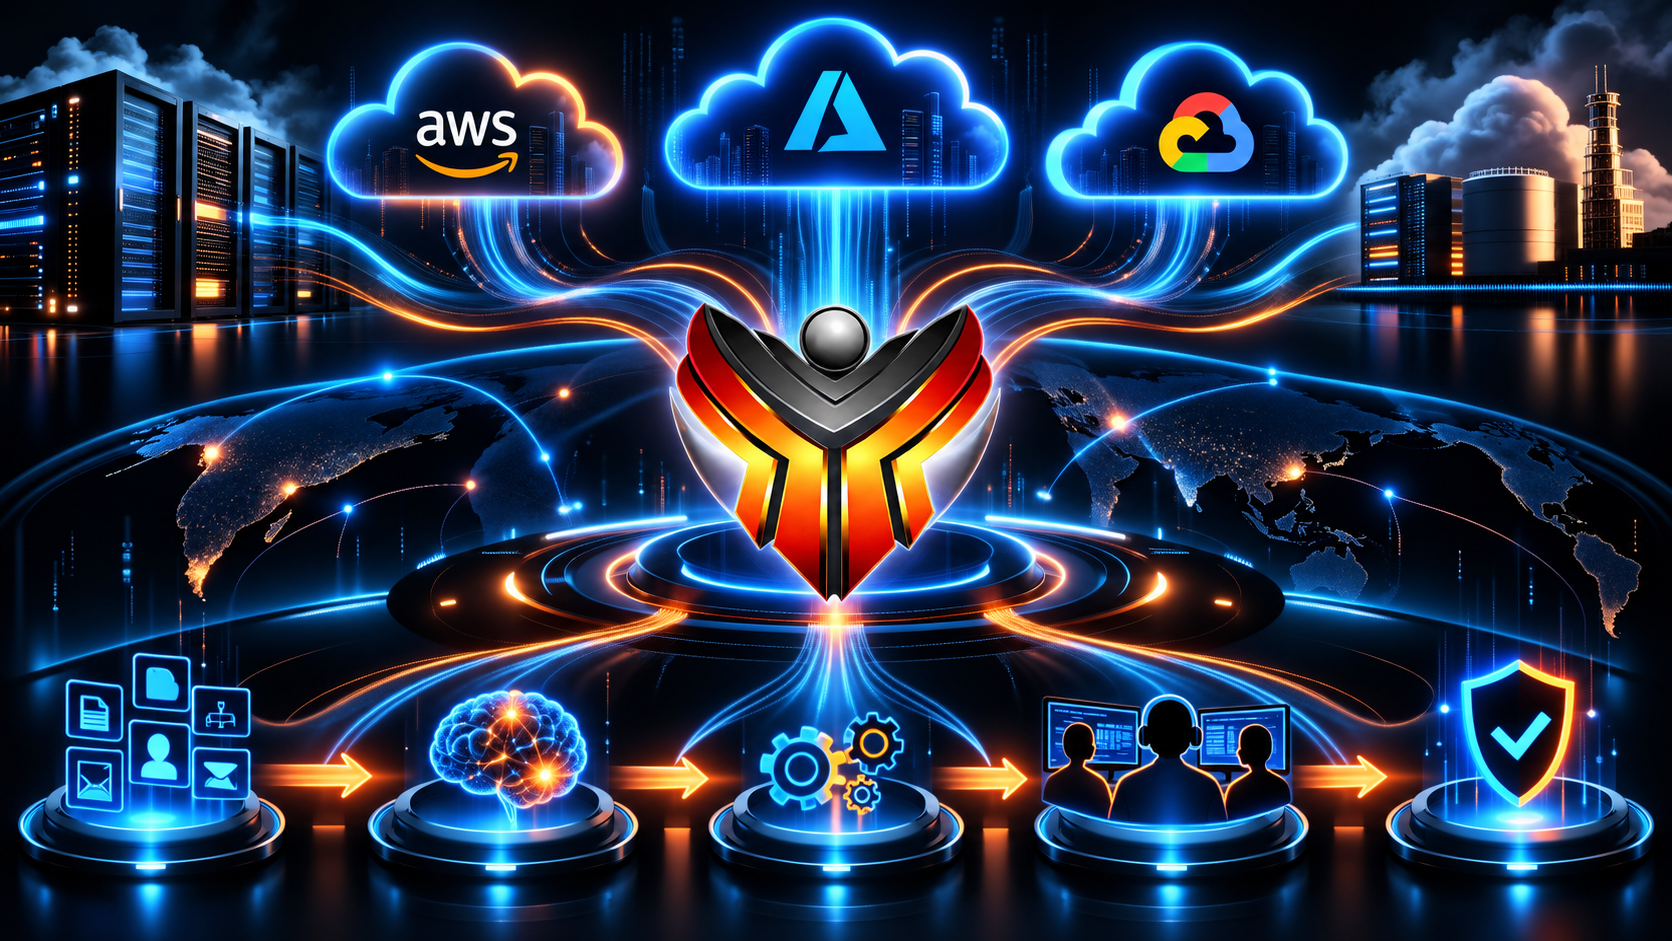
HAWK extends security operations across cloud, hybrid, multi-cloud, and on-premises environments—bringing together telemetry, context, evidence, investigation, decision, response, and verification without requiring organizations to replace the security technologies already in place.
Extend the Security Investments You Already Have
HAWK works with existing endpoint, identity, network, cloud, email, threat intelligence, and other security technologies, allowing those investments to contribute telemetry and context to a coordinated security operation rather than requiring a rip-and-replace strategy.
vTTAC complements existing EDR by extending host-based context where additional endpoint visibility is needed.
Turn Telemetry into Investigation-Ready Context
The HAWK Engine ingests, normalizes, enriches, and analyzes security telemetry in real time, helping connect activity across cloud providers and the broader security environment.
Instead of leaving teams to assemble information manually across disconnected systems, HAWK helps establish the context needed to understand what happened, what is affected, and what should happen next.
Move From Detection to Verified Response
HAWK coordinates real-time analytics, investigation, evidence, decision, containment, response, and verification across the security operation.
Octopus cAI uses available intelligence and evidence to investigate suspicious activity and coordinate authorized action within customer-defined policies, authority, thresholds, and escalation boundaries.
Preserve the Evidence Behind the Incident
Security telemetry and incident evidence can support investigation, post-incident analysis, reporting, compliance requirements, and continuous security improvement—providing a more complete operational record from detection through verified outcome.
Human Expertise When You Need It
HAWK Concierge Services provide access to experienced security and incident-response professionals when investigation, escalation, guidance, or complex response requires additional human expertise.
Scale With Greater Operational Predictability
HAWK is designed to help security operations expand across increasingly distributed environments without requiring manual processes and operational complexity to grow at the same rate.
Connect the Telemetry | Establish the Context | Investigate with Evidence | Coordinate the Response | Verify the Outcome